Another day, another reminder that trust has limits. |
Today's news has me watching an alleged university hack, government code flaws, and millions of emails stolen. - Ken Missed a newsletter? Read past issues here. |
|
|
|
Here’s what you need to know: |
|
|
|
Ransomware Gang Claims 1 Million SSNs Stolen From Vanderbilt |
Ransomware group BYOD claims to have stolen more than 1 million Social Security numbers and other sensitive data from Vanderbilt University. The university has not confirmed the group's involvement or alleged theft, and several services remain restricted as investigators assess the intrusion. |
My Take: Restoring systems is only half the battle. Organizations must identify and close attacker entry points before bringing services back online to prevent reinfection. Review privileged activity and suspicious data transfers, and revoke compromised access before restoring services. |
2.2 Million Emails Stolen in SEGA Vendor Breach |
A breach at SEGA's newsletter provider ARARA exposed approximately 2.2 million email addresses. The broader breach affected over 81 million email addresses, with additional subscriber information exposed in more than 92,000 SEGA records.
My Take: I think this incident highlights the importance of limiting how much customer data third-party providers retain. Review third-party data access, restrict bulk exports, and monitor unusual email sending activity. |
Researcher Finds 100+ Security Flaws in UK Government Code |
A researcher found over 100 vulnerabilities in UK government software code. The findings also included an exposed Microsoft Entra ID credential and excessive SharePoint and OneDrive access.
My Take: Although these issues have been fixed, they reinforce the importance of verifying that remediation closes the underlying attack paths. Scan repositories for exposed credentials, revoke compromised secrets, and enforce least privilege across application integrations. |
|
|
|
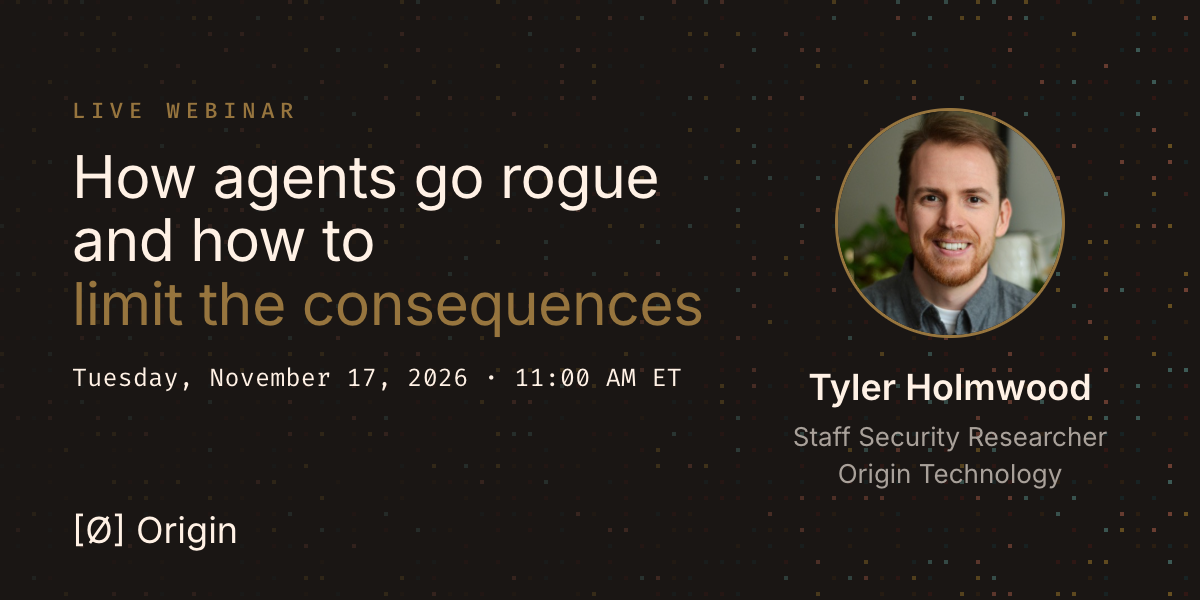
An AI agent doesn’t need an attacker to go rogue
An agent can do something risky with legitimate access. It might follow instructions planted in a web page or a tampered skill, or take a routine task further than anyone intended.
On Tuesday, November 17 at 11 AM Eastern, join Origin researcher Tyler Holmwood to follow real traces of how agents go off course. See what they were asked to do, which instructions they followed, and where they crossed a line. Leave with practical steps for reviewing agent access and using existing controls to limit the consequences. |
|
|
|
Binance Warns of iOS Flaw Threatening Crypto Wallet Data |
Researchers found an iOS flaw that could let malicious apps access other apps’ files and expose cryptocurrency wallet secrets. The researchers released a PoC, but no exploitation in the wild has been confirmed as of publication. |
My Take: I think this highlights why organizations shouldn't rely solely on application sandboxing for protecting data.
Use MDM to enforce iOS updates, block untrusted apps, and verify encryption of sensitive application data. |
Black Kite Finds Critical Flaws in 34% of AI Vendors |
A Black Kite study found critical unpatched vulnerabilities at 34.2% of AI companies worldwide. Additionally, 9.8% had vulnerabilities listed in CISA's Known Exploited Vulnerabilities catalog.
My Take: These findings reinforce the need to assess AI supplier access and your ability to contain a vendor compromise. Review AI vendor permissions, limit system access, and prepare to revoke compromised connections. |
|
|
|
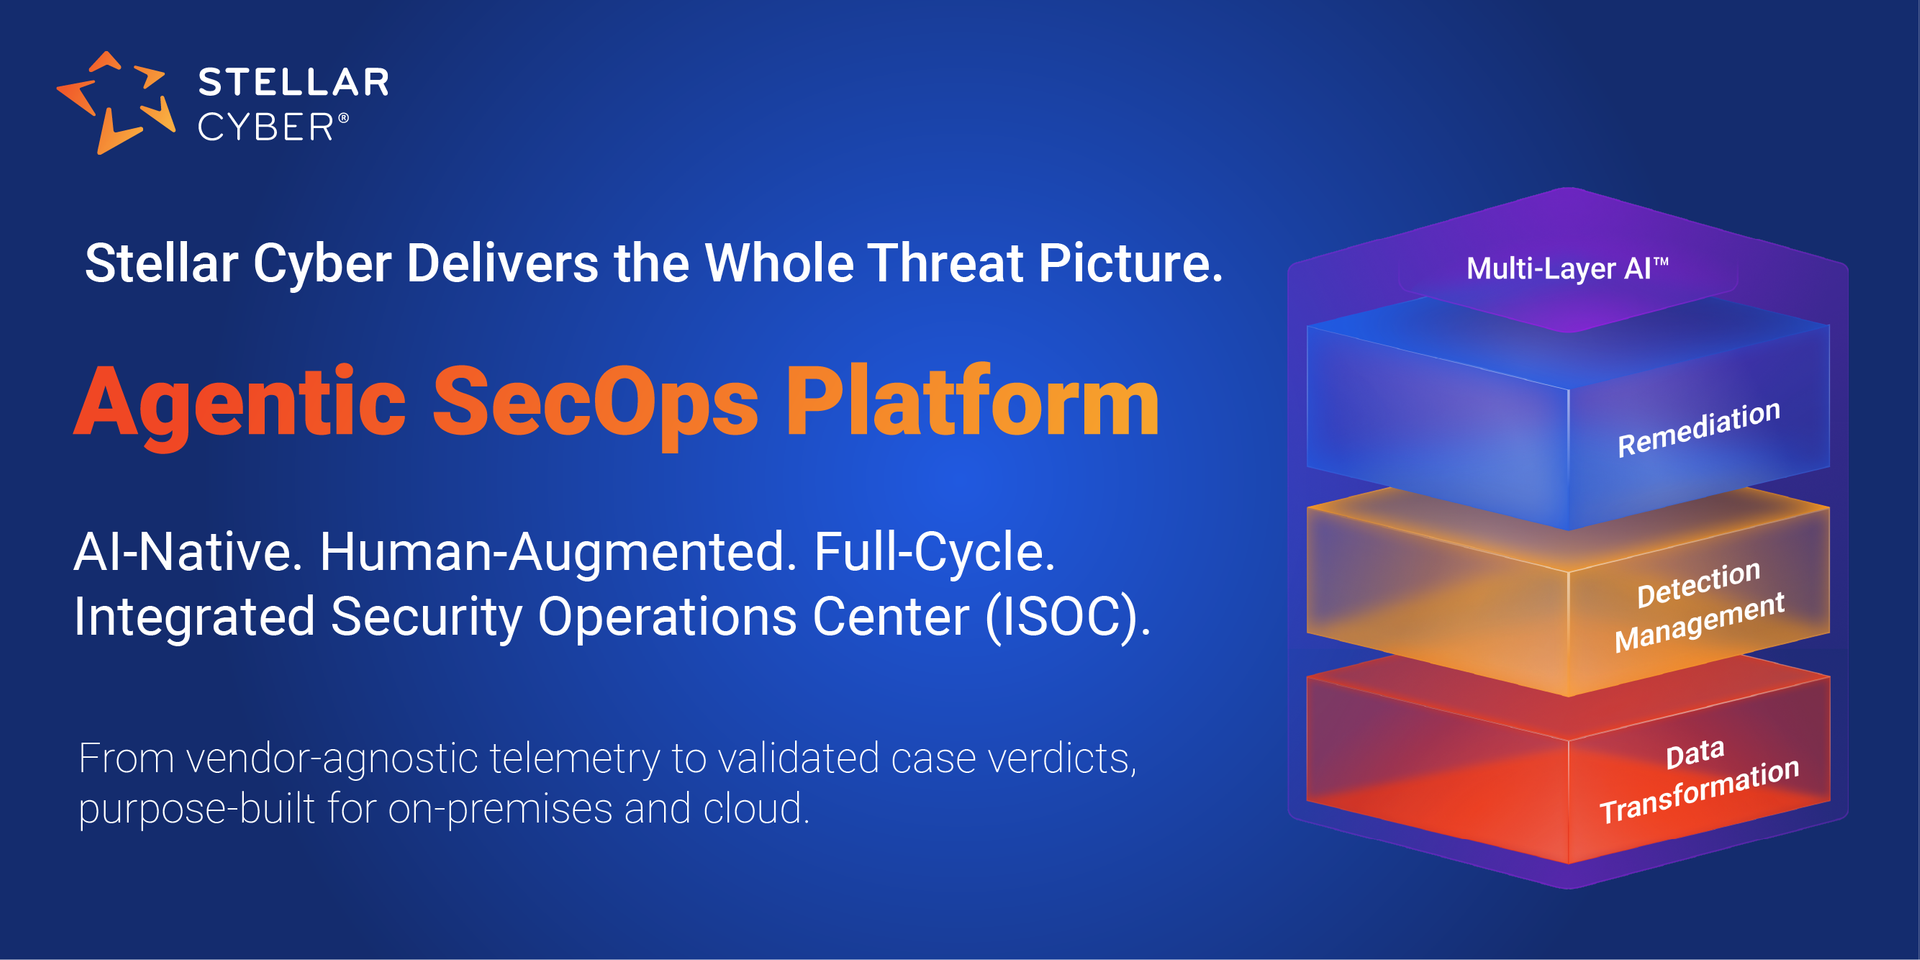
Stellar Cyber's Integrated Security Operations Center (ISOC) Platform offers full-cycle, AI-Native, human-augmented threat detection and response. Streamline your operations now with an Agentic SecOps Platform that will change how your security ecosystem operates. |
|
|
|
AI-generated code can accelerate development, but organizations must still follow secure coding practices to identify vulnerabilities and protect applications before deployment. |
- Use DevSecOps tools to scan human-written and AI-generated code for vulnerabilities and identify insecure third-party dependencies.
-
Validate application inputs, store credentials in secure vaults, and enforce least privilege to prevent unauthorized access.
- Require security-focused code reviews and automated testing before deploying new or updated applications.
|
Track pre-deployment security check pass rates and critical vulnerability remediation times to measure secure development. |
|
|
|
Security Tools You Can Use |
|
|
|
A developer accidentally publishes a live credential. What happens next? |
|
|
|
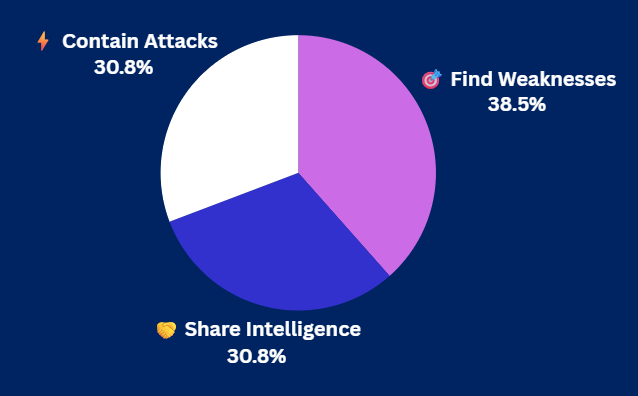
Yesterday's Pulse Check Results |
You control the next security investment. What gets funded first? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|