Attackers aren't waiting for security teams to catch up. |
Today, I'm watching threat actors manipulate refrigeration systems at French blood banks while new CrowdStrike research shows attackers exploiting vulnerabilities within minutes. - Ken Missed a newsletter? Read past issues here. |
|
|
|
Here’s what you need to know: |
|
|
|
DigiCert Leak Exposes Customer IDs and Personal Data |
DigiCert confirmed that attackers accessed customer information and identity documents, including passports and driver’s licenses. The breach involved an internal archive left publicly accessible for over 16 months following a 2025 infrastructure migration. |
My Take: What concerns me is that DigiCert initially treated unauthorized account creation as a registration issue rather than a potential data breach.
Test access permissions after infrastructure changes and monitor for unauthorized account creation or unusual file access. |
Hackers Tamper With Refrigerators at French Blood Banks |
Threat actors compromised a third-party refrigeration provider and manipulated temperature and defrosting settings at three French blood bank facilities. Monitoring systems detected the unauthorized changes before stored plasma was damaged, allowing staff to intervene and relocate supplies. My Take: This incident shows the value of continuous monitoring and layered controls. Restrict vendor access, independently monitor equipment changes, and test incident response procedures. |
Google Patches 213 Chrome Flaws, Seven Critical |
Google patched 213 Chrome vulnerabilities, including 7 critical and 77 high-severity flaws. Several flaws could enable malicious code execution, although Google has reported no active exploitation.
My Take: What interests me is the growing role of AI-assisted vulnerability research, with Claude and Codex Security credited in this release. And I’m concerned that security teams are already overloaded with patch backlogs. Set risk-based patching deadlines for browsers, track time to remediation, and escalate critical vulnerabilities that exceed those deadlines. |
|
|
|
Chainalysis Breach Puts User Accounts at Risk |
Chainalysis disclosed a breach exposing user data, including password hashes and live tokens, with possible unauthorized account access. The service shutdown disrupted cryptocurrency screening, potentially creating compliance gaps for financial institutions. |
My Take: This incident makes me question whether financial institutions have adequate contingency plans for critical vendor outages.
Verify token and session revocation, rotate API keys, and review transactions for suspicious activity. |
CrowdStrike Finds Hackers Exploiting Flaws Within 35 Minutes |
CrowdStrike researchers found that attackers exploited a vulnerability just 35 minutes after public PoC code became available. The study also found that 91% of observed exploited vulnerabilities with public PoCs were attacked within 48 hours of publication. My Take: One of my concerns is if organizations can identify exposed systems and deploy temporary protections before attackers exploit them. Measure the time between public exploit disclosure and risk mitigation, and establish escalation thresholds for delays. |
|
|
|
Could Your Vendors Be Your Weakest Link? |
Third-party vendor access supports maintenance but can expose critical systems to manipulation and disruption if compromised. |
How to reduce third-party risk: |
- Use third-party risk management solutions to assess vendor security and continuously monitor risks.
-
Enforce least-privilege access and MFA, and segment critical systems to limit exposure.
- Monitor vendor activity for suspicious changes and establish procedures to revoke access and maintain operations during breaches.
|
Security teams should track vendor risk scores, access violations, and time to remediate third-party security gaps. |
|
|
|
Security Tools You Can Use |
-
Explore how DSPM helps CISOs prioritize critical exposures, guide remediation, and measure risk reduction across cloud, on-premises, and hybrid environments. Read the Article
-
Start your cybersecurity career for free — enroll in Microsoft’s 9-course Analyst Certificate series on Coursera today.
- Build hands-on AI security skills for less — save 30% on TryHackMe with code TECHADVICE30.
|
|
|
|
Would you detect a vendor changing critical system settings? |
|
|
|
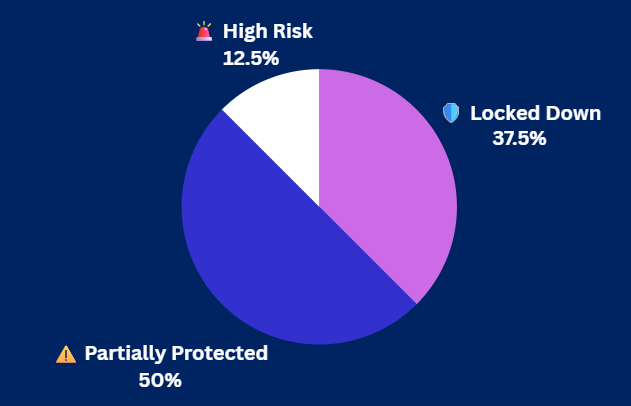
Yesterday's Pulse Check Results |
How Secure Are Your Mobile Devices? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|