Just because a system is patched doesn't mean it's safe. |
That's one of the concerns running through today's news. I'm also watching how AI is changing the way attackers operate and over 200 fixes from Google. - Ken Missed a newsletter? Read past issues here. |
|
|
|
Here’s what you need to know: |
|
|
|
Harvard Data Breach Hits 851,000 Email Addresses |
Nearly a year after Harvard's 2025 breach, Have I Been Pwned identified approximately 851,000 exposed email addresses. The records included donor histories and personal details that attackers could exploit for impersonation and targeted phishing. |
My Take: I think this breach raises an important question about how organizations verify someone's identity. When attackers have access to donation histories and family details, traditional verification questions become less reliable. Restrict bulk donor data exports and independently verify sensitive account or payment changes. |
Google Patches 216 Android Vulnerabilities, Including RCE |
Google's November 2026 Android security update fixes 216 vulnerabilities, including a RCE flaw requiring no user interaction. Other fixes address privilege escalation, information disclosure, and a denial-of-service flaw that could disrupt emergency calls.
My Take: Different manufacturer and carrier update schedules can make it difficult for security teams to maintain consistent protection across company-issued mobile devices. Use MDM tools to monitor patch compliance, enforce security updates, and restrict corporate access until vulnerable devices are patched. |
CISA Flags Actively Exploited WordPress RCE Flaw |
CISA added WordPress Core vulnerability CVE-2026-119977 to its Known Exploited Vulnerabilities catalog following reports of active exploitation.
The flaw allows unauthenticated RCE during certain Core upgrades, exposing websites to potential compromise while administrators install security updates. My Take: Security teams should require evidence of both successful remediation and a compromise assessment before considering the issue resolved.
Apply the patch, review upgrade logs for suspicious activity, and check for unauthorized files or administrator accounts. |
|
|
|
Governance at the speed of AI
Questions about how your business is governing AI are coming in fast. Join our AI governance webinar series live or on-demand to prepare for what customers, auditors, and your board are already asking. Webinar schedule |
-
Nov 17: Govern AI and Close Bigger Deals, the Startup Edition
- Nov 19: Your toughest AI Governance Questions vs our GRC Experts
|
Register for both or pick the session that fits your needs and join live or on-demand. |
|
|
|
Hacker's AI Army Targets Emergency Services in Taiwan |
A threat actor used AI agents to target organizations in 11 countries, compromising systems and exposing sensitive data in Taiwan. This incident demonstrated how AI enables individual attackers to operate at scale. |
My Take: What concerns me most is that these attacks relied on well-known weaknesses, including exposed APIs and SQL injection.
Eliminate default credentials, secure public-facing APIs, and monitor for automated scanning and exploitation attempts. |
Nearly 1,000 Zyxel Switches Hacked Despite Patch |
A zero-day flaw in some Zyxel GS1900 switch models allows unauthenticated local attackers to execute system commands despite June's security patch. Researchers linked the exploit to attacks compromising 996 switches across 48 countries, potentially exposing configurations and credentials.
My Take: I’m concerned that a compromised switch could give attackers a foothold inside the network while remaining outside routine endpoint monitoring. Install Zyxel’s model-specific Patch 3 firmware, restrict switch management access, and monitor for unauthorized configuration changes. |
|
|
|
Can You Keep Up With Vulnerabilities? |
How to reduce your vulnerability exposure: |
- Use vulnerability management solutions to discover assets, scan for vulnerabilities, and identify security gaps.
-
Establish a vulnerability management policy to prioritize exploited flaws, set remediation deadlines, and accelerate patching.
- Validate fixes and monitor emerging threats by rescanning systems and investigating signs of exploitation.
|
Track remediation backlogs, enforce escalation deadlines for critical vulnerabilities, and measure how quickly fixes are verified and deployed to production. |
|
|
|
Security Tools You Can Use |
|
|
|
How Secure Are Your Mobile Devices? |
|
|
|
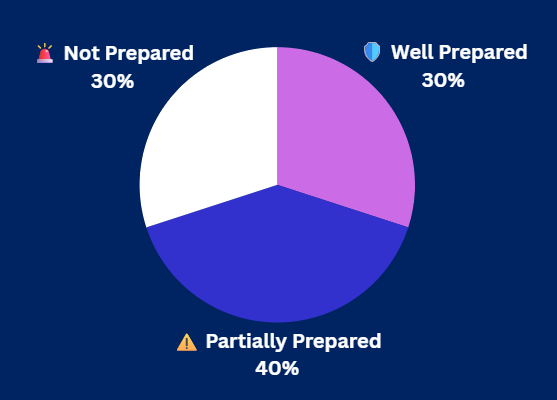
Yesterday's Pulse Check Results |
Ransomware Reality Check: Could your defenses stop an attack? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|