Cybersecurity teams have plenty to think about. |
Today, I'm watching a string of data exposures, a banking disruption, and ransomware hitting a school in the UK. - Ken Missed a newsletter? Read past issues here. |
|
|
|
Here’s what you need to know: |
|
|
|
Nearly 90,000 Exposed in Law Firm Attacks |
Social engineering attacks at Baker McKenzie and Troutman Pepper Locke exposed nearly 90,000 people’s personal information. Neither firm reported unauthorized system access, suggesting attackers obtained confidential documents by deceiving employees. |
My Take: Employees may have legitimate reasons to access confidential files, but external transfers should require additional verification.
Require independent verification of sensitive file transfers and use DLP tools and policies to flag unusual external sharing. |
Suspicious Activity Disrupts Sageworks Banking Services |
Abrigo shut down its Sageworks lending platform after detecting suspicious activity, disrupting services for U.S. banks and credit unions. Most services resumed by November 2, but borrower-facing functions remained down, with no confirmed cyberattack or breach. My Take: I think the bigger concern for banks is whether loan records remained accurate during the outage. Reconcile loan applications, verify records, and test borrower workflows before resuming operations. |
3AM Ransomware Hits UK School |
A 3AM ransomware affiliate encrypted 37 computers at a UK school after stealing credentials and linking three separate Active Directory domains. Bitdefender researchers identified unusual command patterns suggesting possible AI assistance, although its involvement remains unconfirmed.
My Take: I think the focus on possible AI involvement risks overshadowing a more important concern. Attackers were able to expand their access by manipulating trust relationships that should have been tightly controlled. Audit domain trusts, limit privileged access, and monitor Active Directory changes to prevent lateral movement. |
|
|
|
AI has made producing convincing, personalized attacks at scale cheap and easy. DeleteMe & 451 Research surveyed 303 security leaders to understand how AI has changed the nature of social engineering attacks and how organizations are responding. Three key findings |
- 9 in 10 say AI has increased the success rate of social engineering and impersonation attacks.
- 9 in 10 say publicly available employee data increases their exposure to those attacks.
-
1 in 2 are investing in PII removal services this year to reduce their organization’s risk.
|
|
|
| Frontline Education Breach Exposes 1.3 Million People |
Threat actors exploited a third-party software flaw to breach Frontline Education, potentially exposing 1.3 million people. Compromised records included Social Security numbers and government identification details of students and school employees across multiple districts. |
My Take: I think schools need to know exactly what information their vendors retain and how long they keep it.
Audit vendor data inventories, enforce retention limits, and require secure deletion of unnecessary records. |
AI Threats Demand More Than Reactive Security |
Agentic AI is challenging traditional security defenses as attacks become more adaptive and automated. Historical incident data remains valuable, but relying on past attacks alone may leave organizations unprepared for emerging threats.
My Take: AI-assisted attack simulations can help find weaknesses, but they need to reflect your actual network configurations and security controls to produce meaningful results. Test detection rules through controlled attack simulations to identify security gaps before expanding AI-driven automation. |
|
|
|
Are You Ransomware Ready? |
Ransomware attacks continue to threaten organizations by encrypting critical systems and disrupting business operations. |
How to reduce ransomware risk: |
- Deploy ransomware protection solutions and EDR tools to detect suspicious activity and prevent encryption.
-
Enforce MFA, restrict privileged access, and segment networks to limit unauthorized access and lateral movement.
- Prioritize patching critical vulnerabilities and maintain tested offline or immutable backups to support recovery.
|
Combining preventive security controls with tested recovery plans helps minimize ransomware damage and business downtime. |
|
|
|
Security Tools You Can Use |
|
|
|
Ransomware Reality Check: Could your defenses stop an attack? |
|
|
|
Yesterday's Pulse Check Results |
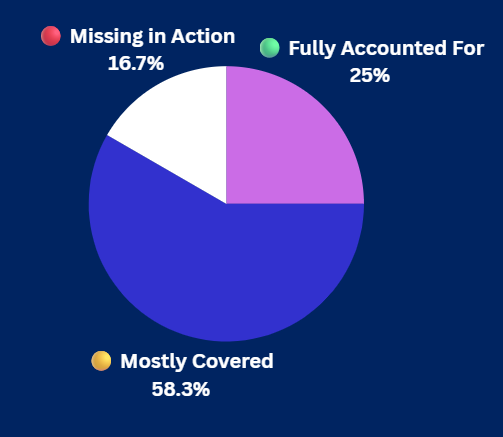
Could you account for every device today? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|