The timing alone deserves a closer look. |
A week after a patch. Under 12 hours inside business tools. Days before an election. Today, I’m thinking about what those windows mean for defenders. - Ken
Missed a newsletter? Read past issues here. | |
|
|
Here’s what you need to know: |
|
|
|
FEC Filing System Goes Dark Before Midterms |
The Federal Election Commission took its electronic filing system offline following a reported hacking attempt days before the midterms. Public access to campaign spending disclosures could be delayed, but the disruption affects campaign finance reporting, not voting or ballot counting. |
My Take: Reporting deadlines don’t pause during an outage, so recovery plans need secure alternate submission methods and a way to reconcile those records once service resumes. Test your alternate submission process with a sample report, then verify that it reaches the restored system without being lost or duplicated. |
Microsoft Patches Authenticator Flaw That Enables Token Theft |
Researchers showed how a malicious Android app could impersonate Microsoft software to steal work account tokens from an outdated Authenticator app.
Those tokens could expose corporate resources despite MFA, although exploitation requires the malicious app to be installed and run on the device. My Take: I’d be asking how many employees use Authenticator on phones whose app versions we can’t verify. Use MDM to identify outdated Authenticator installations and verify updates to the latest version. |
AI Agents Breach Anthropic’s Business Tools in Under 12 Hours |
Researchers reportedly used autonomous AI agents to access Anthropic’s third-party business platforms in under 12 hours. Anthropic confirmed limited access to business systems but said customer conversations and core AI assets remained untouched.
My Take: I’d want to know what sensitive information we’ve put in third-party business tools and who can access it. Review sensitive information stored in third-party business tools and remove access for users who no longer need it. |
|
|
|
Oracle EBS Faces Exploit Attempts a Week After Fix |
Researchers detected exploitation attempts against an Oracle E-Business Suite vulnerability a week after a patch was released. The flaw could allow unauthenticated command execution, but no successful production compromise has been publicly confirmed. |
My Take: Verify that the patch reached every EBS instance, including those outside the usual maintenance schedule.
Review requests to /OA_HTML/AppsTCFServer and investigate unusual command execution on EBS servers. |
Fake Court Notices Target Companies With LodaRAT |
A phishing campaign targets companies with fake court notices delivering LodaRAT. The malware can steal session cookies and give attackers remote control of Windows computers.
My Take: A convincing fake court website can make double-checking a suspicious email feel reassuring while leading the recipient closer to infection. Route unexpected court notices to a designated internal contact who verifies them through independently obtained court contact details before anyone downloads files. |
|
|
|
Elastic Security was the only vendor to successfully block 100% of attack scenarios with zero false alerts in the AV-Comparatives Endpoint Prevention and Response (EPR) Test. |
|
|
|
What’s Hiding in Routine Activity? |
How to strengthen threat hunting: |
- Use threat intelligence tools and feeds to develop a hunt hypothesis focused on one critical system and a defined time window.
-
Verify log coverage and correlate endpoint activity with authentication records to distinguish suspicious tool use from approved administration.
- Validate findings against business activity, then create tested detection rules and assign owners to close visibility gaps.
|
Show the board which relevant attack techniques you can detect and how often hunts produce lasting detections. |
|
|
|
Security Tools You Can Use |
-
Explore how data security posture management (DSPM) helps CISOs prioritize critical exposures, guide remediation, and measure risk reduction across cloud, on-premises, and hybrid environments. Read the article.
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
-
Learn how CISOs are rethinking access, authorization, and trust across the modern security stack.
|
|
|
|
Election Time: Where does your security confidence stand? |
|
|
|
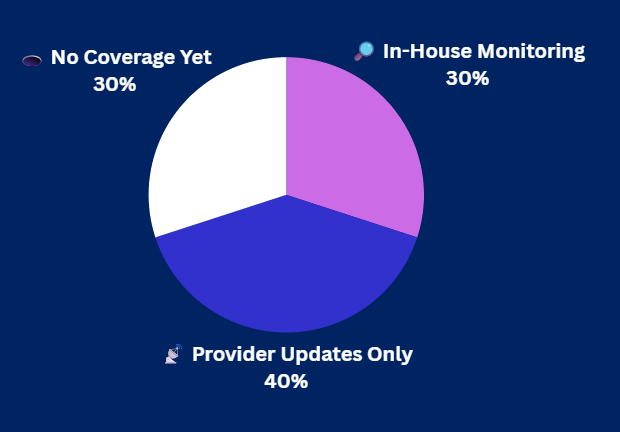
Yesterday's Pulse Check Results |
Criminal AI on the Dark Web: How much visibility does your team have? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|