The consequences don’t always stay on the network. |
Today, I’m looking at what happens when cyber incidents reach the emergency room, the compensation bill, and the cameras behind your firewall. - Ken
Missed a newsletter? Read past issues here. |
|
|
|
Here’s what you need to know: |
|
|
| UNM Cyber Incident Diverts Ambulances, Halts Surgeries |
An incident at University of New Mexico Health diverted ambulances for two hours and suspended outpatient surgeries and appointments. Clinical operations have resumed, but the disruption highlights the need to coordinate containment decisions with neighboring facilities. |
My Take: Restoring connectivity is only part of recovery. Hospitals also need to verify that patient records and medication orders are accurate and critical workflows function correctly before resuming use. Test downtime procedures, assign ambulance diversion authority, and validate clinical data before restoring affected services. |
Japan Cyberattacks Trigger Customer Compensation |
After separate cyberattacks, GMO Internet offered reimbursement for verified unauthorized trading losses, while Park24 offered payouts to eligible breach victims. Both cases show that breach costs can extend beyond restoring systems to addressing customer harm. My Take: Risk assessments should account for what attackers could do with a service’s access and data, even when the service stays online. Restrict access to financial accounts, remove unnecessary stored identity documents, and monitor for unauthorized transactions. |
Criminal AI Tools Accelerate Familiar Attack Tactics |
Resecurity’s 2025 investigation found that DIG AI could generate malicious scripts targeting vulnerable web applications. Subsequent research has documented attackers using AI to automate intrusion tasks and modify malware.
My Take: Automated attacks demand faster containment, so test whether investigation and approval processes delay your response. Simulate credential misuse in an authorized exercise, measure the time to session revocation, and address the longest delay. |
|
|
|
Spoiler: It Wasn’t Luck
Competition’s tough for startups, and everyone needs an edge. Nothing kills a deal faster than showing up without a SOC 2, but audit prep takes time most teams don’t have. Vanta gets you SOC 2-ready fast. See for yourself: |
-
20% shorter enterprise deal cycles
- $1.5M in sales unlocked in 3 months
- SOC 2 Type II readiness in 3 weeks
|
|
|
|
Dahua Cameras Compromised Behind Firewalls |
CERT-UA warned that attackers viewed Dahua camera feeds, changed configurations, and added unauthorized accounts through Easy4IP cloud access. The service can make cameras reachable behind firewalls without directly exposed management ports. |
My Take: Recovery should verify who still has access, since changing passwords alone may leave attacker created accounts in place.
Review camera accounts and cloud connections, remove unauthorized users, and disable remote access features without an operational need. |
Police Say AI-Assisted Hacker Hit 60 Organizations in 44 Days |
Seoul police said a suspected hacker breached 60 organizations in 44 days after adopting AI-assisted tools. The broader campaign exposed more than 8.2 million personal information records, including patient consultation details.
My Take: Extortion samples may reveal only part of a breach, so teams should independently verify the scope of data theft. Test whether you can match a mock extortion sample to internal records and use access logs to investigate wider exposure. |
|
|
|
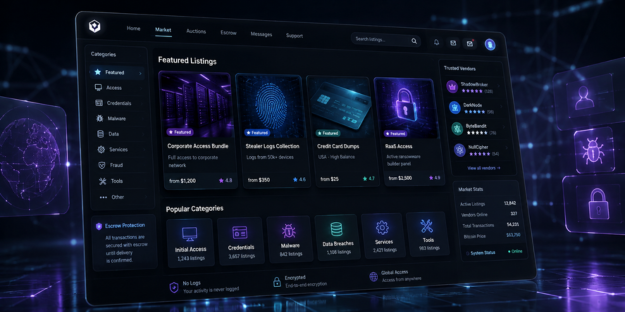
Cybercrime marketplaces sell stolen data and network access that attackers can use for fraud, data theft, and extortion. |
- Use threat intel tools and feeds to flag exposed credentials and access offers, then verify against internal logs.
-
Reset compromised credentials, revoke sessions, rotate exposed keys, and check for credential-stealing malware.
- Enforce phishing-resistant MFA and assign owners to coordinate incident response.
|
Proactive exposure management helps reduce account takeovers and limit the impact of stolen data. |
|
|
|
Security Tools You Can Use |
|
|
|
Criminal AI on the Dark Web: How much visibility does your team have? |
|
|
|
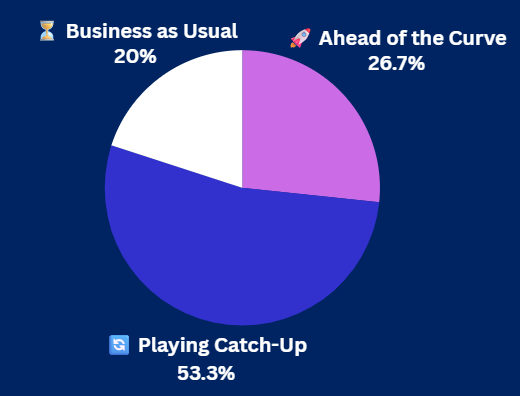
Yesterday's Pulse Check Results |
Has AI changed your patching strategy? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|