Old flaws are finding new life |
Today, I'm watching how AI is changing the game for attackers. Add a major Apple security update, a retailer forced offline, and millions of exposed files… and there's plenty worth your attention. - Ken Missed a newsletter? Read past issues here. | |
|
|
Here’s what you need to know: |
|
|
|
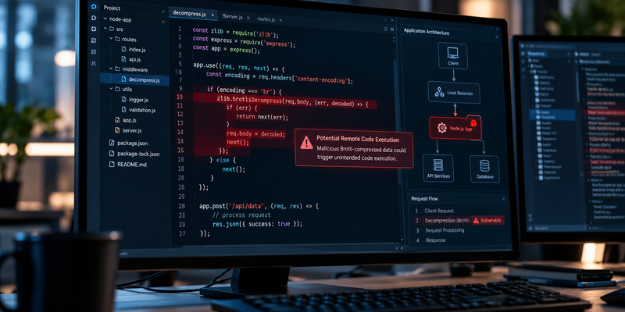
Node RCE Vulnerability Puts Applications at Risk |
Researchers demonstrated a Node flaw, dubbed Node2Shell, that enables remote code execution through malicious Brotli-compressed data. Applications using Express middleware or Node’s built-in fetch() API could be vulnerable even without developers explicitly implementing decompression functionality. |
My Take: One risk here is incomplete remediation, as organizations may update Node while older, vulnerable runtime versions remain active in production environments. Inventory all Node deployments and update vulnerable runtimes, including those in containers and legacy applications. |
Black October Shows AI Making Old Flaws Exploitable |
The PHP2Shell flaws behind cybersecurity's "Black October" show how AI can simplify exploitation of older vulnerabilities. Researchers demonstrated how AI-assisted techniques can adapt exploits across different PHP versions and system configurations. My Take: Exploitation complexity may no longer be a reliable reason to assign a vulnerability a lower priority. Identify vulnerabilities previously deprioritized due to exploitation complexity and test whether existing security controls can prevent exploitation. |
Apple Fixes 163 Security Flaws in Major iOS Update |
Apple patched 163 vulnerabilities, including WebKit and kernel issues that could expose sensitive data or enable malicious code execution. The patches also address an Apple Intelligence flaw that could expose user data to remote attackers, with no known active exploitation reported. My Take: Monitor BYOD devices accessing corporate resources, as delayed iOS updates could leave sensitive business data exposed. Use mobile device management tools to identify outdated devices and enforce minimum OS versions for corporate access. |
|
|
|
Good Smile Company Shuts Store After Data Breach |
Good Smile Company confirmed a store breach that may have exposed customer contact details, purchase histories, and partial payment-card information. Full card numbers and security codes were reportedly unaffected, while the store remains temporarily closed during the investigation. |
My Take: Exposed purchase histories could help attackers craft convincing phishing messages disguised as legitimate order updates or payment requests.
Verify suspicious communications directly through the retailer's official support channels rather than clicking links in unsolicited messages. |
302ai Data Leak Exposes 17.6 Million Files |
Researchers discovered 17.6 million publicly accessible files belonging to AI aggregator 302ai, totaling 22.72 terabytes of data. The exposed files included corporate documents and more than 144,000 private AI chat logs. My Take: Access to trusted AI models doesn't guarantee that third-party aggregators handle data securely. Audit employee use of AI aggregators and verify how vendors store and retain sensitive business data before approving their use. |
|
|
|
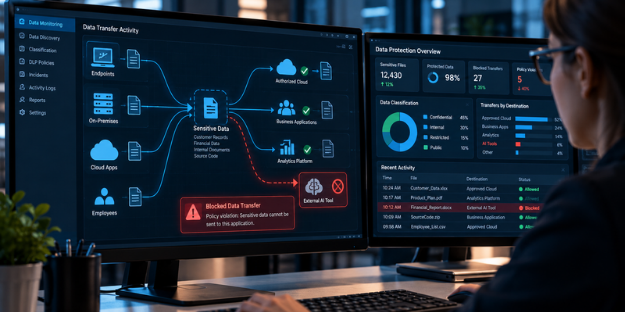
Data breaches continue to expose sensitive information, while growing AI adoption creates new data protection risks. |
How to strengthen data protection: |
- Discover and classify sensitive data to identify confidential information and prioritize protection based on business risk.
-
Deploy DLP tools to monitor sensitive information and prevent unauthorized transfers across cloud applications, endpoints, and AI tools.
- Encrypt sensitive data and enforce least-privilege access to protect information at rest and in transit while restricting access to authorized users.
|
Security teams should regularly assess sensitive data exposure and track mean time to detect (MTTD) and mean time to contain (MTTC) incidents. |
|
|
|
Security Tools You Can Use |
-
Protect your business from threats — get 30% off Bitdefender’s powerful cloud and on-premise protection today.
-
Build hands-on AI security skills for less — save 30% on TryHackMe with code TECHADVICE30.
- Explore the top cybersecurity companies protecting businesses in 2026.
|
| |
|
Has AI changed your patching strategy? |
|
|
|
Yesterday's Pulse Check Results |
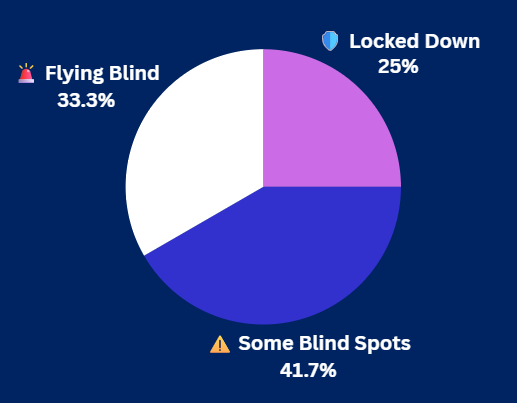
Could an attacker move through your cloud environments undetected? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|