Cyber incidents are hitting where it hurts. |
I'm tracking the ConnectWise attack, federal court disruptions, and the WAF vulnerability being exploited. Just another day at the cybersecurity office. - Ken
Missed a newsletter? Read past issues here. | |
|
|
Here’s what you need to know: |
|
|
|
ConnectWise Attack Exposes Microsoft 365 Accounts |
ConnectWise disabled seven compromised Cloud Backup app identities used to access Microsoft 365 tenants. Huntress confirmed they found unauthorized sign-ins across 162 tenants. |
My Take: You still need to investigate affected tenants for unauthorized credentials, elevated privileges, and other changes that could allow attackers to maintain persistence. Review service principal sign-ins, audit permission changes, and revoke any unauthorized credentials or access. |
Is Your Cybersecurity Brand Ready for Black Friday? |
Black Friday and Cyber Monday are approaching. Will your cybersecurity brand be part of the conversation? Sponsored newsletter placements offer a way to reach potential customers beyond your existing audience.
Available opportunities include Cybersecurity Insider and The Neuron, with more than 700,000 AI-focused subscribers, along with additional newsletters. Not on the marketing team? Share this with someone who handles advertising. View Black Friday sponsorship opportunities.
|
BAE Systems Cyberattack Disrupts US Bankruptcy Courts |
A BAE Systems incident halted U.S. bankruptcy court notices and took related websites offline. The outage shows how third-party incidents can disrupt critical services without directly affecting internal systems. My Take: This incident is a reminder to reassess your TPRM program and test your cyber resilience plans against vendor outages.
Identify critical vendor dependencies, establish acceptable outage durations, and test alternative workflows to maintain operations. |
|
|
|
SiteGuard WAF Vulnerability Gives Attackers Privileged Access
|
Attackers are exploiting a SiteGuard Server Edition vulnerability that allows command execution with root or SYSTEM privileges on affected servers. The flaw affects a statistics feature enabled by default, and the vendor warns that patching could erase evidence of compromise. |
My Take: Prioritize patching based on your actual exposure and existing security controls while preserving forensic evidence.
Preserve SiteGuard diagnostics, investigate potential compromise, and patch or temporarily disable the statistics feature. |
Hackers Exploit Collabora Flaw to Backdoor Nextcloud |
A Collabora vulnerability has enabled attackers to compromise Nextcloud servers by executing commands and planting PHP web shells. The flaw affects the built-in CODE Server app when offline, potentially exposing sensitive files and enabling persistence even after patching. My Take: Map potential attack pathways from the compromised web server account to identify exposed data and opportunities for lateral movement. Upgrade to the latest version, hunt for suspicious PHP files, and review access logs for signs of exploitation. |
|
|
|
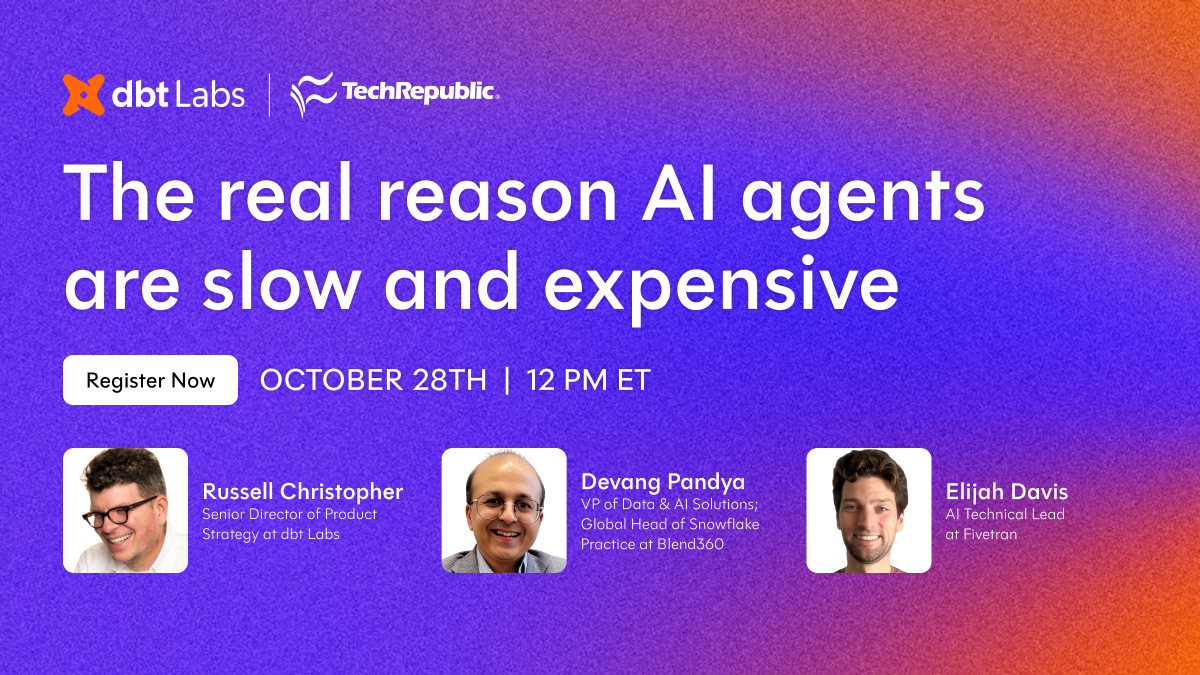
Before scaling AI agents, hear directly from leaders at dbt Labs, Blend360, and Fivetran about the context behind agent costs.
TechRepublic and dbt Labs bring these perspectives together in “The real reason AI agents are slow and expensive” on October 28, 2026, at 12:00 PM ET. Register for this focused, 30-minute panel discussion before your next rollout. |
|
|
|
Is Your Cloud Security Keeping Up? |
Cloud breaches highlight how attackers exploit stolen credentials, misconfigurations, and third-party access to compromise environments. |
How to reduce cloud security risk: |
- Strengthen access controls by enforcing phishing-resistant MFA, least-privilege permissions, and just-in-time access for privileged accounts.
-
Use CNAPP tools to identify cloud misconfigurations, exposed services, excessive permissions, and security vulnerabilities.
- Monitor cloud activity by auditing application identities, third-party integrations, and centralized logs for suspicious access or unauthorized changes.
|
You should be able to report overall cloud risk exposure, remediation progress, and any unresolved security gaps. |
|
|
|
Security Tools You Can Use |
- Earn your cybersecurity degree online at CBU. Develop practical skills through a Christ-centered, NSA-validated Cyber Defense program. Explore the Program.
-
Build your skills — earn your CompTIA CSIE with CySA+, CASP, Security+, and Pentest+ training for 74% off.
-
Think like a hacker — master Web3 security, red teaming, and bug bounty skills with 86% off the Cybersecurity Mastermind Bundle.
|
|
|
|
Could your business survive a vendor outage? |
|
|
|
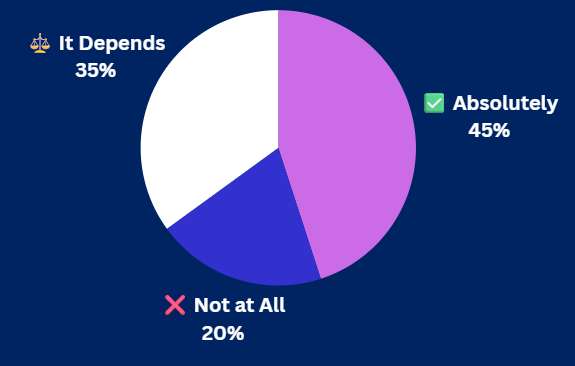
Yesterday's Pulse Check Results |
Should robot makers be liable for misuse? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|