Technology isn't always the weakest link, or the strongest defense. |
I’m looking at human behavior, monitoring gaps, and the unexpected ways AI enters the picture. - Ken Spend less time figuring out AI and more time using it with practical, self-paced courses from The Neuron Academy. Missed a newsletter? Read past issues here.
|
|
|
|
Here’s what you need to know: |
|
|
|
SAP Vulnerability Opens Door to System Takeover |
SAP patched a S/4HANA flaw that could allow privileged users to execute arbitrary code and take control of affected systems. A separate vulnerability, CVE-2026-58249, could let unauthenticated attackers crash SAP services with HTTP/2 enabled. |
My Take: It’s worth reinforcing that vulnerability prioritization should be driven by actual exposure and material business impact, not CVSS scores alone. Audit SAP Fiori permissions, assess HTTP/2 exposure, and prioritize patching affected systems based on business risk. |
Microsoft Disrupts Phishing Network Behind 1B Messages |
Microsoft disrupted a phishing network linked to over 1 billion malicious messages targeting 75,000 organizations across 150 countries. The operation seized domains used to distribute compromised cloud accounts, phishing kits, and impersonation tools.
My Take: Use intelligence from the takedown to identify lingering compromises rather than assuming the disruption eliminates the threat. Review related threat indicators, investigate suspicious cloud account activity, and revoke compromised sessions. |
13.7M Records Found in Unsecured Database |
A researcher uncovered 13.7 million exposed records containing sensitive information in a database. Although access has since been restricted, it's unclear where the records originated or whether they were downloaded. My Take: Restricting access stops further exposure, but the risk remains unclear without knowing who could have accessed the data. Review access logs, investigate potential data exfiltration, and assess whether exposed credentials remain active. |
|
|
|
OpenAI Engineer Arrested in Spying Case |
Authorities arrested an OpenAI engineer accused of planting a hidden recorder in an executive conference room. Prosecutors allege he also used AI to research building the device, but whether it recorded any conversations remains unclear. |
My Take: AI's role on both sides is interesting, but a routine security sweep reportedly uncovered the device. It's a reminder that physical security deserves the same attention as network security. Conduct regular security sweeps of sensitive meeting rooms, restrict access, and investigate unauthorized devices. |
South Korea Breaches Expose 100K Records |
South Korean regulators confirmed breaches at 16 financial firms, exposing roughly 100,000 personal records. A broader review of 555 firms found 130 security gaps, including outdated software and inadequate monitoring.
My Take: The inadequate monitoring makes me wonder: How many threats will go undetected until another major breach occurs? Identify monitoring blind spots, verify alert coverage, and investigate suspicious activity. |
|
|
|
How can your organization verify an employee, contractor, or customer when voices and identities can be convincingly replicated?
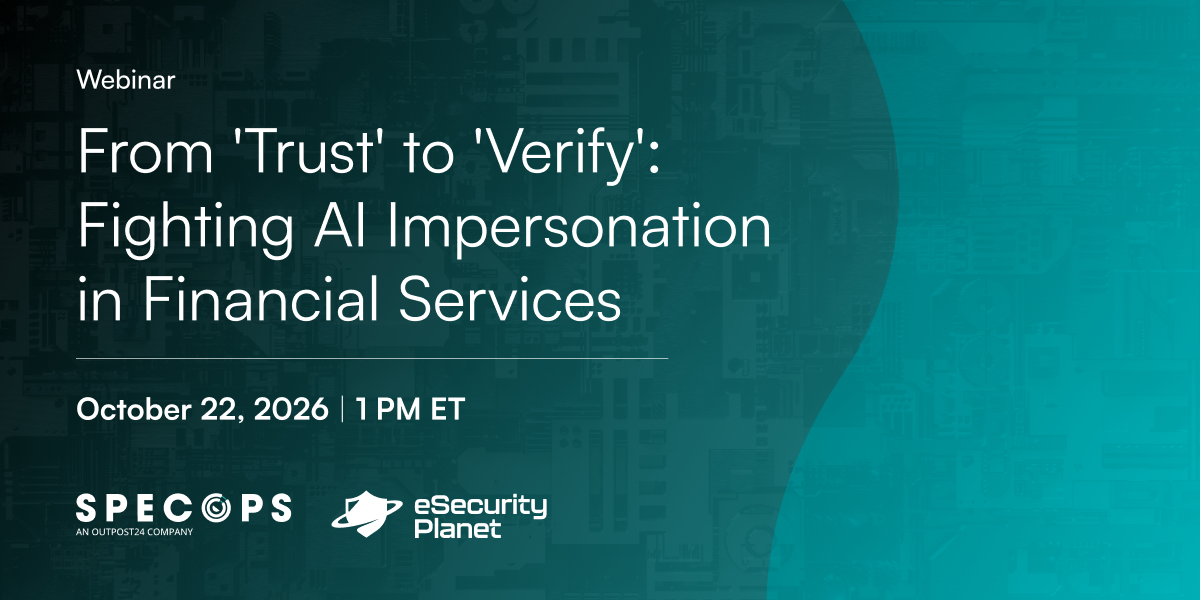
Specops and eSecurity Planet will explore practical approaches during From ‘Trust’ to ‘Verify’: Fighting AI Impersonation in Financial Services on October 22, 2026, at 1:00 PM ET.
Learn where traditional verification falls short and how to establish stronger identity assurance before issuing credentials or making account changes. |
|
|
|
Is Your Data Safe From Insiders? |
Insider threats extend beyond malicious employees to include accidental data exposure, negligent behavior, and misuse of privileged access. |
How to reduce your insider threat risk: |
- Enforce least privilege, regularly audit permissions, and remove unnecessary access.
-
Monitor suspicious activity and use DLP tools to detect and block unauthorized data transfers.
- Strengthen offboarding by immediately revoking access, terminating sessions, and recovering devices.
|
The effectiveness of an insider threat program should be measured by how quickly security teams detect and contain risky behavior, not by the volume of alerts generated. |
|
|
|
Security Tools You Can Use |
-
Think like a hacker — master Web3 security, red teaming, and bug bounty skills with 86% off the Cybersecurity Mastermind Bundle.
-
Protect your business from threats — get 30% off Bitdefender’s powerful cloud and on-premise protection today.
-
Build your skills — earn your CompTIA CSIE with CySA+, CASP, Security+, and Pentest+ training for 74% off.
|
|
|
|
Should companies face hefty fines for unsecured databases? |
|
|
|
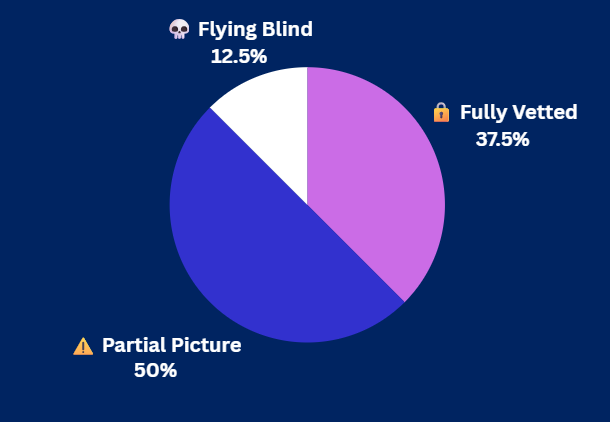
Yesterday's Pulse Check Results |
M&A Risk Check: Could you inherit fines like Microsoft? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|