Some vulnerabilities make headlines. Others make trouble first. |
Today, I'm looking at flaws exploited before public disclosure and a multi-million dollar fine. - Ken
Missed a newsletter? Read past issues here. |
|
|
|
Here’s what you need to know: |
|
|
|
Microsoft Patches 1,400 Flaws, Including Active Zero-Day |
Microsoft's Patch Tuesday fixed over 1,400 vulnerabilities, including an actively exploited Windows vulnerability. The release also fixes critical Outlook flaws that could allow remote code execution without user interaction. |
My Take: With 1,400-plus flaws to triage, I'd prioritize active exploitation and actual exposure over severity scores alone.
Map affected systems to exploitable attack paths, prioritize remediation, and verify fixes across your environment. |
WordPress Plugin Attacked Before Disclosure |
Attackers began exploiting a Bricksforge WordPress vulnerability before public disclosure. The flaw allows unauthenticated attackers to upload and execute malicious PHP code.
My Take: My concern is that threat actors could establish persistence through PHP web shells that remain active even after patching. Patch Bricksforge and inspect upload directories and server logs for web shells or other signs of compromise. |
Microsoft’s Xandr Fined $9.6M Over Grindr Data |
Norway fined Microsoft-owned Xandr $9.6 million for unlawfully processing Grindr user data without a valid legal basis. The violations predated Microsoft's 2022 acquisition and involved sensitive user data.
My Take: I think this case reinforces the importance of reviewing historical privacy practices during M&A due diligence, as regulatory liabilities can emerge years later. Review third-party data practices, verify legal bases for processing, and assess privacy liabilities before acquisitions. |
|
|
|
Experimenting with AI is easy. Turning it into something useful for your daily work takes the right skills.
The Neuron Academy helps you move beyond basic prompts with practical courses on building AI-powered workflows. You can also learn how to create AI agents and apps at your own pace, with guided pathways tailored to what you want to accomplish. |
|
|
|
Google DevSite Vulnerability Exposes Servers to RCE |
A researcher uncovered a Google DevSite flaw that could enable forged sessions and unauthenticated code execution. The vulnerability also affected authentication on four other Google developer sites before being patched. |
My Take: I'd be looking at how many applications share signing keys, because one exposed secret shouldn't give attackers the keys to your kingdom.
Inspect session cookies for exposed credentials, eliminate unsafe deserialization, and rotate compromised signing keys across affected applications. |
Galaxy S26 Hacked Seven Times at Pwn2Own |
Researchers hacked Samsung's Galaxy S26 seven times at Pwn2Own Ireland 2026, exploiting both newly discovered and previously known vulnerabilities. There were no reports of the newly discovered flaws being exploited in the wild at the time of publication. My Take: Seven hacks grab headlines, but I'd focus on which flaws were exploited, available fixes, and how to limit exposure until they're patched. Audit managed Galaxy devices, apply available security updates, and monitor Samsung advisories for new patches. |
|
|
|
Is Your Website an Easy Target? |
Recent WordPress vulnerabilities highlight how attackers exploit weaknesses in website plugins, software, and server configurations. |
How to reduce website exposure: |
- Regularly patch your CMS, plugins, themes, and servers, and deploy a WAF to block malicious traffic.
-
Enforce MFA and least-privilege access, and restrict file uploads to prevent unauthorized code execution.
- Continuously monitor for suspicious activity and maintain tested backups for recovery.
|
Prioritize high-risk websites and verify the effectiveness of existing security controls. |
|
|
|
Security Tools You Can Use |
|
|
|
M&A Risk Check: Could you inherit fines like Microsoft? |
|
|
|
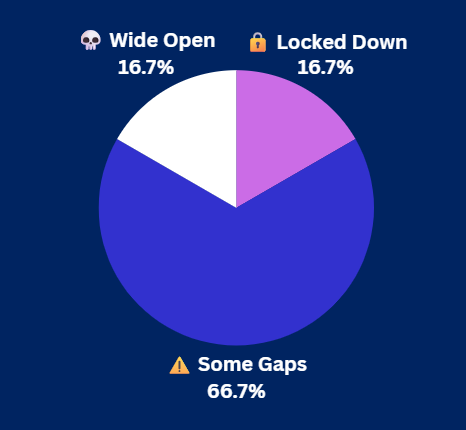
Yesterday's Pulse Check Results |
How protected is your company's data? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|