Security news isn’t always about new vulnerabilities. |
I'm looking at how attackers are putting familiar weaknesses to work and an incident that took an unexpected physical toll. - Ken Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Citrix Patches NetScaler RCE Vulnerability |
Citrix patched a NetScaler vulnerability that could enable remote code execution or denial of service. The flaw affects specific NetScaler ADC and Gateway builds using SAML authentication, although Citrix has reported no known exploitation. |
My Take: I'd want to identify NetScaler appliances using SAML authentication and prioritize vulnerable ones for patching.
Check SAML configurations, install the appropriate Citrix patches, and test authentication functionality after deployment. |
SonicWall Flaw Draws Attacks Within 48 Hours |
Researchers detected over 100 attempts to exploit a critical SonicWall SMA1000 flaw within 48 hours of its patch release. The vulnerability could expose internal services to unauthenticated attackers, although no successful compromises have been reported. My Take: I'd check whether attackers accessed the internal CouchDB service. That could indicate exploitation beyond initial probing. Update affected SMA1000 appliances and review WorkPlace logs for suspicious requests targeting internal services. |
628K Ukrainian Records Stolen by Threat Actors |
CyberXero used Anthropic's Claude Code to automate attacks that stole over 628,000 records from Ukrainian organizations. The attacker deployed up to 51 AI agents, scanning 4,708 targets and deploying 32 web shells in just 61 seconds.
My Take: The speed of these attacks is what stands out to me. AI agents allowed the attacker to exploit familiar vulnerabilities at a scale that could outpace traditional detection and response processes. Patch vulnerable WordPress plugins, scan for unauthorized web shells, and alert on suspicious bulk data exports. |
|
|
|
Cyberattack Spoils Food at French Supermarkets |
Threat actors manipulated refrigeration controls at hundreds of French supermarkets, spoiling food and potentially causing fires. The attack hit major chains, including Intermarché and Netto, showing how OT attacks can cause physical damage. |
My Take: I'd verify that refrigeration systems have independent temperature alerts to detect tampering before equipment damage or inventory losses occur. Segment OT networks, restrict vendor access, update outdated firmware, and implement independent alerts for abnormal equipment conditions. |
FBI Takes Down Flax Typhoon Attack Domains |
The FBI seized seven domains linked to China-backed Flax Typhoon hackers, disrupting tools used for vulnerability scanning and malware delivery. These tools supported attacks on critical infrastructure and universities worldwide, with confirmed breaches at Taiwanese institutions. My Take: Seizing these domains disrupts the attackers' operations, but it doesn't eliminate access they've already established. Review the joint advisory for compromise indicators, unauthorized remote-access tools, and suspicious logins. |
|
|
|
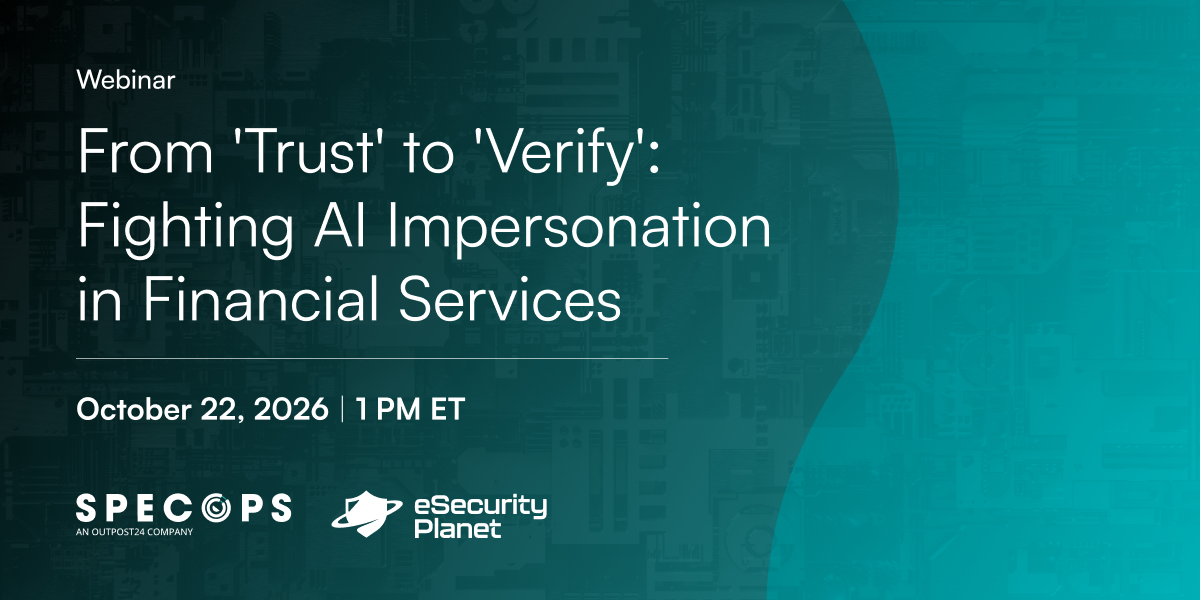
How can your organization verify an employee, contractor, or customer when voices and identities can be convincingly replicated?
Specops and eSecurity Planet will explore practical approaches during From ‘Trust’ to ‘Verify’: Fighting AI Impersonation in Financial Services on October 22, 2026, at 1:00 PM ET. Learn where traditional verification falls short and how to establish stronger identity assurance before issuing credentials or making account changes. |
|
|
|
Is Your OT Infrastructure Secure? |
As industrial systems become more connected, securing operational technology (OT) is critical to preventing costly disruptions and physical safety risks. |
How to reduce OT security risks: |
- Segment ICS networks from IT networks and restrict remote access with MFA.
- Patch vulnerable OT devices and isolate legacy systems that cannot be updated.
- Monitor for abnormal equipment behavior and test recovery procedures to ensure safe restoration.
|
Security teams should work with OT operators to validate critical system protections and confirm recovery procedures before an incident disrupts operations. |
|
|
|
Security Tools You Can Use |
|
|
|
How protected is your company's data? |
|
|
|
Yesterday's Pulse Check Results |
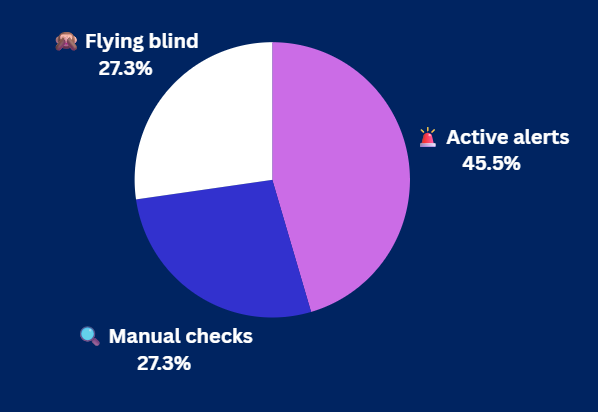
Would you know if attackers moved into your backup server? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|