“Patched” can still leave a few questions unanswered. |
Today, I’m looking at what happens after updates… and before a phone ever leaves its box. - Ken
Want to get more out of AI? The Neuron Academy offers self-paced courses to help you put it to work. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Meraki Devices Face Weeks Without Security Fixes |
Cisco disclosed seven Meraki CVEs affecting six product families, including a 9.6-rated flaw requiring no authentication or user interaction. Some fixes are due in October or November, with no workarounds or known malicious exploitation. |
My Take: I’d check whether guest or unmanaged devices share a network segment with affected equipment because the 9.6-rated flaw requires adjacent-network access. Assign an owner to track fixes by product family and firmware train and verify installed versions after upgrades. |
Cisco Licensing Flaws Require Two Advisory Checks |
Cisco patched License On-Prem, including a 10.0-rated cryptographic signature flaw requiring no authentication or user interaction. The flaws affect the licensing system regardless of configuration, with no workarounds and no exploitation reported in the wild. My Take: I’d check for credentials shared with production systems, since compromising this licensing server could give attackers a path into those systems. Compare the running build against both security advisories and apply the latest fix. |
Attackers Hit Ahsay Backup Servers Despite Patch |
Attackers exploited AhsayCBS backup servers to gain SYSTEM privileges despite the 10.3.4.0 patch. Huntress verified that hotfix 10.3.4.45 blocks initial access, but existing webshells and malicious services may remain.
My Take: I’d verify that we can recover from those backups without using the affected server before relying on them during an outage. Apply the hotfix, reboot, and investigate unexpected processes. |
|
|
|
Hybrid environments mean more flexibility — and more consoles, policies to sync, and gaps to miss. Gateway Load Balancer and FortiGate Next-Generation Firewall consolidate cloud and on-premises security into one dashboard. Get the technical article. |
|
|
|
Bitdefender Finds Malware Baked Into Android Firmware |
Bitdefender found Midnight Mimosa preinstalled in the firmware of some low-cost Android phones before purchase. The malware can silently install apps with system-level privileges, and users cannot remove it through normal uninstall options. |
My Take: I’d review accounts used on an infected phone for suspicious activity rather than assume MFA prevented exposure.
Suspend corporate access for affected phones and revoke their active sessions from a trusted device. |
Anthropic Launches Free AI Bug Hunts for Open Source |
Anthropic launched OSS Scanner, offering eligible open-source projects free AI vulnerability reports without human review. In its broader research, the company found over 29,000 potential flaws in six months but manually reviewed only about 6,000.
My Take: I wouldn’t let AI-assigned severity dictate patch priority without checking how the flaw could impact your business. Assign a triage owner, verify reported flaws, and test patches before applying them. |
|
|
|
How Secure Are Your Mobile Devices? |
Mobile malware and unpatched vulnerabilities can give attackers access to sensitive data and authenticated sessions. |
How to reduce mobile device risk: |
- Approve supported devices from authorized sellers and verify their security patch dates.
-
Require MFA for account access and use MDM compliance policies to restrict access from insecure devices.
- Test your ability to revoke sessions and remotely remove work data from lost devices.
|
Test whether marking a phone noncompliant actually cuts off existing access to company data. |
|
|
|
Security Tools You Can Use |
-
Spend less time figuring out AI and more time using it with practical, self-paced courses from The Neuron Academy.
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
-
Build your skills — earn your CompTIA CSIE with CySA+, CASP, Security+, and Pentest+ training for 74% off.
|
|
|
|
Would you know if attackers moved into your backup server? |
|
|
|
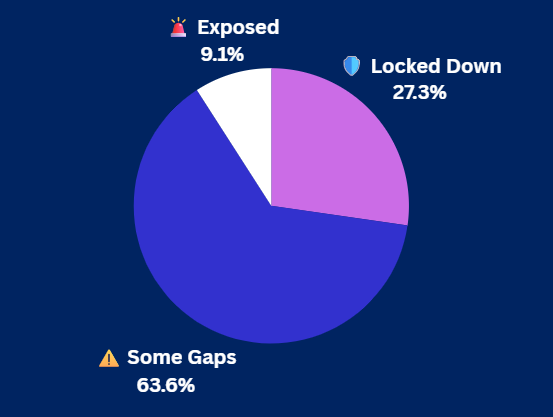
Yesterday's Pulse Check Results |
How secure are your switches and routers? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|