Some attacks deserve a closer look. |
I’m tracking the McKesson incident and how GTA 6 hype is being exploited (love gamers). I’m also digging into a rare glimpse of Russia’s GRU cyber training pipeline. - Ken
Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
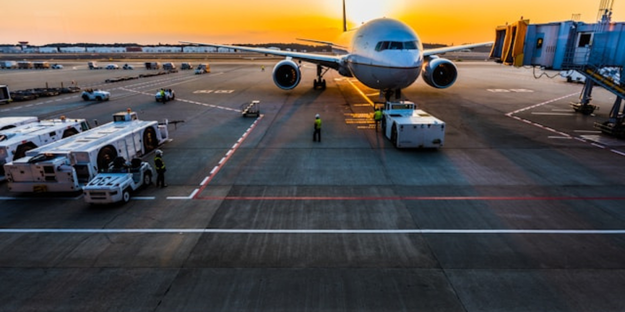
UK Airport Attack Exposes 8.7 Million Customers |
A cyberattack on Manchester Airports Group exposed personal data belonging to about 8.7 million customers across three U.K. airports. The breach did not disrupt flights, but the stolen customer data could fuel targeted phishing and social engineering. |
My Take: The airports stayed operational, but exposing millions of customer records raises questions about whether basic controls, such as data encryption, were adequately implemented here. Segment customer-facing systems from critical environments, encrypt sensitive data, and limit how much information a compromised account or application can access. |
ShinyHunters Claims McKesson Data Theft |
McKesson is investigating a breach of third-party applications, while ShinyHunters claims it stole millions of patient records. The group says vishing attacks compromised employee Okta accounts, providing access to Salesforce and Snowflake, while McKesson confirmed data exfiltration. My Take: I’ve worked healthcare incident response during a ransomware attack that disrupted operations for weeks and ultimately led to a payment. Extortion groups know that when patient care is at stake, the pressure to restore systems quickly can give them leverage.
Use phishing-resistant MFA for SSO accounts and verify employee identities through secondary channels before resetting credentials or changing authentication settings. |
Russian University Records Reveal GRU Cyber Operator Pipeline |
Leaked university records reveal a training program researchers link to GRU units behind APT28 and Sandworm. The curriculum covers offensive and defensive cyber skills, with graduates placed in military units linked to espionage and disruptive operations.
My Take: The structured training pipeline isn’t surprising since Western countries also recruit and train cyber talent from certain universities for intelligence work. What’s more interesting is the visibility this leak provides into how Russia develops personnel for specific GRU units and missions.
Prioritize the attack paths these groups repeatedly exploit by hardening internet-facing systems, enforcing phishing-resistant MFA, and continuously monitoring for suspicious identity activity. |
|
|
|
Your prospects won’t sign without proof of security. A proof of compliance request stalls deals and pulls engineers into audit prep. Vanta gets you compliant fast (SOC 2, ISO 27001, HIPAA+) and keeps you that way. Trusted by 16,000+ companies like Ramp, Harvey, and Writer. |
|
|
|
Fake GTA 6 Demo Drops Vidar Infostealer |
Cybercriminals are exploiting GTA 6 hype with fake Rockstar sites that deliver the Vidar infostealer instead of a game demo. The malware steals browser passwords and session cookies, potentially bypassing two-factor authentication to access accounts. |
My Take: We spend a lot of time protecting the initial login, but an attacker who steals a valid session token may be able to sidestep those controls entirely.
If an infostealer is detected, change passwords, revoke active sessions and tokens, and remove unfamiliar devices from a clean device. |
Agentic AI Helps SOC Teams Do More With Less |
Understaffed SOC teams are using agentic AI to automate repetitive investigations and increase capacity without adding headcount. AI can gather evidence and context, helping less-experienced analysts investigate incidents without relying on senior staff.
My Take: As someone who has worked on a small IR team, I think the real value of agentic AI is scaling SOC expertise while keeping experienced analysts focused on decisions that require human judgment. Document investigations that consume senior analyst time, automate repeatable evidence gathering, and require human approval for disruptive actions. |
|
|
|
Turn Threat Intelligence Into Action |
Threat intelligence helps security teams identify relevant threats, prioritize risk, and act before attackers gain a foothold into organizations. |
How to make threat intelligence actionable: |
- Prioritize relevant threats by tracking likely threat actors, active vulnerabilities, and techniques that matter most to your environment.
-
Use threat intelligence solutions to enrich SIEM and EDR alerts with context that helps analysts investigate and prioritize threats faster.
- Hunt and measure results by looking beyond individual IOCs and tracking whether intelligence improves detections, investigations, and threat hunts.
|
Threat intelligence should drive better security decisions by focusing teams on actionable information that improves detection, investigation, and response. |
|
|
|
Security Tools You Can Use |
|
|
|
Which part of a state-backed cyber pipeline concerns you most? |
|
|
|
Yesterday's Pulse Check Results |
How isolated are your print servers? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. | |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|