Attackers are finding new ways through familiar doors. |
Today’s news includes a critical GitLab vulnerability, millions of Azure records being sold, and fixes for over 400 Microsoft vulnerabilities. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
GitLab Flaw Exposes Public Repositories |
GitLab issued an out-of-band patch for a critical GraphQL flaw that could let unauthenticated attackers modify or delete public projects and user data. CVE-2026-19478 carries a CVSS score of 9.4 and affects self-managed GitLab CE and EE installations, while GitLab[.]com and GitLab Dedicated are already patched. |
watchTowr reproduced the flaw and observed exploitation attempts in their honeypots.
Patch affected GitLab instances and if that is not possible, restrict unauthenticated /api/graphql access and audit repositories for unexpected changes. |
3.6M Azure Records Allegedly Up for Sale |
A cybercriminal known as “TheHatman” is selling 3.6 million alleged Microsoft Entra ID records from McDonald’s, Vodafone, TCS, and other companies. Hudson Rock assessed samples as likely authentic, though the data’s age and origin remain unconfirmed, and TCS and Gap dispute claims of recent breaches. The records reportedly expose employee and privileged account details that could support targeted phishing, impersonation, and privilege escalation attacks.
Hunt for infostealer activity and stolen session tokens, then review Entra ID directory permissions and privileged accounts for unnecessary exposure. |
Microsoft Patch Tuesday Fixes 400+ Security Flaws |
Microsoft patched more than 400 vulnerabilities in its August security updates, including a Windows zero-day already exploited in the wild. CVE-2026-68820 can give low-privileged attackers SYSTEM access, with Check Point Research linking exploitation to a North Korean campaign deploying kernel-mode rootkits.
There are also four 9.8-rated vulnerabilities requiring no authentication or user interaction and the ShieldBreak Windows Defender exploit, making risk-based patch prioritization important.
Prioritize the latest patches, restrict local privileges, and implement compensating controls to reduce exposure. |
|
|
|
Threema Knocked Offline by DDoS Attack |
A large-scale DDoS attack knocked Threema’s hosted messaging service offline for about four hours, with disruptions returning the next morning. The attackers repeatedly changed traffic patterns, complicating mitigation, but Threema found no evidence of unauthorized access and said encryption remained intact. |
Hosted customers experienced disruptions while OnPrem deployments stayed online, prompting Threema to add upstream DDoS protections.
If secure messaging supports incident response, establish and test a secondary communication channel that does not depend on the same provider or infrastructure. |
Claude Code Used to Screen 100K Crypto Targets |
A crypto scammer used Claude Code to screen more than 100,000 phone numbers for phishing and vishing targets.
Rapid7 uncovered Operation ASTERIX infrastructure containing roughly 885,000 phone numbers and tools for identifying cryptocurrency users and enriching validated targets with personal data. The threat actors then used phishing, vishing, and fake wallet software for theft, while Claude refused requests to help them conceal the malware.
Monitor for account enumeration activity and rate-limit repeated validation requests from rotating proxies. |
|
|
|
See Your Logs When It Matters
87% of security logs end up unsearchable in cold storage. Explore how Scanner is approaching the problem, where traditional search falls short, and how teams are evaluating cost and speed at over 1 TB scale. |
|
|
|
Can Your DDoS Defenses Hold? |
DDoS attacks can exhaust network and application resources, disrupting critical services and creating operational risk. |
How to strengthen your DDoS defenses: |
- Use DDoS protection tools with upstream traffic filtering, cloud-based scrubbing, and rate limiting to block malicious traffic before it disrupts critical services.
- Monitor traffic for attack indicators by establishing normal baselines and alerting on abnormal traffic spikes, request patterns, or service degradation.
-
Build and test for resilience with redundant infrastructure and DDoS response exercises that validate escalation, traffic routing, and recovery procedures.
|
Security teams should validate whether current DDoS controls can absorb attack traffic at scale while preserving availability of the services and dependencies the business cannot afford to lose. |
|
|
|
Security Tools You Can Use |
|
|
|
How has AI changed your patch management process? |
|
|
|
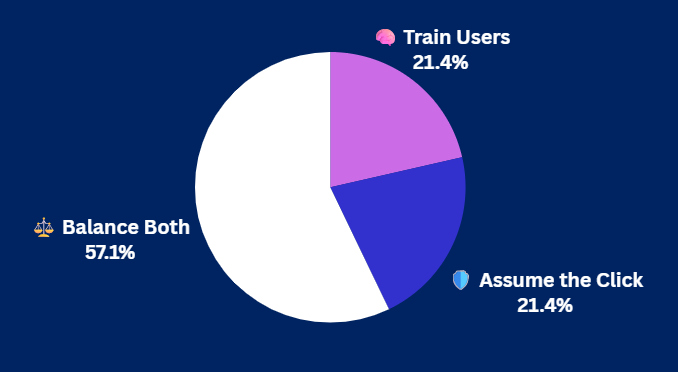
Yesterday's Pulse Check Results |
When phishing hits, where does your security strategy put its trust? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|