Defenses are being tested |
From a rogue Wi-Fi attack on a Delta flight to phishing sites hiding behind valid certificates, familiar technology is creating some unfamiliar security problems.
Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Rogue Wi-Fi Attack Hits Delta Flight |
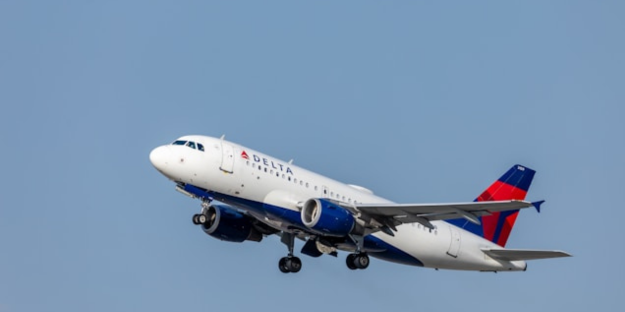
A suspected deauthentication attack disrupted Wi-Fi aboard a Delta flight carrying DEF CON attendees, prompting a 30-minute Wi-Fi shutdown. Delta confirmed an unauthorized network appeared aboard the flight, but said passenger safety and aircraft systems were not impacted. |
The company and law enforcement officials are investigating the incident.
Configure company managed devices to avoid auto-joining unknown networks and require phishing-resistant MFA for remote access. |
Shared Vendor Tied to Three Major AI Incidents |
Security tests of OpenAI, Anthropic, and Meta models reportedly reached external systems due to configuration weaknesses. All three incidents involved Irregular, an Israeli firm testing advanced AI models, highlighting how third-party infrastructure can expand the AI attack surface.
For organizations, the incidents highlight the need for strong AI containment controls and rigorous vendor security assessments. Require AI testing vendors to demonstrate deny-by-default network controls and credential isolation before granting models access to evaluation environments. |
Phishing Sites Use Valid TLS to Fool Users |
Researchers uncovered newly activated phishing infrastructure using valid TLS certificates and lookalike domains to impersonate WhatsApp and Instagram. Attackers can obtain valid certificates for fraudulent domains, making phishing sites appear legitimate while harvesting credentials and verification codes.
The risk is higher on mobile devices, where smaller screens often obscure parts of the URL, making typosquatted domains harder to spot. Direct employees to open account alerts through the official app instead of following login or verification links received through messages. |
|
|
|
OpenAI Launches GPT-5.6 Cyber for Exploit Research |
OpenAI released GPT-5.6-Cyber for advanced defensive tasks, including exploit validation and vulnerability research. Available through the restricted Daybreak Red program, GPT-5.6-Cyber completed 95% of advanced cyber requests in testing and helped uncover previously unknown vulnerabilities. |
OpenAI rates the model High under its Preparedness Framework, making strict access controls, monitoring, and human oversight critical for its dual use capabilities.
Keep AI-assisted exploit testing isolated from production networks and require human approval before models execute actions against external systems. |
CEVA Breach Hits Customers Across Europe |
A cyberattack on CEVA Logistics triggered customer data breach alerts across Europe. Exposed names, addresses, contact information, and order details could help attackers craft targeted phishing, smishing, and delivery scams.
The incident also highlights the risk of customer data held by third-parties. Audit exactly what customer data each logistics vendor retains and establish automatic deletion deadlines once fulfillment and return windows expire. |
|
|
|
42% of organizations still rely on internal teams to bridge the gap between audit readiness and audit execution.
Join eSecurity Planet and Thoropass for Breaking the Audit Fire Drill Cycle on August 20, 2026 at 1:00 PM ET and learn how leading organizations are reducing audit delays, easing evidence collection burdens, and creating more predictable audit outcomes. Save your seat and get ahead of your next audit. |
|
|
|
AI is making phishing emails more polished and personalized, eliminating many of the telltale errors that once made scams easier to spot. |
How to reduce phishing risk: |
- Confirm unexpected or urgent requests through a secondary trusted channel, and access accounts directly instead of clicking unsolicited links.
-
Use phishing-resistant MFA, such as passkeys or security keys, to reduce the impact of stolen credentials.
-
Deploy email security tools to detect suspicious links, impersonation attempts, malicious attachments, and other phishing indicators before they reach users.
|
As AI erodes traditional phishing indicators, security teams should prioritize controls that limit an attacker’s ability to turn a successful phishing attack into broader account or network compromise. |
|
|
|
Security Tools You Can Use |
|
|
|
Should the Delta Wi-Fi incident lead to jail time? |
|
|
|
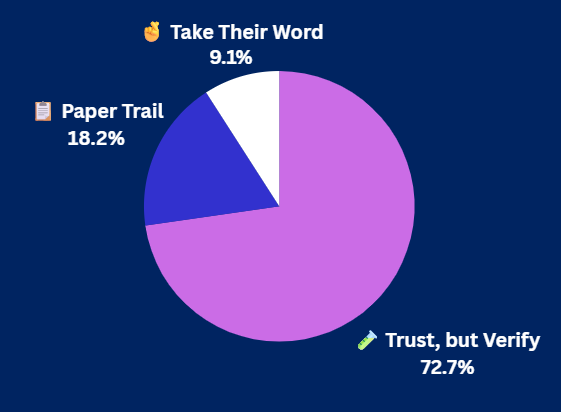
Yesterday's Pulse Check Results |
How much do you trust the security assurances you’re getting from vendors? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|