Attack surfaces are shifting |
Today’s threats stretch from AI-discovered exploits and enterprise assistants to drones, corporate leaders, and convincing phone calls.
Sometimes, the weakest link isn’t where security teams expect it… Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
AI Helps Researchers Find Zoom Zero-Click RCE Chain |
Researchers found Zoom flaws enabling zero-click remote code execution against meeting participants. Dubbed “ZOOMSDAY,” the three-vulnerability chain exploited memory-corruption flaws in Zoom’s annotation feature across Windows, macOS, iOS, and Android. |
The researchers developed a working exploit in under 24 hours using publicly available AI models, and Zoom has since released fixes.
Prioritize Zoom client updates across managed endpoints and restrict annotation privileges to trusted participants. |
RovoBlast Exposes Data Risks in Atlassian AI |
Varonis researchers uncovered an Atlassian Rovo flaw that could inject malicious prompts into authenticated AI sessions through a crafted link. The attack used existing user permissions to potentially expose sensitive data across connected enterprise services.
This research shows how AI integrations and autonomous agents can amplify prompt injection risks. Audit Rovo and other enterprise AI connectors, remove unnecessary data sources, and restrict autonomous agents from accessing sensitive systems or external destinations. |
Royal Navy Drone Cameras Contact Chinese IP |
A UK defense assessment found Royal Navy drone cameras communicating with a Chinese IP address, prompting officials to cut internet access. The third-party cameras were used on Kraken Technology Group’s K3 Scout vessels despite unexpected traffic passing supplier security checks. No compromise was found at this time, but the incident highlights the need to independently validate connected devices rather than rely solely on vendor assurances. Baseline approved outbound destinations for connected hardware during acceptance testing, then automatically flag or block new connections after firmware and configuration changes. |
|
|
|
Ransomware Attackers Zero in on Business Leaders |
Zscaler found that ransomware operators are increasingly targeting managers and other business leaders for their privileged organizational access. Researchers discovered that 62% of victims were managers or higher, while 75% worked in business-critical functions such as finance, sales, and operations. |
These findings show that business privilege can pose risk even without technical administrator access.
Map employees who can approve payments, modify vendor information, or access sensitive business data, then require phishing-resistant MFA and secondary verification. |
Wall Street Firms Hit by Phone-Based Extortion Campaign |
Threat actors are targeting major U.S. financial firms with fake help-desk calls designed to steal credentials and extort victims. Attackers impersonate IT staff and direct employees to phishing sites that capture passwords and authentication codes in real time.
Google linked the campaign to infrastructure targeting more than 200 organizations, highlighting how social engineering can bypass strong authentication controls. Require employees to verify unexpected passkey, MFA, password, or account change requests directly with IT through an approved internal channel. |
|
|
|
Modern employees expect seamless access from anywhere, while IT teams are expected to deliver more with fewer resources. Cloud-first workspace strategies are becoming essential, not optional.
TechRepublic partners with Nerdio on August 19 at 1:00 PM ET to share practical guidance for simplifying cloud migrations, improving security, and reducing operational overhead. |
|
|
|
Could Your Data Be Overexposed? |
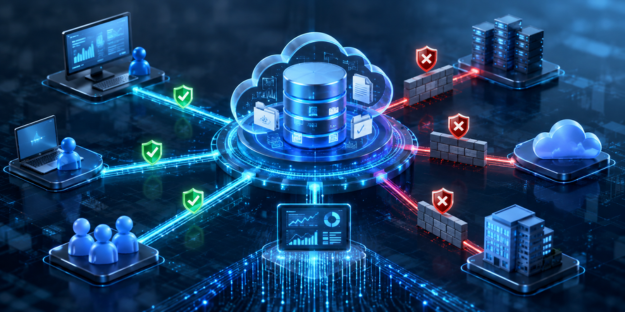
Data exposure often stems from misconfigurations, excessive access, and third-party connections that leave sensitive information unnecessarily accessible. |
How to reduce data exposure risk: |
- Apply least-privilege controls and regularly review third-party permissions to limit unnecessary access to sensitive data.
-
Use DLP tools to detect and block unauthorized sharing, transfers, and exposure of sensitive information.
- Audit cloud configurations and monitor for unusual data access, downloads, and permission changes.
|
Reducing data exposure requires continuous visibility into where sensitive data lives, who can access it, and how it moves across the organization. |
|
|
|
Security Tools You Can Use |
|
|
|
How much do you trust the security assurances you’re getting from vendors? |
|
|
|
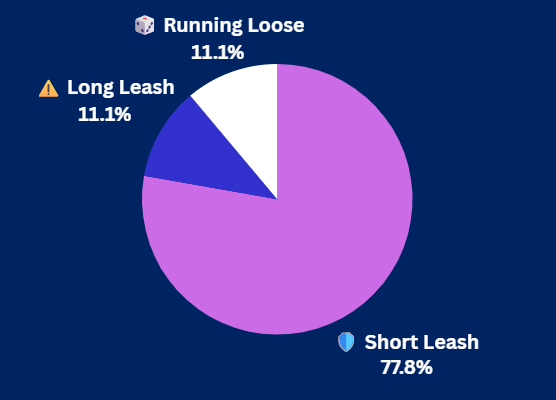
Yesterday's Pulse Check Results |
How much control have you really handed over? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|