AI is moving fast. Security gaps may be moving faster. |
Today’s news brings risky AI agents, unreliable AI fixes, smarter BEC attacks, evasive Mac malware, and dozens of mobile flaws. Innovation keeps accelerating, but so does the attack surface. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Critical Flaws Put AI Coding Agents at Risk |
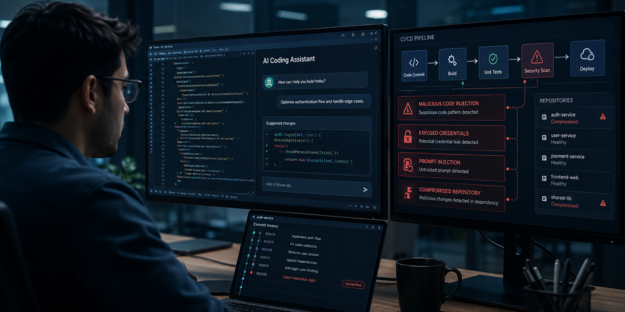
Researchers uncovered critical vulnerabilities in AI coding agents from Anthropic, Google, and OpenAI that could let attackers compromise development workflows.
The flaws exposed risks including RCE, credential theft, persistent prompt injection, and software supply chain compromise, revealing weaknesses in the infrastructure surrounding AI agents. |
While all three vendors introduced mitigations, organizations using similar default configurations and automated workflows could remain at risk.
Audit agent permissions and trust boundaries, isolate workflow stages, treat agent-generated files as untrusted, and monitor AI-powered CI/CD pipelines for unexpected execution or credential access. |
AI-Generated Patches Fail More Than Half the Time |
A 1Password study found that just 26% of more than 6,000 AI-generated security patches fully fixed vulnerabilities without unintended side effects and that the patches failed to fully block the exploit pathway more than half the time.
Researchers found that AI-generated patches often treated symptoms instead of root causes, missed alternate exploit paths, or introduced new vulnerabilities. Better prompts improved results but failed to eliminate insecure fixes, raising concerns about autonomous remediation in production environments.
Organizations should require experienced engineers to review AI-generated patches and test them against alternate exploit paths before approving deployment. |
AI Email Assistants Fuel BEC Attacks |
Barracuda researchers showed how attackers could use AI email assistants to turn compromised accounts into sophisticated BEC attacks. In the proof-of-concept, Microsoft Copilot helped attackers conduct reconnaissance, evade detection, craft convincing phishing emails, and redirect a $247,500 wire transfer.
The research shows how AI can make attacks from legitimate accounts faster and harder for traditional email security controls to detect.
Organizations should alert on newly created or modified inbox rules in AI-enabled accounts and require out-of-band verification before approving changes to payment instructions. |
|
|
|
ClickFix Campaign Evades Scanners to Target Macs |
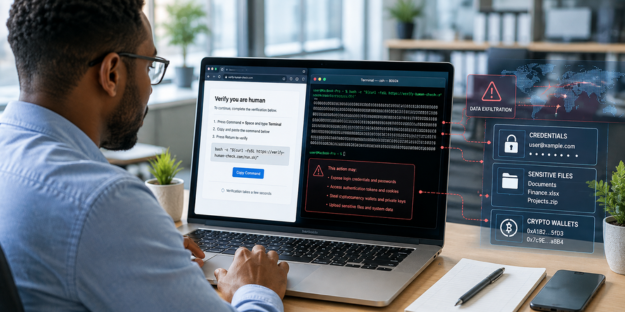
More than 250 malicious domains use browser fingerprinting to identify Mac users and deliver Atomic Stealer or MacSync malware. Mac users who pass fingerprinting checks are prompted to run obfuscated Terminal commands that can expose credentials, crypto wallets, and sensitive files. |
Microsoft found the campaign serves benign content to security tools and researchers, helping its malicious infrastructure evade detection.
Monitor for browser activity immediately followed by suspicious Terminal commands, like curl piped into zsh, Base64 decoding, or osascript execution, rather than relying solely on domain reputation or page scans. |
Samsung Fixes 56 Security Flaws |
Samsung’s August 2026 update fixes 56 vulnerabilities across Galaxy devices, including eight critical Android flaws. The update includes 38 Google fixes and 18 Samsung-specific patches affecting components such as Contacts, Messages, AppLock, and system libraries. Enterprises that delay updates could leave Galaxy devices exposed to privilege escalation, unauthorized data access, and other attacks.
Use mobile device management tools to verify patch levels across managed Galaxy devices and prioritize remediation for users handling sensitive or privileged accounts. |
|
|
|
Every Unprotected Identity Is an Open Door for Attackers
BeyondTrust's PAM Buyer's Guide details eight must-have capabilities to secure human, machine, and AI identities—covering Agentic AI, DevOps, OT security, and Zero Trust. Download to strengthen your PAM strategy, plus get a customizable Excel checklist to compare BeyondTrust head-to-head against other vendors. |
|
|
|
Mobile devices can give threat actors a path to sensitive data through OS vulnerabilities, malicious apps, and phishing/smishing attacks. |
Source: Rahul Chakraborty/Unsplash |
How to reduce mobile device risk: |
- Enable automatic updates, use a screen lock with biometrics when available, and turn on remote device tracking and wiping.
- Download apps only from trusted sources and regularly review permissions to limit unnecessary access to sensitive data and device features.
- Use a VPN on public Wi-Fi and remain cautious of suspicious links, QR codes, attachments, and messages that could be phishing attempts.
|
As threat actors use AI to make phishing, social engineering, and other mobile attacks more scalable and convincing, organizations should reassess whether existing controls adequately address risk. |
|
|
|
Security Tools You Can Use |
|
|
|
Where does AI fit into your patching process? |
|
|
|
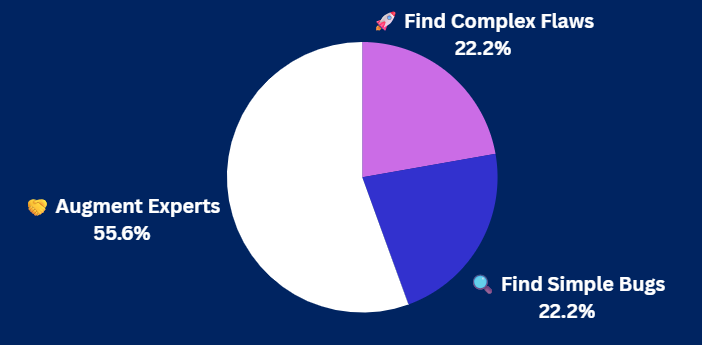
Yesterday's Pulse Check Results |
Five years from now, AI will mostly... |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|