The rules of cyber defense are changing. |
This edition explores faster-moving AI threats, trusted networks turned against travelers, a large breach, and why one overlooked AI component could reshape security testing.
Read past newsletters here. | |
|
|
Here’s what you need to know: |
|
|
|
CrowdStrike Threat Hunting Report Flags Surge in AI-Powered Attacks |
CrowdStrike's latest threat hunting report shows attackers increasingly abusing AI, trusted identities, cloud services, and software supply chains to accelerate attacks. The report found AI-enabled threat activity surged 89%, while 88% of vulnerability attacks began within 48 hours of PoC code becoming available. |
It also highlights rising vishing, OAuth abuse, supply chain attacks, and cloud-focused eCrime as adversaries blend automation with hands-on tactics to accelerate compromises.
Prioritize patching internet-facing assets within 48 hours of public exploit releases and strengthen identity monitoring with phishing-resistant authentication and continuous behavioral threat hunting. |
Microsoft Flags Russian Hotel Wi-Fi Attacks |
A Russian state-backed campaign is using compromised hotel Wi-Fi networks to trick business travelers into stealing credentials or installing malware.
Microsoft attributes the campaign, tracked as CaptiveCrunch, to Storm-2945, a subgroup of Midnight Blizzard, which uses fake updates, ClickFix lures, and device-code phishing to compromise endpoints and cloud identities. Because stolen Microsoft 365 session tokens can remain valid even after a device is cleaned, a single hotel Wi-Fi connection could provide attackers with prolonged access to corporate email, files, and internal systems. Require employees to use an always-on, full-tunnel VPN or a trusted cellular hotspot while traveling, and disable Microsoft device-code authentication wherever it is not operationally required to reduce identity-based attacks. |
UK Police Breach Exposes 135,000 Contacts |
A cyberattack on the U.K.'s Police National Legal Database (PNLD) exposed the contact details of approximately 135,000 police personnel, government partners, and members of the public.
While no operational case files appear to have been exposed, the stolen contact data could fuel targeted phishing and impersonation attacks. The incident also underscores the growing threat of data extortion, where attackers gain leverage by exposing sensitive information instead of encrypting systems.
Secure employee directories with phishing-resistant MFA, restricted access, and suspicious login monitoring. |
|
|
|
Flare Launches Free Dark Web Training |
Flare has launched Darkroom, a free interactive platform for hands-on threat intelligence training. Participants investigate simulated dark web activity through adaptive, AI-powered scenarios covering ransomware, stolen credentials, and cryptocurrency tracing. |
The interactive training helps analysts improve threat hunting, attribution, and pre-breach intelligence capabilities.
Add interactive threat intelligence exercises to your team’s training program so analysts can practice investigating attacker infrastructure and credential exposure before facing a live incident. |
AI Harnesses Change Red Team Outcomes |
New research from Lasso suggests AI agent harnesses can influence offensive security results as much as the underlying LLM. Swapping only the runtime framework dramatically changed attack success rates, with one model improving from 1% to 24%.
Researchers also found AI agents often misclassified failed attacks as successful, raising concerns about AI benchmarking. When assessing AI agents, benchmark the complete model-and-harness stack and validate results with independent testing rather than relying on the agent’s self-reported success metrics. |
|
|
|
Customer expectations are changing as quickly as the threat landscape. Discover how MSPs and MSSPs can evaluate AI-driven security capabilities to strengthen customer protection and prepare their managed security services for what's next during Channel Insider's webinar with ESET on August 18 at 1:00 PM ET. |
|
|
|
Threat Intelligence Starts Before the Attack |
Threat intelligence is essential for organizations of all sizes, helping security teams identify emerging threats early as attackers increasingly target identities, cloud environments, and software supply chains. |
How to strengthen your threat intelligence: |
-
Use trusted threat intelligence feeds and tools to track active threat actors, emerging campaigns, and validated IOCs.
-
Monitor your external exposure for leaked credentials, exposed assets, and dark web activity, while mapping threats to the MITRE ATT&CK framework.
- Share actionable threat intelligence to prioritize patching, improve defenses, and respond faster to emerging threats.
|
Organizations that operationalize context-rich threat intelligence are better positioned to reduce risk, prioritize resources, and respond before attackers achieve their objectives. |
|
|
|
Security Tools You Can Use |
-
Cyber threats move fast—your endpoint management should too. Discover how autonomous endpoint management helps close security gaps and keep endpoints protected with less manual effort.
-
Automate like an admin — master Active Directory with PowerShell and save 74% today.
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
|
|
|
|
What's your go-to internet connection on the road? |
|
|
|
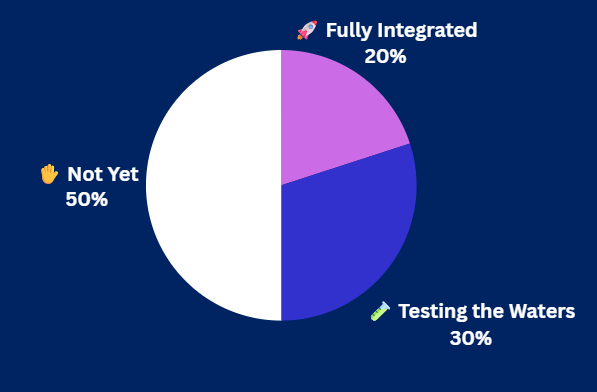
Yesterday's Pulse Check Results |
AI Pen Testing Check: Where's your team today? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|