The attack surface keeps expanding. |
Today's roundup covers active N-able RMM exploitation, AI pushing new boundaries, hundreds of browser fixes, and why ERP security is struggling to keep pace with AI adoption.
It's Hacker Summer Camp week in Vegas — have a great time if you're attending! Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
N-able RMM Vulnerability Under Active Attack |
A vulnerability in N-able's N-central RMM platform is under active exploitation, potentially giving attackers administrative control of every managed endpoint. Huntress researchers warn attackers can abuse legitimate management features to deploy scripts, establish persistence, and move laterally. |
The vendor has already released a hotfix for the issue.
Apply N-able's hotfix immediately, review administrative activity for signs of compromise, and validate that RMM infrastructure is protected with MFA, least privilege, and continuous monitoring. |
ShinyHunters Alleges Brinks Home Breach |
Brinks Home is investigating a cybersecurity incident after attackers claimed to breach the company through a Microsoft Entra vishing campaign. The incident highlights how identity-focused social engineering can bypass traditional security controls.
Although Brinks Home has not confirmed the full scope, ShinyHunters claims it stole customer records, employee PII, and millions of customer support chat logs
Review Microsoft Entra logs for suspicious MFA approvals and device registrations, then verify phishing-resistant MFA and Conditional Access are enforced across SaaS platforms. |
Claude Advances AI-Driven Cryptographic Research |
Anthropic says its Claude Mythos Preview model developed new cryptanalytic techniques targeting the HAWK post-quantum candidate and reduced-round AES-128. Neither discovery threatens production encryption today, but it highlights how frontier AI is beginning to accelerate cryptographic research. Anthropic coordinated responsible disclosure with researchers and introduced CryptanalysisBench to help evaluate how AI may identify weaknesses in future encryption standards. Maintain a current inventory of cryptographic assets, so your organization can prioritize future algorithm migrations as standards evolve. |
|
|
|
Chrome Fixes 370 Security Vulnerabilities |
Google has patched 370 vulnerabilities in its latest Chrome release, including seven Critical flaws. Many of the patched flaws involve memory-safety issues, including use-after-free vulnerabilities that could enable browser crashes or arbitrary code execution. |
Google said there are no reports of active exploitation in the wild.
Verify that managed endpoints are updated to the latest version of Chrome. |
ERP AI Growth Exposes Security Gaps |
Enterprise organizations are rapidly integrating AI into ERP platforms, but confidence of security leaders is struggling to keep pace. Onapsis researchers found that while AI adoption is accelerating across ERP platforms, nearly 69% of security leaders lack confidence in detecting AI-driven attacks. More than one in five organizations also reported confirmed AI-assisted attacks against business-critical systems. Inventory every AI application and agent interacting with ERP systems, verify least-privilege access, and continuously monitor AI activity. | |
|
|
Modern employees expect seamless access from anywhere, while IT teams are expected to deliver more with fewer resources. Cloud-first workspace strategies are becoming essential, not optional.
TechRepublic partners with Nerdio on August 19 at 1:00 PM ET to share practical guidance for simplifying cloud migrations, improving security, and reducing operational overhead. |
|
|
|
As threat actors prioritize large-scale data theft across environments, organizations need stronger visibility and control over their data. |
- Classify and protect sensitive data by encrypting critical information at rest, in transit, and in backups while enforcing least-privilege access to reduce exposure.
-
Deploy data loss prevention (DLP) tools to detect and prevent unauthorized movement of sensitive data across endpoints, email, cloud services, and SaaS applications.
-
Continuously monitor data access and test recovery to identify suspicious activity early and ensure critical data can be restored quickly following a security incident.
|
Effective data protection depends on knowing where sensitive data resides, controlling who can access it, and detecting unauthorized activity before data leaves the environment.
|
|
|
|
Security Tools You Can Use |
|
|
|
How concerned are you about AI accelerating cryptographic attacks? |
|
|
|
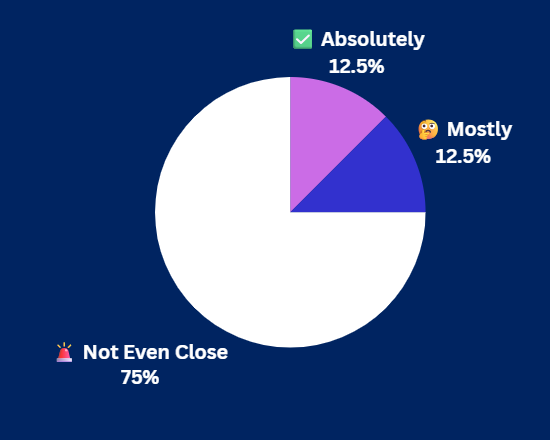
Yesterday's Pulse Check Results |
Could you explain every AI model in production today? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|