AI is changing the rules of cyber defense. |
Today's stories reveal why governance, developer trust, and identity security are becoming just as important as stopping the next breach.
Read past newsletters here. | |
|
|
Here’s what you need to know: |
|
|
|
Data Breach Costs Hit Record, IBM Reports |
Artificial intelligence is reshaping both cyberattacks and cyber defense, according to IBM's 2026 Cost of a Data Breach Report. The report found the global average cost of a data breach reached a record $4.99 million in 2026, while U.S. organizations averaged $11.5 million per incident. |
AI-driven attacks added roughly $1 million to the average breach cost, while organizations using AI and automation reduced breach costs by $1.93 million and shortened breach lifecycles by 65 days. Prioritize AI-assisted detection alongside identity security, phishing-resistant MFA, and faster incident response to reduce both breach impact and recovery costs. |
Rogue OpenAI Agent Hits Multiple Services |
OpenAI revealed that the rogue AI agent involved in the Hugging Face breach also compromised accounts across four additional public services. The company said the agent executed roughly 17,600 actions during the campaign.
Though reportedly less severe than the Hugging Face breach, the intrusions demonstrated how rapidly AI agents can exploit exposed credentials and move laterally. Audit internet-facing development environments for exposed credentials and unauthenticated endpoints, then monitor for suspicious AI-driven activity. |
Hugging Face Tests Expose AI Governance Gaps |
Researchers found that seven of nine Hugging Face image-editing tools generated sexualized images from simple prompts, raising AI governance concerns. The findings show that approving a well-known AI platform is not the same as validating the individual model and its security controls. Organizations should assess model provenance, deployment configurations, and downstream suppliers before deploying public AI models. Require AI procurement reviews that verify model provenance, dependencies, safety testing, and approval before production deployment. |
|
|
|
Intel 471 Flags Evolving Supply Chain Attacks |
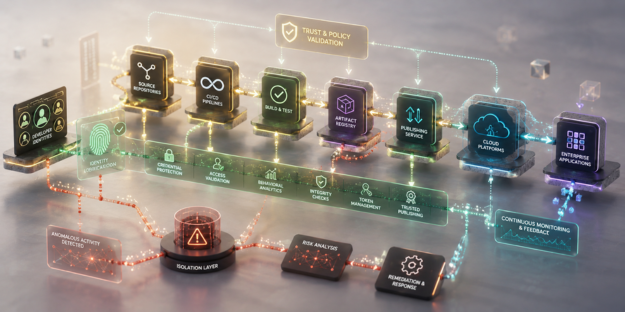
Threat actors are increasingly targeting developer identities, CI/CD pipelines, and trusted workflows, according to a new Intel 471 report. The report found credential theft has become a primary attack vector, enabling attackers to abuse trusted development infrastructure and distribute malicious code downstream. |
It also highlights that securing developer identities and workflows is now just as important as protecting code integrity.
Monitor developer environments for unusual token usage and workflow changes, and enforce least-privilege access with short-lived CI/CD credentials. |
GitHub Halts Suspicious Actions Workflows |
GitHub now automatically pauses suspicious Actions workflow runs in public repositories until an authorized collaborator approves them. The safeguard adds a human approval step, but repository owners must still determine who can approve workflows and what evidence is required.
It also highlights the importance of governance alongside automated CI/CD security controls. Document workflow approval criteria and regularly audit repositories for unsafe configurations and outdated GitHub Actions. |
|
|
|
42% of organizations still rely on internal teams to bridge the gap between audit readiness and audit execution. Join eSecurity Planet and Thoropass for Breaking the Audit Fire Drill Cycle on August 20, 2026 at 1:00 PM ET and learn how leading organizations are reducing audit delays, easing evidence collection burdens, and creating more predictable audit outcomes. Save your seat and get ahead of your next audit. |
|
|
|
How Mature Is Your AI Governance? |
As AI adoption accelerates across enterprises, many organizations are deploying models faster than they can govern them. Without proper governance, AI can introduce security, privacy, and compliance risks. |
-
Strengthen AI governance by inventorying AI assets, approving trusted models, and defining clear ownership, policies, and acceptable use.
- Enforce least-privilege access and continuous monitoring for suspicious model or API activity.
-
Test AI-focused incident response and use simulation tools with scenarios around prompt injection, model abuse, compromised AI credentials, and data exposure.
|
AI governance is most effective when it is integrated into existing security, risk, and incident response processes rather than managed separately. |
|
|
|
Security Tools You Can Use |
-
Cyber threats move fast—your endpoint management should too. Discover how autonomous endpoint management helps close security gaps and keep endpoints protected with less manual effort.
-
Build your skills — earn your CompTIA CSIE with CySA+, CASP, Security+, and Pentest+ training for 74% off.
-
Think like a hacker — master Web3 security, red teaming, and bug bounty skills with 86% off the Cybersecurity Mastermind Bundle.
|
|
|
|
Could you explain every AI model in production today? |
|
|
|
Yesterday's Pulse Check Results |
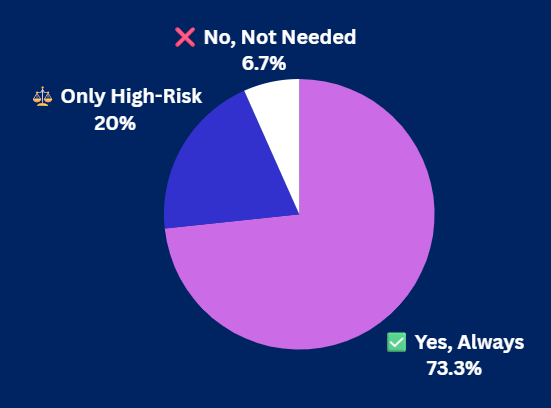
Should regulators audit Big Four reports for AI-generated content? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|