The attack surface keeps expanding. |
Today's news spans an actively exploited RCE, exposed CI/CD infrastructure, massive Apple security updates, and AI accelerating vulnerability discovery.
Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
FastJson RCE Flaw Actively Exploited |
Threat actors are actively exploiting a FastJson remote code execution vulnerability that requires no user interaction or elevated privileges. The flaw affects FastJson versions 1.2.68 through 1.2.83 deployed as Spring Boot executable fat-JARs. |
There is no patch available for this vulnerability, so organizations should migrate to a supported version.
Inventory applications and third-party software using vulnerable FastJson versions, enable SafeMode immediately, and prioritize migrating to fastjson2 or another supported JSON library. |
Apple Ships 194 Vulnerability Fixes |
Apple has released a major security update addressing 194 unique vulnerabilities across iPhone, iPad, Mac, Apple Watch, Apple TV, and Vision Pro devices.
Several of the vulnerabilities could allow attackers to gain root or kernel-level privileges, execute malicious code, expose sensitive data, or bypass security protections. Apple did not report any exploitation of the vulnerabilities at the time of publication.
Audit for vulnerable devices on your network and apply patches or compensating controls. |
TeamCity Flaw Opens Door to Server Attacks |
JetBrains has patched a TeamCity vulnerability that could let unauthenticated attackers execute commands on exposed CI/CD servers. The flaw affects unpatched TeamCity On-Premises deployments and could allow attackers to steal credentials, alter server configurations, or compromise software build pipelines.
JetBrains did not report any exploitation in the wild. Upgrade to the latest version and if an upgrade must be delayed, then review build artifacts, access tokens, and server activity for signs of unauthorized changes. |
|
|
|
AI Exposes More Software Weaknesses |
More than 45,000 software vulnerabilities have been reported in 2026 as AI accelerates discovery. Major technology vendors, including Oracle, Microsoft, and Google, are releasing significantly larger security updates as AI accelerates vulnerability discovery. |
At the same time, broader access to advanced AI cyber models is raising concerns that defensive innovations could also strengthen offensive capabilities.
Reevaluate vulnerability management priorities by focusing on internet-facing assets, known exploited vulnerabilities, and automated risk-based patching to keep pace with the growing volume. |
Cursor Fixes Git Execution Flaw |
A high-severity Cursor flaw from months ago could let attackers execute code by tricking developers into opening a malicious Git repository. The vulnerability causes Cursor to execute a rogue git[.]exe file, potentially exposing developer workstations, credentials, and software supply chains. Although Cursor has patched the vulnerability, it highlights how AI-powered development tools can amplify longstanding security risks.
Patch to the latest version and restrict developers from opening untrusted repositories until they have been scanned for unexpected executables and other potentially malicious files. |
|
|
|
Modern employees expect seamless access from anywhere, while IT teams are expected to deliver more with fewer resources. Cloud-first workspace strategies are becoming essential, not optional. TechRepublic partners with Nerdio on August 19 at 1:00 PM ET to share practical guidance for simplifying cloud migrations, improving security, and reducing operational overhead. |
|
|
|
Strengthen Supply Chain Security |
Applications rely on third-party components, so a single compromised dependency or CI/CD pipeline can impact downstream systems. |
How to reduce supply chain risk: |
-
Use DevSecOps tools to improve visibility, while combining SBOMs, software composition analysis (SCA), and dependency monitoring to identify vulnerable or malicious components.
-
Secure your software delivery pipeline by enforcing least-privilege access, MFA, and package integrity verification across CI/CD systems.
- Prepare for supply chain incidents by testing response plans, rotating credentials, rebuilding trusted artifacts, and validating software integrity after a compromise.
|
Reducing software supply chain risk requires embedding security throughout the development lifecycle, not just responding after vulnerabilities are discovered. |
|
|
|
Security Tools You Can Use |
|
|
|
CI/CD Pipeline Security Check: What's your biggest concern? |
|
|
|
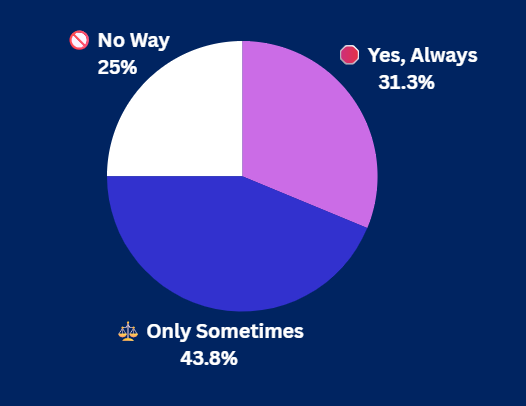
Yesterday's Pulse Check Results |
Should governments have an AI kill switch? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|