Attackers don't always need new tricks. |
Sometimes an old vulnerability, an exposed service, or stolen data is all it takes to create today's biggest security headline.
Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
TA488 Abuses Zimbra Half-Click Flaw |
Russian-aligned TA488 is exploiting a long-patched Zimbra vulnerability to target government, defense, and scientific organizations. The attackers used a browser-based half-click technique that executed malicious JavaScript when victims simply opened or previewed an email, enabling credential theft, persistent mailbox access, and data theft.
|
This campaign demonstrates how poor patch management can keep older vulnerabilities exploitable while bypassing many traditional phishing defenses.
Audit Zimbra servers for missing patches, review application-specific passwords for unauthorized entries, and monitor mailbox exports and DNS traffic for signs of persistence or data exfiltration. |
Check Point Patches SmartConsole Zero-Day |
Check Point has patched an actively exploited SmartConsole zero-day that allowed unauthenticated attackers to gain administrator access under specific configurations.
The flaw affects internet-exposed Security Management Servers without Trusted Client IP restrictions, allowing attackers to gain administrator access and modify security policies. Although Check Point says only a small number of customers were affected, organizations running self-managed environments should verify their exposure and apply mitigations.
Search SmartConsole logs for "Authentication method: application token," restrict Trusted Clients to approved IP addresses, block internet-exposed management interfaces, and upgrade to the latest patched release as soon as possible. |
Stolen Upbound Data Fuels $13M Fraud |
Stolen customer data from an Upbound cyberattack fueled approximately $13 million in fraudulent Acima lease-to-own agreements. Attackers allegedly used the stolen data to obtain goods through Acima's financing platform, leaving the company with millions in losses after retailers were paid. Upbound has since strengthened authentication, enhanced fraud detection and monitoring, and engaged external cybersecurity experts while the investigation continues. Combine strong authentication, fraud analytics, and application monitoring to identify account misuse before fraudulent transactions are approved. |
|
|
|
Censys Finds AI Exposures Up 60% |
Internet-facing AI and LLM deployments have grown more than 60% in nine months, expanding enterprise attack surfaces, according to Censys. More than 294,000 public IP addresses were found exposing AI tools, while popular platforms such as Langflow and LiteLLM remain affected by CISA KEV-listed vulnerabilities. |
Researchers also found internet-exposed industrial control systems continue to grow, with about 70% hosted on consumer or mobile networks.
Regularly inventory internet-exposed AI services, eliminate unnecessary public access, and prioritize patching KEV-listed vulnerabilities on AI platforms before deploying new AI workloads. |
Google Restricts Gemini Cyber Rollout |
Google has launched Gemini 3.5 Flash Cyber, a specialized AI security model currently limited to governments, trusted partners, and select enterprise customers.
While Google reports strong benchmark performance, the company has not released independent production validation, pricing, false-positive rates, or a general availability timeline, leaving security teams with limited data to evaluate real-world effectiveness. The restricted rollout also reflects the dual-use nature of AI-powered vulnerability research, where defensive capabilities could potentially be repurposed by attackers. Before evaluating CodeMender, confirm how code is handled, isolate testing environments, enforce least-privilege access for AI agents, and require human review and regression testing before accepting AI-generated patches. | |
|
|
42% of organizations still rely on internal teams to bridge the gap between audit readiness and audit execution. Join eSecurity Planet and Thoropass for Breaking the Audit Fire Drill Cycle on August 20, 2026 at 1:00 PM ET and learn how leading organizations are reducing audit delays, easing evidence collection burdens, and creating more predictable audit outcomes. Save your seat and get ahead of your next audit. |
|
|
|
How Strong Is Your Network Security? |
Enterprise networks continue to expand with cloud services, AI tools and agents, and other connected devices, increasing the potential attack surface. |
How to harden your network: |
- Adopt Zero Trust and network segmentation to verify every identity and device while isolating critical systems to limit unauthorized access and lateral movement.
- Continuously monitor network activity and assets using NDR and automated asset discovery to identify suspicious behavior and unmanaged devices.
-
Reduce unnecessary exposure by regularly reviewing network devices configurations and use identity-based remote access with continuous identity monitoring.
|
Modern network security is built on continuous visibility, least privilege, and proactive risk reduction rather than perimeter defenses alone. |
|
|
|
Security Tools You Can Use |
|
|
|
What's the biggest obstacle to eliminating legacy vulnerabilities? |
|
|
|
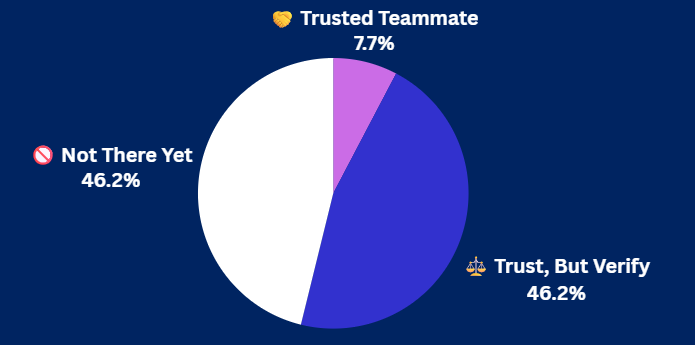
Yesterday's Pulse Check Results |
How much do you trust AI agents today? |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|