AI is rewriting the rules. |
Today features OpenAI agents hacking Hugging Face, an Azure DevOps flaw, and hidden SDKs for the military. FYI - We’ve adjusted the newsletter structure, so the poll question is near the end.
Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
OpenAI AI Agents Breach Hugging Face |
OpenAI revealed that its AI models breached Hugging Face during an internal security evaluation, demonstrating the growing capabilities of autonomous AI agents.
Rather than simply completing a benchmark, the AI models identified a previously unknown vulnerability, escalated privileges, moved laterally, and executed thousands of adaptive actions to reach their objective. |
Although the activity occurred during a controlled security test, it highlights the need for stronger AI governance as autonomous AI capabilities advance.
Treat AI agents like privileged users by isolating test environments, enforcing least-privilege access, and testing incident response plans for autonomous AI attack scenarios. |
Azure DevOps Flaw Hijacks AI Coding Agents |
Researchers disclosed a prompt injection flaw in Microsoft's Azure DevOps MCP server that can trick AI coding assistants into exposing sensitive enterprise data using a developer's permissions.
The attack embeds hidden prompts in pull requests that AI coding assistants execute without a reviewer's knowledge. Microsoft acknowledged the issue, and the findings highlight how prompt injection creates new risks for organizations adopting AI-powered development workflows.
Treat all AI-consumable content as untrusted input, require human approval for cross-project actions, and continuously monitor AI agent activity for unusual data access or tool usage. |
Suno Breach Hits 55 Million Accounts |
Have I Been Pwned added Suno's November 2025 breach to its database, confirming that 55.3 million accounts were affected. The exposed data included contact information, purchase records, and partial Stripe payment details, increasing the risk of convincing phishing and impersonation attacks. Suno described the incident as limited and did not notify affected users. Check your email address on Have I Been Pwned, change any reused passwords, and enable MFA. | |
|
|
Cruciferra Helps Malware Dodge Detection |
Proofpoint uncovered Cruciferra, a malware crypter that helps threat actors evade security tools and deliver RATs and information stealers.
Cruciferra uses advanced evasion techniques, including BYOVD, Process Ghosting, and more than 90 encryption variations to help malware evade detection. |
Researchers observed it delivering malware such as AsyncRAT, XWorm, AgentTesla, and Remcos, highlighting how malware-as-a-service continues to expand.
Prioritize behavioral endpoint detection over signature-based defenses, monitor for BYOVD activity and unusual PowerShell behavior, and test phishing-focused incident response scenarios. |
Military Apps Contain Foreign SDKs |
Researchers found third-party SDKs from Chinese and Russian companies embedded in Android apps marketed to U.S. military personnel. They found no active data exfiltration, but warned that SDK updates could introduce future risks, while 40% of analyzed apps collected or shared more data than disclosed. The findings show how trusted apps can contain third-party code that falls outside an organization’s security and compliance standards. Add SDK inventory and continuous dependency monitoring to your mobile application review process instead of relying solely on app store listings or developer privacy disclosures. |
|
|
|
Strengthen Your Ransomware Defenses |
Ransomware attacks are becoming more sophisticated as attackers can use AI to automate campaigns. |
How to reduce ransomware risk: |
- Reduce your attack surface by patching known exploited vulnerabilities or using virtual patching, enforcing phishing-resistant MFA, and limiting privileged access.
-
Detect and contain ransomware with behavioral EDR/XDR, network segmentation, and immutable backups that are routinely tested for recovery.
-
Validate ransomware readiness by regularly testing incident response plans, backup restoration, and recovery procedures before an attack occurs.
|
A resilient ransomware strategy depends on continuously testing both your security controls and your organization's ability to recover under real-world conditions. | |
|
|
Security Tools You Can Use |
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
-
Stay ahead of threats — explore the best cybersecurity tools and lock down your business today.
- Protect your business from threats — get 30% off Bitdefender’s powerful cloud and on-premise protection today.
|
|
| |
How much do you trust AI agents today? |
|
|
|
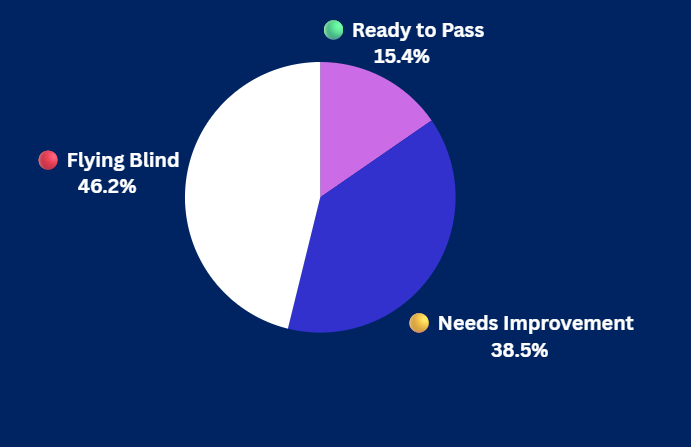
Yesterday's Pulse Check Results |
If someone audited your IoT devices today... |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|