Old vulnerabilities can still create problems. |
Today’s stories span legacy IoT flaws, a Chick-fil-A attack, healthcare vendor risk, AI powering cybercrime, and a global phishing takedown. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Decades-Old Flaw Hits Modern IoT Devices |
Finite State found legacy third-party software in a popular IoT camera that exposed sensitive data and increased denial-of-service risk. Because the camera uses a shared white-label platform, the same vulnerabilities may affect other devices built on the same firmware. |
The findings reinforce the value of SBOMs and continuous software inventory for identifying vulnerable components early.
Segment IoT devices, request SBOMs during procurement, and prioritize remediation based on exploitability rather than vulnerability counts alone. |
Credential Stuffing Hits Chick-fil-A Customers |
Threat actors used stolen usernames and passwords to compromise Chick-fil-A customer loyalty accounts. The incident may have exposed customer contact information, loyalty account details, payment information, and other personal data.
Chick-fil-A has not confirmed the total number of customers impacted at the time of publication. Continuously monitor authentication activity for unusual login patterns and deploy bot detection, passkeys or phishing-resistant MFA, and compromised credential screening to reduce account takeover risk. |
Healthcare Supply Chain Hit by Craneware Breach |
A cyberattack on a healthcare software provider has potentially exposed sensitive data.
The breach highlights the growing risk posed by third-party healthcare vendors, whose compromise can have cascading effects across the healthcare ecosystem. Although Craneware said it contained the incident and services remained operational, investigators are still determining what data was accessed and whether patient information was affected.
Review critical vendors' security practices, breach notification processes, and data retention policies to ensure they align with your organization's third-party risk management program. |
|
|
|
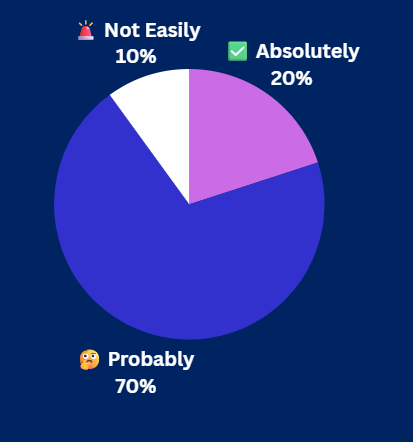
If someone audited your IoT devices today... |
|
|
|
Yesterday's Pulse Check Results |
Could you tell a billing bug from a cloud breach? |
|
|
|
Security Tools You Can Use |
-
Start your cybersecurity career for free — enroll in Microsoft’s 9-course Analyst Certificate series on Coursera today.
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
-
Build your skills — earn your CompTIA CSIE with CySA+, CASP, Security+, and Pentest+ training for 74% off.
|
|
|
|
AI Fuels Next Wave of Cybercrime |
A ThreatDown report warns that guardrail-free AI models, malicious AI agent skills, shadow AI, and AI-powered malware are transforming cybercrime. Researchers suggested AI could shorten the time required to discover and weaponize zero-day vulnerabilities, giving defenders less time to patch critical systems. |
As organizations increasingly adopt AI tools, the findings emphasize that governance and visibility are becoming just as important as traditional security controls.
Inventory and govern all AI applications and agent integrations, then prioritize rapid patching and continuous monitoring to reduce exposure to AI-assisted attacks. |
Authorities Shut Down Kratos Phishing Service |
An international law enforcement operation dismantled the Kratos phishing platform, seizing more than 200 servers and arresting its alleged developer in Indonesia.
Investigators say more than 1,800 criminals used Kratos to launch approximately 15,000 phishing campaigns each month with fake Microsoft login pages designed to steal credentials. The international takedown disrupted a platform linked to victims in 35 countries and may help authorities identify additional threat actors.
Strengthen phishing-resistant authentication with passkeys or FIDO2 security keys and monitor for suspicious Microsoft account logins, as stolen credentials often fuel follow-on attacks. |
|
|
|
IoT devices often run outdated firmware or hidden third-party software, making them attractive entry points for threat actors. |
- Reduce IoT attack paths by enforcing strong device identities, eliminating default credentials, and accelerating firmware and security update deployment.
-
Strengthen software supply chain visibility by maintaining a complete IoT asset inventory and requiring vendor SBOMs to identify vulnerable third-party components.
- Contain and detect threats by segmenting IoT devices from critical business systems and continuously monitoring for anomalous device behavior, authentication activity, and network traffic.
|
Effective IoT security depends on reducing exposure before compromise through disciplined asset management, software supply chain visibility, and continuous monitoring. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|