The biggest risks aren't always what they seem. |
Today's stories reveal trusted tools turned against us, massive AWS billing confusion, and an Estée Lauder breach. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Estée Lauder Discloses Oracle HR Breach |
Estée Lauder is notifying affected individuals after attackers breached its Oracle E-Business Suite HR environment and accessed personal information. The August 2025 intrusion was confirmed in June 2026, with exposed data including names, passport details, financial account information, and employment data. |
Estée Lauder has not identified the vulnerability involved, though the timing aligns with widespread exploitation of CVE-2025-61882 as the investigation continues.
Patch vulnerabilities and continuously monitor logs for signs of unauthorized access or other suspicious activity. |
DocuSign Scam Uses Legitimate Remote Tools |
Attackers are using fake DocuSign pages to deliver legitimate remote monitoring and management (RMM) software for persistent access instead of malware.
BlueVoyant researchers found the operation targets both Windows and macOS, using staged document viewers, environment checks, and Cloudflare Turnstile verification to build trust before delivering RMM tools. The campaign has remained active for months and continues to evolve its delivery methods across numerous phishing domains.
Baseline approved RMM software across your environment and immediately investigate any new remote management agents, unexpected installations, or script activity that attempts to modify security controls. |
AWS Bug Sends Bills Into Trillions |
An AWS software bug caused projected cloud charges to briefly appear in the billions and trillions of dollars. Amazon said an error in its estimated billing system applied incorrect unit pricing, affecting only the AWS Cost Management Console and not actual usage data or customer invoices. Although no customers were overcharged, the incident highlights how faulty operational data can trigger unnecessary investigations, financial concern, and business disruption. Configure independent cost anomaly detection and validation alerts so sudden billing spikes can be quickly verified before triggering costly investigations or unnecessary response actions. |
|
|
|
Could you tell a billing bug from a cloud breach? |
|
|
|
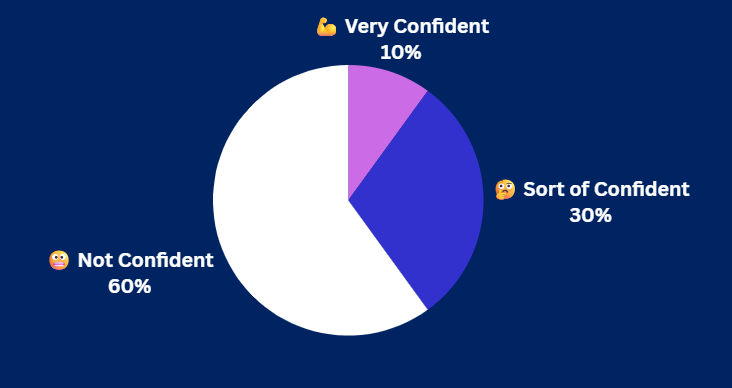
Yesterday's Pulse Check Results |
How confident are you in your AI security controls? |
|
|
|
Security Tools You Can Use |
|
|
|
Feds Shut Down 1,000+ World Cup Sites |
An international law enforcement operation has seized more than 1,000 websites and blocked nearly 2,000 domains used to illegally stream FIFA World Cup 2026 matches. Operation Offsides united partners across 54 countries to disrupt copyright infringement and illicit streaming. |
The operation follows earlier FBI warnings that fake FIFA ticketing, hospitality, and unauthorized streaming sites may expose fans to malware, credential theft, financial fraud, and other scams. Educate employees to avoid unofficial streaming and event-related websites, and use DNS filtering and web security controls to block access to newly identified malicious or high-risk domains. |
Threat Actors Target Trust Across Enterprise Systems |
UltraViolet Cyber finds today's most effective attacks target trust rather than software vulnerabilities alone. Attackers increasingly abuse valid credentials, OAuth sessions, remote administration tools, and trusted business processes to bypass traditional defenses.
UltraViolet Cyber says organizations should adopt continuous identity verification, behavioral monitoring, and Zero Trust as AI-driven social engineering weakens perimeter-based security. Review your highest-privilege accounts and critical business workflows this quarter, then add continuous monitoring and independent verification for any action that could significantly impact the organization. |
|
|
|
Secure Your Web Applications |
Web applications remain an attractive target, with adversaries exploiting vulnerabilities, misconfigurations, exposed APIs, and compromised credentials to access sensitive data. |
How to reduce web application risk: |
- Deploy a web application firewall (WAF) to block common web attacks, and secure APIs with strong authentication, authorization, and rate limiting to reduce unauthorized access.
- Integrate DevSecOps tools into the development pipeline to automate vulnerability scanning, enforce secure coding practices, validate user input, and identify security issues before deployment.
-
Continuously monitor web applications for suspicious activity, authentication anomalies, and configuration changes to detect attacks early and accelerate incident response.
|
Reducing web application risk requires layered security controls across development, deployment, and day-to-day operations to improve resilience. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|