The threat landscape doesn't take a day off. |
Today's headlines feature hijacked brands on social media for a crypto scam, mobile malware, operational disruption for taxis, and a new push to dismantle infrastructure behind ransomware attacks. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Hackers Hijack SpaceX, Starlink X Accounts |
The official SpaceX and Starlink X accounts were reportedly hijacked to promote a fraudulent cryptocurrency. The attackers allegedly used the compromised accounts to promote the fake SCATMAN cryptocurrency, generating nearly $125,000 in Ethereum before the posts were removed. |
Although unconfirmed by SpaceX or X at the time of publication, the incident reflects a growing trend of cybercriminals hijacking trusted social media accounts.
Use phishing-resistant MFA, continuously monitor for unauthorized social media account activity, and test incident response plans for account takeover scenarios. |
SAP Fixes Critical Enterprise Flaws |
SAP has released updates addressing 16 vulnerabilities across its product portfolio, including three critical flaws affecting NetWeaver, Commerce Cloud, and AppRouter.
The vulnerabilities could enable attackers to compromise sensitive enterprise systems through memory corruption, default credentials, or HTTP request smuggling. SAP reported no evidence of active exploitation at the time of publication.
Patch to the latest version, verify that default credentials have been removed, and review application and web server logs for unusual authentication attempts or suspicious HTTP request patterns. |
Cyberattack Hits Japan's Largest Taxi Operator |
A cyberattack forced Japan's largest taxi operator, Nihon Kotsu, to disconnect parts of its infrastructure. The attack disrupted taxi dispatch, web bookings, reservation management, telephone dispatch services, and other internal systems, affecting customers across multiple regions. The incident remains under investigation, and no threat actor had claimed responsibility at the time of publication. Review business continuity plans for customer-facing services and ensure critical systems can be isolated without halting essential operations. |
|
|
|
What's your biggest concern about a social media account takeover? |
|
|
|
Yesterday's Pulse Check Results |
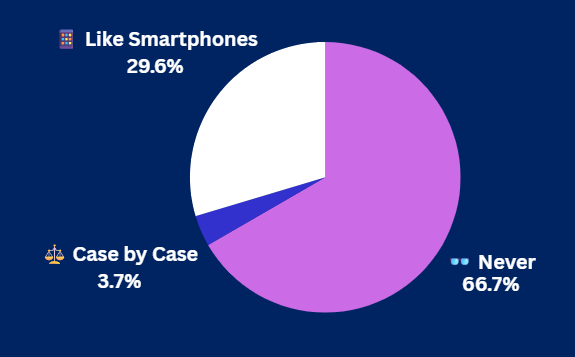
Should smart glasses be allowed in sensitive facilities? |
|
|
|
Security Tools You Can Use |
|
|
|
Android Malware Abuses Accessibility Controls |
An Android malware campaign that is tricking users into installing fake banking and government apps that can give attackers extensive remote control over infected devices.
Researchers at Group-IB identified the RedHook malware targeting users in Vietnam and Indonesia by impersonating trusted organizations and tricking victims into granting Android Accessibility permissions. |
The campaign remains active in the wild at the time of publication. Configure MDM policies to restrict Accessibility permissions for unmanaged apps and train employees to verify unexpected app installation requests through official channels. |
Treasury Targets Ransomware Infrastructure |
The U.S. Treasury sanctioned a VPN provider, its administrator, and a malware cryptor developer for allegedly enabling ransomware attacks. They targeted infrastructure and services that help cybercriminals hide their identities, evade detection, and attack victims.
This Treasury action follows Operation Saffron, which dismantled the VPN network and seized 33 servers across 27 countries.
Review threat intelligence feeds and firewall logs for connections to previously identified criminal infrastructure, and update vendor risk assessments to account for third-party services that may knowingly support cybercriminal activity. |
|
|
|
You can’t solve identity security in isolation. The Hybrid Identity Protection Conference puts you in the room with experts and a community that understand the stakes. You’ll go home with fewer dead ends, better answers, and more confidence in the decisions you make next. 🧭 CISO sessions to drive business decisions, communication, and resilience
⚠️ Crisis management sessions to keep teams focused when seconds count 🎓 Masterclasses to help you harden identity systems before a crisis happens 🔬 Identity security research to help you close attack paths sooner 🗝️ Keynotes that widen the lens on the intersection of cyber and human behavior |
|
|
|
How Confident Are You in Your Cyber Resilience? |
Cyber resilience has become a strategic priority as cyberattacks continue to target organizations of every size and industry. |
How to strengthen your cyber resilience: |
- Protect business-critical assets by prioritizing crown-jewel systems, segmenting high-value environments, and maintaining regularly tested, offline immutable backups.
-
Improve organizational resilience by continuously monitoring for threats and validating incident response capabilities through regular tabletop exercises and simulations.
-
Ensure recovery objectives align with business risk by routinely testing recovery processes and confirming that RTOs and RPOs support operational continuity and executive expectations.
|
Regularly testing these capabilities before a crisis occurs can help reduce downtime, financial impact, and the blast radius of a successful attack. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|