AI isn't the only story today. |
Today’s stories cover shifting AI policies, persistent healthcare threats, sophisticated phishing campaigns, and browser-based deception.
Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Claude AI Returns After White House Review |
Anthropic is restoring access to its Claude Fable 5 and Mythos AI models after U.S. officials lifted a two-week export freeze. A temporary freeze followed Amazon’s jailbreak finding, but Anthropic says new safeguards now block the bypass in more than 99% of cases. |
The incident highlights how quickly access to frontier AI models can change, requiring organizations to plan accordingly.
Include contingency plans for AI-dependent workflows by identifying approved backup models and documenting when teams should switch if access to a primary AI platform becomes restricted. |
Healthcare Faces Relentless Cyberattacks |
Healthcare remains the most targeted industry, with SonicWall reporting higher malware, ransomware, and intrusion activity than any other sector.
The industry averaged more than 102,000 malware hits per firewall in the first half of 2026 as attackers exploited remote access tools, legacy vulnerabilities, and connected medical devices. With 16.6 million ransomware detections across 10 active ransomware families, healthcare remains an attractive target because downtime can directly impact patient care and operations.
Audit internet-facing remote access services, segment medical IoT devices from clinical systems, conduct continuous third-party risk assessments, and require phishing-resistant MFA. |
Microsoft Uncovers Chrome Search Hijacker |
Microsoft uncovered a fake Perplexity AI Chrome extension that redirected users' searches through attacker-controlled servers before reaching legitimate search engines.
Organizations relying on browser extensions for productivity or AI workflows should treat them as potential attack vectors and include them in software governance and security reviews. Although Google removed the extension, the incident shows attackers can abuse trusted browser features and official app stores to collect sensitive browsing data.
Audit managed browsers for unauthorized extensions and restrict extension installations to an approved allowlist wherever possible. |
|
|
|
What's really driving frontier AI restrictions? |
|
|
|
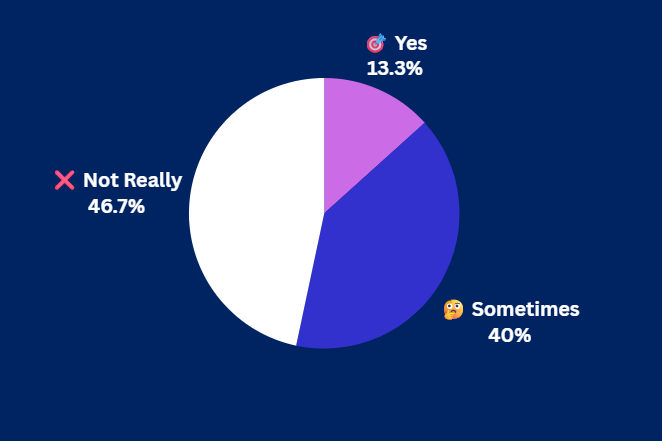
Yesterday's Pulse Check Results |
Do large bounties actually help catch state-sponsored hackers? |
|
|
|
Security Tools You Can Use |
-
Agentic AI-powered, continuous web application penetration testing. A scalable, continuous, deep, and robust pentest solution, fully aligned with your unique business context. Learn More
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
-
Build, deploy, and optimize in the cloud — master GKE, FinOps, and Google Cloud development for 87% off today.
|
|
|
|
Cisco Talos Exposes ARToken Phishing Kit |
Cisco Talos analyzed ARToken, a phishing platform that abuses Microsoft 365 OAuth device code authentication to steal session tokens and maintain account access.
Closely tied to the EvilTokens ecosystem, ARToken combines phishing automation, advanced evasion, and built-in business email compromise (BEC) capabilities for persistent access to Microsoft 365 environments. |
Its use of legitimate Microsoft infrastructure and convincing SharePoint lures makes the attacks more difficult for users and traditional defenses to detect.
Monitor OAuth device code authentication, review mailbox forwarding rules and token activity for anomalies, and require employees to use a secondary verification method for financial requests. |
GitHub Repos Trick AI Coding Agents |
Mozilla researchers showed how a seemingly legitimate GitHub repository could trick Anthropic's Claude Code into executing a hidden payload that opened a reverse shell. The proof-of-concept shows how AI coding assistants can execute malicious commands while performing routine setup tasks. As organizations adopt these tools, security controls should extend beyond just code review to include runtime protections and least-privilege execution. Configure AI coding agents to run in isolated, sandboxed environments with restricted network access and require human approval before executing shell commands or setup scripts from unfamiliar repositories. |
|
|
|
Your logs are growing. Your SIEM bill does not have to.
Scanner provides security teams with fast, searchable visibility across massive datasets so they can investigate threats faster, improve detection, and control log storage costs. |
|
|
|
How secure is your healthcare environment? |
Healthcare organizations remain prime targets as threat actors exploit legacy systems, remote access infrastructure, and connected medical devices. |
How to harden healthcare defenses: |
- Use Zero Trust solutions to continuously verify identities and devices, enforce phishing-resistant MFA, and restrict remote access.
-
Segment medical IoT devices, prioritizing patching or virtual patching for legacy systems, and use ransomware protection solutions.
- Maintain tested and immutable offline backups, and test IR plans with simulations, not just tabletops.
|
Focusing on these security fundamentals helps organizations reduce overall exposure and limit blast radius. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|