Today's cybersecurity headlines share a common theme. |
Whether it's protecting identities, securing transactions, or proving trust, the latest developments reveal where organizations are under the most pressure. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Aflac Japan Attack Exposes Sensitive Data |
Aflac disclosed a breach at its Japan subsidiary that exposed customer, policy, and bank account data. This incident highlights that insurers remain attractive targets for attackers seeking financial and personal data. |
The investigation remains ongoing, and Aflac has not yet disclosed the total number of individuals impacted.
Review privileged account activity for unusual access patterns and ensure phishing-resistant MFA protects all administrative accounts, especially those with access to customer financial and policy data. |
Citrix NetScaler Vulnerability Exposes Memory |
watchTowr disclosed a high-severity Citrix NetScaler flaw that lets unauthenticated attackers leak memory from internet-facing SAML IdP appliances.
The vulnerability could expose authentication data, memory pointers, or other sensitive information while also enabling denial-of-service conditions through crafted requests. Researchers did not report any active exploitation, but they did show a proof-of-concept.
Patch affected NetScaler appliances, disable unused SAML IdP functionality, and monitor authentication activity for signs of exploitation. |
Feds Put $10M Bounty on Russian Hackers |
The DOJ is offering a $10 million reward for information on two Russian-linked groups targeting Signal and WhatsApp users. Attackers compromised thousands of accounts by impersonating Signal support and stealing backup recovery keys without breaking encryption. The campaigns have primarily targeted government officials, military personnel, journalists, NGOs supporting Ukraine, and security researchers. Train employees to never share messaging app recovery keys or verification codes and verify all support requests through official channels before taking action. |
|
|
|
Do large bounties actually help catch state-sponsored hackers? |
|
|
|
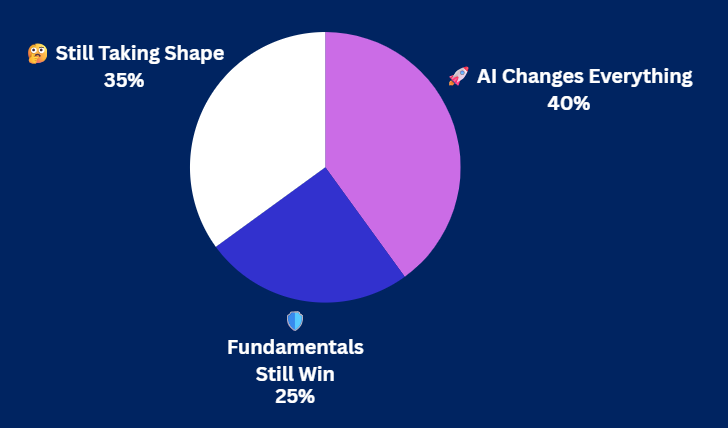
Yesterday's Pulse Check Results |
Which statement best matches your view? |
|
|
|
Security Tools You Can Use |
-
Build your skills — earn your CompTIA CSIE with CySA+, CASP, Security+, and Pentest+ training for 74% off.
-
Find out how security teams gain complete visibility across cloud environments and detect issues before they become outages or incidents.
-
Discover how continuous AI-powered penetration testing helps uncover exploitable risks before attackers do—at a fraction of traditional testing costs.
|
|
|
|
Silent Swap Steals Crypto Through Chrome |
McAfee uncovered a crypto theft campaign using a fake Google Notes extension to replace wallet addresses during transactions. The malware bypasses Chromium security protections, abuses excessive browser permissions, and uses blockchain-based C2 to make detection and takedowns more difficult. |
Because cryptocurrency transactions are irreversible, the active campaign can turn a single unnoticed wallet address swap into permanent financial loss.
Install extensions only from official stores, apply zero trust principles, and verify wallet addresses on a trusted device before approving crypto transactions. |
SOC 2 Shapes Enterprise Buying Decisions |
Enterprise buyers increasingly require SOC 2 audits and compliance evidence instead of relying on vendor security claims. Organizations now expect audit reports, security documentation, and proof that security controls are operating effectively, with SOC 2 serving as an early procurement requirement. Vendors without SOC 2 often face longer sales cycles as buyers increasingly evaluate audit scope and distinguish between Type I and Type II reports. Treat SOC 2 as evidence of operational maturity by keeping audit reports, supporting documentation, and control evidence readily available for security reviews. |
|
|
| Strengthen Regulatory Compliance |
Regulatory requirements continue to evolve, making it essential to integrate compliance into daily security operations to reduce risk, streamline audits, and build customer trust. |
How to strengthen compliance programs: |
-
Use GRC tools to automate compliance by maintaining an up-to-date inventory of regulatory requirements, collecting control evidence continuously, and simplifying audit preparation.
-
Continuously assess internal and third-party risk by monitoring security controls, reviewing access permissions, and performing ongoing vendor risk assessments to identify compliance gaps early.
-
Build a compliance-focused security culture by documenting and testing incident response plans regularly and providing role-based security and compliance training for employees.
|
Embedding these practices can help organizations improve resilience, reduce audit friction, and demonstrate measurable governance. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|