Not every threat starts with malware. |
Today’s headlines reveal what happens when trusted vendors, familiar platforms, AI ecosystems, and even your own employees become part of the attack surface.
Tell us what content you want to see on TechRepublic by taking this quick survey. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Klue Breach Hits Cybersecurity Firms |
A compromised Klue credential exposed Salesforce data across multiple organizations, including several cybersecurity firms. Attackers used stolen OAuth tokens to execute nearly 1,000 Salesforce API queries in 15 minutes, exposing CRM data over a six-hour period. |
Huntress has warned impacted companies to watch for targeted phishing campaigns using stolen Salesforce data.
Regularly review OAuth-connected applications, remove unused integrations, conduct third-party risk assessments, and enable alerts for unusual API activity to detect suspicious access early. |
Apple Flaw Exposes Millions of iPhones |
Researchers disclosed usbliter8, a hardware-level exploit affecting millions of older iPhones. The SecureROM flaw cannot be patched and enables code execution before Apple’s security controls load. Like Checkm8, the physical-access exploit shows how hardware vulnerabilities can persist for years. Identify any A12 or A13-based devices in your environment and prioritize hardware refresh plans for users. |
Researchers Flag AI Plugin Trust Risks |
Researchers found 23 ClawHub plugins published under unofficial @openclaw and @clawhub namespaces. While no malicious code was found, the plugins could execute code and access APIs, making trusted-looking abuse possible.
The discovery highlights growing trust and software provenance risks in AI ecosystems. Add AI plugins, agent extensions, and MCP servers to your software asset inventory and require publisher verification checks before approving them for production use. |
|
|
|
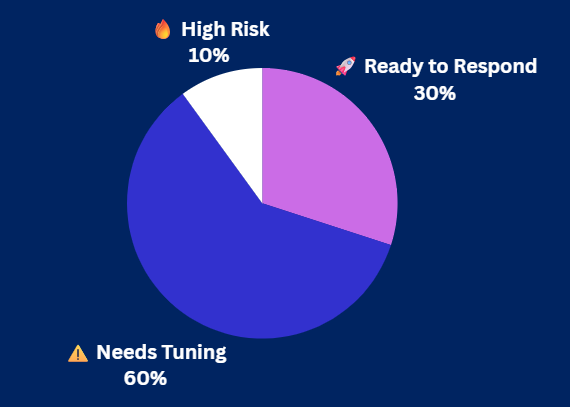
How confident are you in the security of your organization's hardware devices? |
|
|
|
Yesterday's Pulse Check Results |
How confident are you in your organization's ransomware defenses? |
|
|
|
Security Tools You Can Use |
|
|
|
CodeStorm Targets Microsoft 365 Accounts |
Researchers at ZeroBEC dissected a CodeStorm phishing campaign designed to evade detection and steal Microsoft 365 credentials. The attack uses rotating infrastructure to identify Microsoft 365 tenants, validate credentials, and support MFA bypass. |
This campaign also highlights how modern phishing kits are becoming harder to detect by mimicking legitimate logins.
Combine zero trust access controls with Entra 50126 monitoring to detect credential replay attacks sooner. |
AI Builders Create New Security Gaps |
Employees are increasingly deploying AI tools and automations, expanding organizations' attack surfaces. Vanta found that builder-focused roles grew 311% year over year, with those organizations adopting AI vendors 73% more frequently and using 42% more third-party vendors. As AI adoption expands beyond engineering into business teams, organizations face growing risks from shadow AI, unvetted tools, and risky integrations that can bypass traditional security controls. Create a lightweight intake process for AI tools and automations that allows employees to register new solutions in minutes rather than days, making security oversight easier without slowing adoption. |
|
|
|
Secure Your Small Business |
Small businesses remain a prime target for cybercriminals because they often have fewer security resources than larger organizations. |
How to reduce risk for your business: |
- Enable phishing-resistant MFA and use password managers to reduce the risk of account compromise.
-
Keep software updated, segment networks, and use privileged access management (PAM) tools.
- Regularly back up critical data and provide employees with security awareness training.
|
Taking these simple steps today can help your business reduce risk and strengthen resilience. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|