Trust is proving to be a favorite target. |
From developer platforms to website plugins and network devices, today's threats show how attackers continue exploiting what organizations rely on most.
Tell us what content you want to see on TechRepublic by taking this quick survey. Read past newsletters here. | |
|
|
Here’s what you need to know: |
|
|
|
3 Million Texans Exposed in Breach |
An incident involving a third-party vendor exposed personal information tied to more than 3 million Texas hunting and fishing license holders. Although Social Security numbers, financial data, and dates of birth were not exposed, attackers may have accessed driver’s license information and passport numbers. |
The exposed information could be used in targeted social engineering attacks.
Conduct continuous third-party risk assessments and conduct tabletop exercises. |
New Ransomware Exploits Backup Gaps |
A Prinz Eugen ransomware variant encrypts recently modified files first and leaves no ransom note.
By targeting recently modified files first, Prinz Eugen increases the risk that active data, including databases and cloud-synced files, will be encrypted before organizations can capture a clean backup, creating potential recovery gaps. Researchers also found the malware can delete original files after encryption and evade traditional ransomware triggers, reinforcing the need for behavioral-based detection.
Run a recovery test on files modified within the last 24 hours to verify your backup and ransomware response plans can protect active business operations. | Attackers Poison 10,000 GitHub Repos |
Researchers uncovered a GitHub malware campaign involving more than 10,000 repositories distributing Trojan-infected ZIP files. Threat actors cloned legitimate repositories and inserted malicious download links to trick developers into downloading malware.
GitHub has already deleted some of the repositories. Add a sandbox analysis step to your software validation process and scan downloaded archives as complete packages before allowing them into development environments. |
|
|
|
Automated pentesting proves only the assets it can safely exploit. Your business-critical, restricted, and air-gapped systems, the ones the board cares about most, stay unchecked. Proving exploitability everywhere takes a different method: testing each CVE's TTP chain against your real controls. No live exploit required. |
|
|
|
How confident are you in your organization's ransomware defenses? |
| |
|
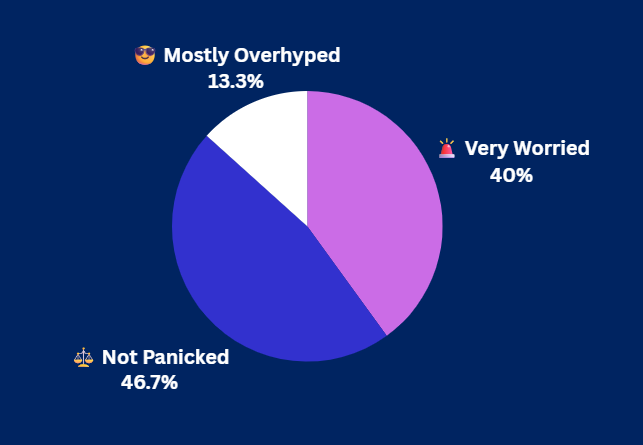
Yesterday's Pulse Check Results |
The "Patch Apocalypse" Is Coming. How worried are you? |
|
|
|
Security Tools You Can Use |
-
We’re in a Patch Apocalypse. That Means These Three IT Excuses Won’t Work Anymore. Read more
-
Security work is hard enough without chasing project updates across five different tools. See how ClickUp can help.
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
|
|
|
|
Botnet Takes Over D-Link Routers |
AryStinger has compromised more than 4,000 outdated D-Link routers, turning them into attacker-controlled proxies. Researchers found the malware exploits years-old vulnerabilities in unsupported D-Link routers, allowing threat actors to build a distributed infrastructure for attacks. |
A more advanced variant targeting NAS devices suggests the operators are also expanding their capabilities.
Audit your network for end-of-life routers and internet-facing devices, then prioritize replacing unsupported hardware. |
WordPress Plugin Exposes Sensitive Data |
A Gravity SMTP vulnerability exposes sensitive data from 100,000+ WordPress sites. The flaw exposes credentials, API keys, and other sensitive data that attackers can use to compromise services.
Researchers said more than 17 million exploitation attempts have been blocked at the time of publication. Search your web server logs for suspicious requests and rotate any email service credentials stored in the plugin. |
|
|
| Stay ahead of every threat.
Your log volumes grow daily. Scanner provides the visibility and context needed to investigate faster, accelerate detections, and respond with confidence. Search massive datasets in seconds, cut costs, and focus on threats that matter most. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|