Some risks arrive quietly. Others make headlines. |
Today’s stories span a SaaS data breach, a server takeover vulnerability, shifting AI directives, and the growing influence of machine-speed threats.
Tell us what content you want to see on TechRepublic by taking this quick survey. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
137K School Staff Records Exposed |
A breach at education technology provider Infinite Campus exposed personal data from more than 137,000 school staff accounts after attackers compromised its Salesforce environment.
According to Have I Been Pwned, the exposed records included names, email addresses, phone numbers, physical addresses, usernames, and support ticket information, but no student records. |
The incident shows how third-party SaaS breaches can still create phishing, credential theft, and social engineering risk even when core school systems are not compromised.
Review third-party SaaS integrations and prioritize phishing-resistant MFA, least-privilege access controls, and continuous monitoring. |
LiteSpeed cPanel Plugin Flaw Enables Root Access |
A vulnerability impacting LiteSpeed’s cPanel plugin is being actively exploited in the wild. The flaw allows attackers with limited access to gain root privileges and potentially take over entire servers.
Attackers are actively exploiting the flaw to bypass CloudLinux CageFS protections, and patches are now available. Search server logs for unusual bursts of requests involving the generateEcCert and packageUserSize functions, as these patterns may indicate active exploitation attempts or ongoing compromise. |
Anthropic Shuts Down AI Models Worldwide |
Anthropic pulled two AI models after a U.S. export-control order restricted access for foreign nationals. The incident marks a notable example of government intervention affecting the availability of a frontier AI model after its release. It also introduces new concerns around AI vendor stability, compliance requirements, and the potential for nationality-based access restrictions on advanced AI systems. Add AI provider regulatory risk to vendor assessments and business continuity plans, including documented fallback models and contingency workflows if a critical AI service becomes unavailable with little notice. |
|
|
|
Your primary AI model goes offline overnight. Biggest concern? |
|
|
|
Yesterday's Pulse Check Results |
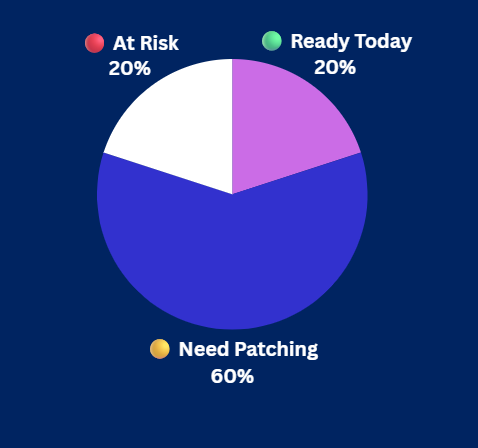
If a critical RCE dropped this afternoon, how exposed would your organization be? |
|
|
|
Security Tools You Can Use |
-
Take a 2-minute survey on Cisco Secure Access and share your perspective on today’s security challenges.
-
Find out how security teams gain complete visibility across cloud environments and detect issues before they become outages or incidents.
-
See how organizations securely share, govern, and unlock the full value of their data without adding operational complexity.
|
|
|
|
|
Big Tech Turns Clicks Into AI Training |
Your searches, clicks, and purchases help train AI systems and fuel behavioral profiling. Privacy experts warn that most people have limited visibility into how their data is collected, shared, and repurposed, despite agreeing to lengthy privacy policies and terms of service. |
Behavioral data also fuels consumer profiling, targeted advertising, and automated decision-making.
Audit your devices and accounts by removing unused permissions, disabling unnecessary tracking, and reviewing connected devices. |
Zscaler Warns of Machine-Speed Attacks |
According to Zscaler, AI is helping attackers identify vulnerabilities and execute attacks at unprecedented speed.
Attackers are chaining multiple lower-severity weaknesses into larger attack paths, creating new challenges for defenders as AI makes these techniques faster and easier to execute. Organizations should prioritize visibility, attack path analysis, automated detection, zero trust, segmentation, and continuous validation to limit attacker movement and reduce breach impact.
Review your top 20 externally accessible assets and map potential attack paths between them. |
|
|
|
How Well Are You Managing AI Risk? |
Artificial intelligence is transforming how organizations operate, but it is also creating new security risks. From data leakage to AI-powered attacks, unmanaged AI adoption can quickly create security and compliance risks. |
-
Establish AI governance with clear usage policies and visibility into approved and unapproved AI tools.
-
Protect sensitive data by enforcing DLP controls and evaluating how AI vendors handle submitted information.
- Train and monitor continuously to reduce risks from AI-driven threats, policy violations, and data exposure.
|
As AI adoption accelerates, organizations that establish guardrails now will be better positioned to manage the security, compliance, and operational risks that follow. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|