Trust is the thread running through today’s edition. |
From AI gateways and search results to government chats, privacy penalties, and cybercrime cash pipelines, the systems meant to connect and protect are under pressure. Tell us what content you want to see on TechRepublic by taking this quick survey.
Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Coupang Slammed With $409M Privacy Penalty |
South Korea hit e-commerce giant Coupang with a record $409 million fine over a massive data breach and unlawful user tracking. Authorities say a former developer retained access credentials after leaving Coupang and used them to access systems, exposing personal data tied to roughly 37.5 million accounts.
|
Regulators attributed the breach to weak security controls rather than a sophisticated attack, leaving the company facing a record fine, customer compensation costs, and reputational damage. Regularly audit and revoke all privileged credentials immediately after employee departures, and implement automated access reviews to reduce long-term insider risk exposure. |
Threat Actors Claim 650K Tchap Messages Exposed |
French authorities are investigating a breach of the government messaging app Tchap after a threat actor claimed access to more than 650,000 messages and 73,000 accounts.
While encrypted private chats reportedly remained protected, investigators are assessing whether messages, files, metadata, and government contact information were exposed through public rooms. The investigation into the incident is ongoing at the time of publication.
Monitor for unusual account activity in collaboration platforms and require phishing-resistant MFA for all privileged accounts. |
CISA Warns of LiteLLM AI Gateway Attacks |
CISA has warned of active exploitation targeting a command injection flaw in the LiteLLM AI gateway. The vulnerability can be chained with an authentication bypass vulnerability to enable unauthenticated remote code execution against exposed AI gateways.
This incident highlights how AI gateways can expose sensitive systems when AI agents lack proper service account governance. Inventory every AI agent and gateway in production, assign a named human owner to each, and review whether its permissions exceed the minimum data access required for its intended function. |
|
|
|
Do massive breach fines actually improve security? |
|
|
|
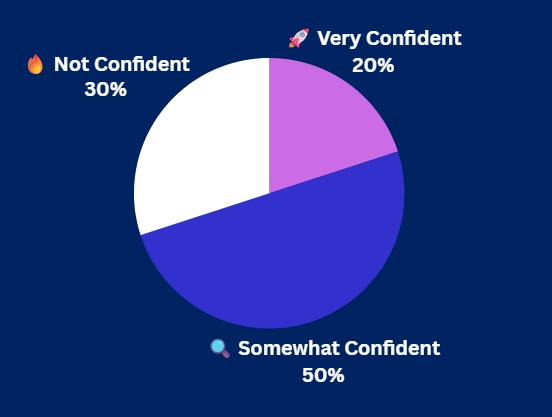
Yesterday's Pulse Check Results |
How confident are you in your organization's ability to stop a zero-day? |
|
|
|
Security Tools You Can Use |
|
|
|
Google Targets AI Search Manipulation |
Google updated its spam policies after fabricated content surfaced in AI-generated search responses. For Australian businesses, manipulated AI answers can present false or biased information as fact, creating risks to consumer trust and regulatory compliance. |
At the recent Zenith Live conference, several conversations I had around poisoned AI search results centered on the same concern: disinformation and reputational damage.
Audit high-ranking brand and product pages for biased listicles, unsupported claims, or prompt-injection-style wording that could trigger AI search spam scrutiny. |
Cybercrime Laundering Network Taken Offline |
Authorities dismantled AudiA6, a cryptocurrency laundering service linked to more than $380 million in ransomware and cybercrime proceeds. Authorities linked AudiA6 to more than 15 ransomware investigations worldwide.
The takedown resulted in arrests, domain seizures, cryptocurrency freezes, and the recovery of thousands of records tied to money mule accounts, giving investigators new insight into broader criminal networks. Review cryptocurrency transaction monitoring rules for links to sanctioned mixers, mule accounts, and high-risk exchange activity, then share indicators with fraud and threat intelligence teams for cross-functional analysis. |
|
|
| This Is Where the Channel Does Business.
ChannelCon is where channel leaders trade notes, pressure-test ideas and get intel you won’t find online. Save $100 when you register by July 1—and get a full year of GTIA membership.
Take your MSP to the next level with vendor-neutral educational sessions on AI, cybersecurity, and more. Connect with potential partners at the Technology Vendor Fair; engage with peers facing the same challenges you are—and close it out at the 80s party at the Rady Shell. This is what GTIA membership feels like at full volume. |
|
|
|
Is Your Browser a Weak Link? |
Browsers are a key part of the SMB attack surface, with threat actors leveraging malicious extensions, fake websites, browser-based malware, and stolen session cookies to bypass traditional security controls. |
How to reduce browser-based risk: |
-
Keep your browser updated by enabling automatic updates and enhanced safe browsing features to block malicious sites.
-
Manage extensions, credentials, and access controls by removing unnecessary browser add-ons, using a password manager, and implementing Zero Trust solutions to continuously verify users and devices.
-
Reduce exposure through good browsing hygiene by separating work and personal browsing activities and periodically clearing cookies and active sessions.
|
Strengthening browser security helps reduce credential theft, shrink attack surface exposure, and improve overall cyber resilience. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|