Attackers aren’t slowing down |
Today’s stories include hosting server flaws, AI runtime security gaps, certificate disruptions, and rebuilt darknet marketplaces.
Help shape our latest TechRepublic research by taking this quick survey. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
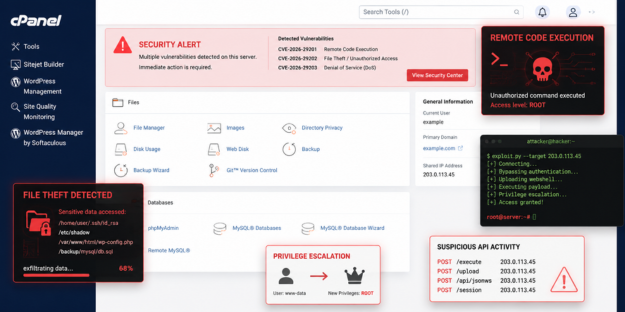
cPanel patched three vulnerabilities that could enable file theft, remote code execution, and denial-of-service attacks on vulnerable servers.
The flaws follow another recently exploited cPanel vulnerability and could increase risk in shared hosting environments. |
cPanel did not report any exploitation in the wild at the time of publication. Apply patches and review cPanel API activity, Perl process execution, and file permission changes for unusual behavior. |
AWS Rex Targets AI Runtime Threats |
AWS open-sourced Trusted Remote Execution (Rex), a runtime framework designed to limit what AI-generated scripts can do at the system level. It uses Cedar policy enforcement to restrict AI-generated system actions and reduce risks tied to prompt injection and unsafe AI behavior. Rex secures the runtime layer but leaves data governance and compliance gaps tied to authorization, auditing, and data access controls.
Map AI controls against both runtime risks and data-layer governance requirements to identify where agentic AI systems still lack enforceable authorization and audit visibility. |
Let’s Encrypt Pauses Certificate Generation |
Let’s Encrypt temporarily halted certificate issuance after identifying an issue tied to its upcoming Generation Y root infrastructure.
The outage disrupted production and staging ACME services before Let’s Encrypt restored issuance through a rollback to its Generation X root infrastructure. This incident highlights how certificate trust chain issues can impact automated renewals, TLS handshakes, and application availability across environments.
Review certificate renewal logs, validate trust chains, and test backup certificate authority workflows before future root infrastructure transitions occur. |
|
|
|
How Exposed Is Your Data Layer? |
|
|
|
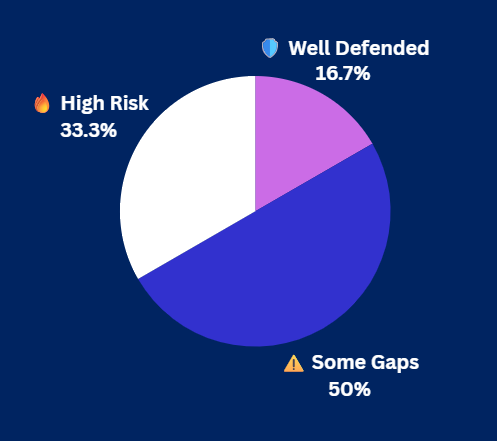
Yesterday's Pulse Check Results |
If ShinyHunters targeted your organization tomorrow… |
|
|
|
Security Tools You Can Use |
-
Help shape our latest TechRepublic research by taking this quick survey.
-
Explore how Cisco is redefining cybersecurity with solutions designed to protect your entire digital ecosystem. Discover solutions
-
Simplify compliance — get ready-to-use security policies to help protect your business without the cost or complexity of an enterprise, all for under $100.
|
|
|
|
Authorities Bust Rebooted Crimenetwork Marketplace |
German and Spanish authorities arrested the suspected operator of a rebooted Crimenetwork marketplace that reportedly generated more than €3.6 million in illicit revenue. Authorities say the platform attracted more than 22,000 users and 100 vendors before investigators seized infrastructure, assets, and user transaction data.
|
The investigation is ongoing and the case is pending trial.
Monitor threat intelligence feeds and dark web exposure services for compromised credentials, ransomware affiliate activity, and stolen access data linked to underground marketplaces. |
Researchers Demo Air-Gapped Data Theft |
Researchers demonstrated a proof-of-concept malware technique called ODINI that uses low-frequency magnetic emissions to steal data from air-gapped systems protected by Faraday cages.
Air-gapped systems are often used across military, financial, and other critical infrastructure environments to protect sensitive operations and data. The research reinforces concerns around side-channel attacks targeting air-gapped systems.
Restrict unauthorized electronic devices near air-gapped systems and review removable media, supply-chain, and insider threat controls. |
|
|
|
Automation frameworks often become harder to maintain as coverage grows. Join TechRepublic and SmartBear on June 3, 2026 at 11:00 AM ET for a focused 30-minute technical session on building scalable test automation with TestComplete. You’ll learn how to reduce maintenance overhead, improve CI execution, and create reusable workflows that support long-term automation growth.
Join the session and walk away with practical strategies your team can apply immediately. |
|
|
|
Could Your Credentials Be on the Dark Web? |
Exposed credentials and leaked personal data continue appearing on dark web forums and marketplaces, increasing the risk of unauthorized account access and fraud. |
How to reduce your dark web exposure: |
- Enable dark web monitoring and regularly review employee and third-party account exposure for compromised credentials or suspicious activity.
-
Use phishing-resistant MFA, password managers, and unique passwords to reduce the risk of credential theft and successful account takeover attacks.
- Immediately rotate reused or exposed credentials to protect against credential stuffing attacks.
|
Monitoring leaked credentials and strengthening identity protections can help organizations reduce account compromise and credential-related security risks. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|