Trusted code and core platforms are all under pressure. |
Today’s news spans Defender false positives, source code access, LMS concerns, and a scalable spyware tool.
Take our quick AI in cybersecurity survey. Read past newsletters here. |
|
|
|
Here’s what you need to know: |
|
|
|
Microsoft Defender Flags DigiCert Certificates as Malware |
A Microsoft Defender update misclassified legitimate DigiCert root certificates as malware, triggering alerts and removing trusted certificates from Windows systems.
The issue disrupted enterprise trust stores and led some teams to initiate unnecessary rebuilds, driven by overly aggressive detection logic tied to a real DigiCert incident that introduced operational risk. |
Microsoft has released a fix for the issue in the latest version of Defender.
Update Defender to the latest version, validate certificate integrity against a known baseline, and monitor endpoints and logs for unexpected certificate or trust store changes. |
Attackers Access Trellix Source Code Repository |
Trellix disclosed unauthorized access to part of its source code repository, raising potential supply chain risk concerns. Trellix reported no evidence of exploitation or customer impact, but the incident still introduces risk given its role as a security vendor across enterprises. The company is continuing its investigation into the incident at the time of publication. Enforce strong access controls, continuously monitor repository activity, and validate code integrity while auditing logs and testing incident response plans. |
Instructure Attack Raises Potential Canvas Security Concerns |
Instructure confirmed a security incident involving a threat actor potentially impacting its Canvas platform and customer data. The company said it has found no evidence that passwords, dates of birth, or financial data were compromised as of publication.
Instructure has rotated credentials and is continuing to investigate the scope of the incident. Monitor vendor updates, rotate API keys, enforce strong access controls, and continuously review logs and integrations for suspicious activity. |
|
|
|
How secure is your source code environment? |
|
|
|
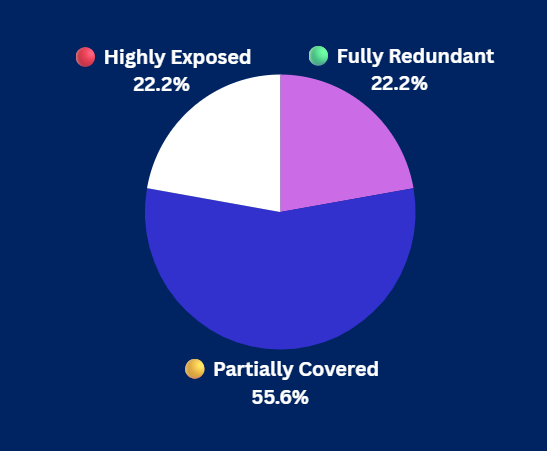
Yesterday's Pulse Check Results |
If a critical upstream service went down today… how would you hold up? |
|
|
|
Security Tools You Can Use |
|
|
|
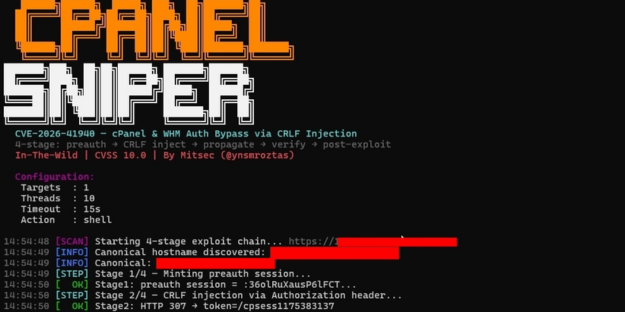
cPanelSniper PoC Exploit Enables Server Takeovers |
A weaponized proof-of-concept exploit, called cPanelSniper, is driving attacks against a critical cPanel vulnerability, with thousands of servers still potentially exposed.
The cPanel flaw allows unauthenticated root access, putting internet-facing systems at risk, with over 44,000 IPs found scanning and exploitation occurring months before the official disclosure. |
cPanel has released a patch, but the vulnerability is still being actively exploited worldwide.
Apply the latest patch, restrict cPanel access, and monitor for suspicious activity while auditing sessions and enforcing least-privilege controls. |
White-Label Spyware Powers Mobile Surveillance
|
A new Android spyware tool lets anyone launch and sell surveillance operations with minimal effort. KidsProtect gives operators near-total control over a device while posing as a parental monitoring app, and its white-label model allows multiple actors to rebrand and deploy it at scale. The tool is still available in the wild at the time of publication. Restrict app sources, enforce mobile security controls, and continuously monitor devices and permissions for suspicious activity. |
|
|
|
Fast API generation without validation leads to technical debt.
In this DZone session with SmartBear on May 21, 2026 at 11:00 AM ET, discover how to enforce testing, consistency, and governance across AI-generated APIs. Save your seat to move from speed to production-ready quality. |
|
|
|
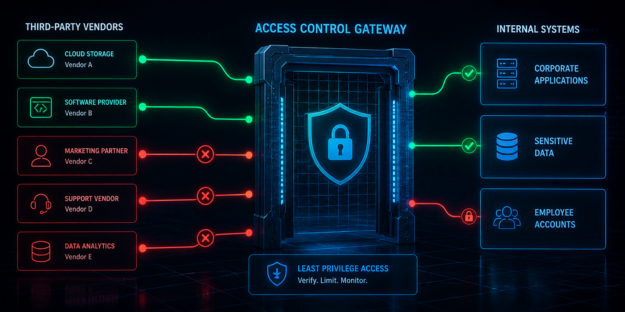
Is Your Third-Party Risk Under Control? |
Third-party incidents are increasing as attackers target vendors for indirect access, making strong vendor security and oversight essential — even when internal defenses are already solid. |
How to reduce third-party risk: |
- Regularly assess vendor risk using third-party risk tools and enforce security requirements such as MFA, logging, and breach notification policies.
-
Limit vendor access with least-privilege controls and audit integrations to remove unnecessary or risky connections.
- Continuously monitor vendor activity for anomalies and align incident response plans to enable faster detection and containment.
|
Third-party risk continues to grow with expanding integrations, making it important to control access, improve visibility, and align with vendors to reduce exposure. |
|
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|
|