Threat actors never quit trying. |
From developer platforms under scrutiny to shifting vulnerability signals and everyday tools turned attack vectors, today’s stories reveal how quietly exposure can scale. Take Cisco’s quick survey to share how you’re securing access.
Read past newsletters here. |
|
| Here’s what you need to know: |
|
|
Vercel Investigates Possible Data Exposure |
A threat actor claims to have accessed Vercel’s internal systems and is offering the alleged stolen data for sale online. Given Vercel’s role in modern pipelines, a compromise could expose credentials, disrupt CI/CD workflows, and create broader supply chain risk through weaknesses in access controls. |
The company has confirmed the incident, but the investigation is ongoing at the time of publication. Rotate and revoke all credentials, enforce least privilege with short-lived access, and continuously monitor and validate pipelines. |
NIST Adjusts Scoring Amid CVE Spike |
A surge in vulnerability disclosures is forcing NIST to scale back how it enriches and scores CVEs in the National Vulnerability Database.
With CVE submissions up over 260% since 2020, NIST will prioritize high-impact vulnerabilities, leaving many others without full context or standardized scoring. This shift pushes security teams to validate inconsistent CNA data and reprioritize remediation, while increasing the risk of blind spots for vulnerabilities lacking full NVD analysis.
Cross-reference vendor advisories and threat intelligence, standardize internal scoring, and automate workflows to maintain consistent vulnerability prioritization despite gaps in NVD enrichment. |
Fiverr Files Exposed via Search Indexing |
Researchers have uncovered a potential data exposure issue where sensitive Fiverr user files may be publicly accessible via Google search. Publicly accessible Cloudinary links may have exposed PII-containing documents to indexing and discovery without authentication.
Fiverr stated the documents came from buyer–seller communications, but cybersecurity leaders have expressed skepticism about that explanation. Audit third-party storage configurations to enforce private-by-default access and implement signed, time-limited URLs to prevent unauthorized file exposure and indexing. |
|
|
How will NIST’s narrower vulnerability scoring impact your organization? |
|
|
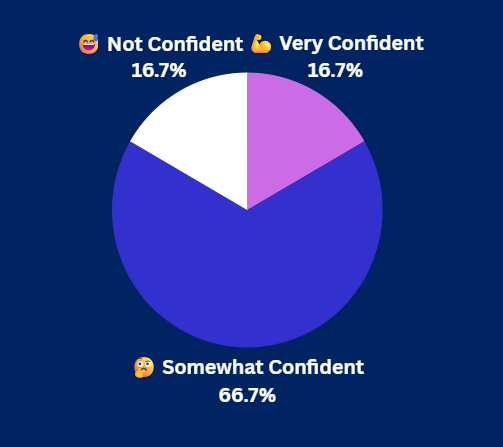
Yesterday's Pulse Check Results |
How confident are you in your website’s security posture? |
|
|
Security Tools You Can Use |
|
|
Attackers Abuse n8n for Stealth Phishing |
Cisco researchers have identified a surge in phishing campaigns abusing n8n automation workflows to deliver malware and evade detection. By abusing trusted n8n subdomains, attackers can evade defenses, tailor payloads to victims, and blend into legitimate workflows. |
The campaigns are still active in the wild at the time of publication.
Implement behavior-based email and network detection that flags automation platform activity anomalies, and validate all inbound workflow-generated links. |
Express Retail Flaw Exposes Customer Data |
A vulnerability in a retailer’s website allowed unauthorized access to customer data simply by modifying order confirmation URLs. Sequential order IDs in unauthenticated URLs allowed easy data enumeration and exposure of sensitive customer details.
The company has since patched the issue. Eliminate predictable identifiers in URLs and enforce authentication checks on all sensitive endpoints to prevent unauthorized data access at scale. |
|
|
Are Manual GRC Processes Holding You Back? |
Software supply chain attacks — such as those exploiting n8n — are increasing, exposing gaps in governance, risk, and compliance (GRC). As dependencies expand and AI-driven threats accelerate, manual GRC workflows fall short — making automation essential to maintain visibility, enforce controls, and keep pace with risk. |
Hardening GRC posture for the Supply Chain: |
- Use GRC automation solutions, centralized risk tracking and continuous monitoring to detect changes in vulnerabilities and risk posture.
-
Assess for third-party risk, conduct threat modeling, and use SBOMs to identify vulnerable dependencies and reduce overall supply chain exposure.
- Apply policy-as-code in pipelines and maintain automated audit trails for real-time compliance visibility.
|
As supply chain risks evolve, automating GRC helps improve visibility, streamlines compliance, and allows teams to focus on higher-value security efforts. |
|
|
| Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field.
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|