The attack surface keeps expanding. |
From “anonymous” platforms leaking sensitive data to everyday devices and outdated phones becoming easy targets, today’s threats are turning trusted systems into attack surfaces. Read past newsletters here. |
|
|
Here’s what you need to know: |
|
|
Anonymous Tip Platform Breach Exposes Millions of Sensitive Data |
A hacker group claims it breached P3 Global Intel, exposing over 8 million anonymous crime and school safety tips, including tipster identities and sensitive personal data.
With over 30,000 schools and multiple US federal agencies using the system, the impact spans vulnerable students, law enforcement workflows, and public trust in reporting mechanisms. |
The incident also highlights potential gaps between stated security controls and actual implementation, particularly around encryption and user tracking. Assume anonymity tools can be deanonymized. Avoid sharing identifiable details and verify vendors’ encryption and data-handling claims before use. |
Fake Resume Campaign Targets Enterprises With Credential Theft Malware |
Attackers are targeting French-speaking corporate environments with phishing emails disguised as resumes to deploy credential stealers and crypto miners.
The FAUX#ELEVATE campaign uses heavily obfuscated VBScript and trusted services like Dropbox, focusing on domain-joined systems to maximize impact. Once executed, it disables defenses and exfiltrates credentials in under 30 seconds, creating significant risk for enterprise environments.
Block or sandbox unsolicited resume attachments and restrict VBScript execution across endpoints to reduce initial compromise risk. |
Chrome 146 Fixes Multiple High-Severity Memory Vulnerabilities |
Google has released a Chrome 146 update to patch eight high-severity memory safety flaws affecting core components like WebAudio, WebGL, and WebGPU.
These vulnerabilities, including buffer overflows and use-after-free bugs, are prime targets for exploitation, especially following recent zero-days discovered soon after release. The update reinforces how quickly browser flaws can be weaponized in enterprise environments. Enable automatic browser updates and regularly audit endpoints to ensure critical patches are applied without delay. |
|
|
How fast do you apply updates to your browser? |
|
|
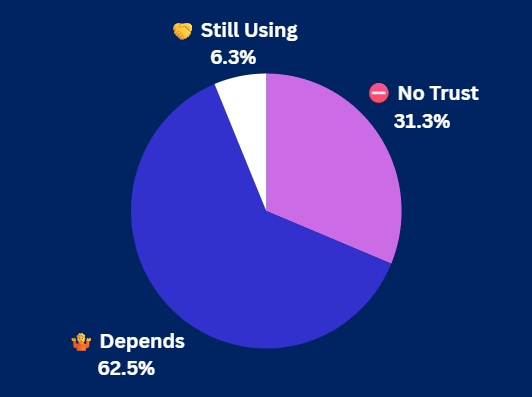
Yesterday's Pulse Check Results |
Would you use network devices made outside your home country? |
|
|
Security Tools You Can Use |
|
|
Interlock System Outage After Cyberattack Locks Out Drivers Nationwide |
A cyberattack on Intoxalock disrupted backend systems, leaving drivers across the US unable to calibrate ignition interlock devices and, in some cases, unable to start their vehicles.
Because these devices require regular calibration to function, even a short outage created immediate real-world consequences for users who depend on them for daily transportation. |
The incident highlights how attacks on connected safety systems can cascade into physical disruptions, particularly for regulated users with limited alternatives. Identify dependencies on cloud-backed or regulated devices and build contingency plans, to prevent lockouts during outages. |
New DarkSword Variant Expands Risk to Millions of iPhones |
A newly leaked version of the DarkSword exploit has rapidly evolved a previously targeted iPhone attack into a widely accessible threat, just days after earlier reports on its controlled use.
Unlike the March 19 campaign, this version requires little technical skill, making it easier to exploit outdated iPhones at scale. With millions of devices still running older iOS versions, the risk of widespread data theft has significantly increased, especially in BYOD environments. Identify and block outdated iOS devices from accessing corporate resources until they are updated to supported versions. |
|
|
Heading to RSAC? Find your Calm-pliance with Vanta.
Stop by Vanta’s booth (S-1827) for a moment of calm in the chaos of RSAC—and find out how to bring the calm to your own program. Vanta, the leading Agentic Trust Platform, combines compliance, risk, and proof in one place, with 400+ integrations and 1,400+ automated tests that keep you audit-ready.
Join Vanta’s uniquely chill kickoff to RSAC, with free food and drinks, music, and a curated space for the GRC community. Hear firsthand how companies like Ramp, Writer, and Atlassian use Vanta to save hundreds of hours and prove trust continuously, without the chaos. Save your spot! |
|
|
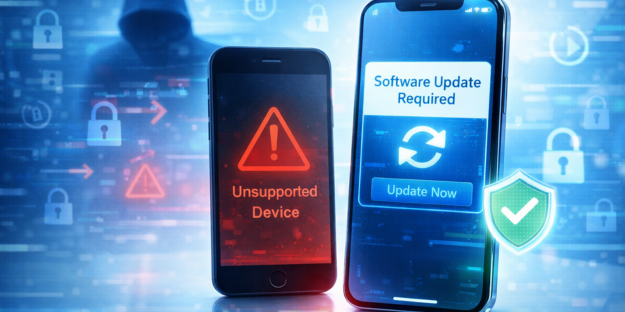
Outdated Devices Are Easy Targets for Attackers |
New exploit leaks like DarkSword are making it easier to compromise devices running older, unsupported operating systems. As security updates stop, these legacy devices become high-risk entry points for data theft, especially in enterprise and BYOD environments. |
How to protect yourself from outdated device risks: |
-
Enable automatic updates to ensure devices receive patches as soon as they are available.
- Regularly check device OS versions to identify systems that are outdated or no longer supported, as part of a zero trust strategy that continuously verifies device security posture.
-
Replace legacy devices that no longer receive security updates to reduce the attack surface.
|
Updating devices is one of the most effective ways to reduce risk against known vulnerabilities. |
|
|
| Senior Staff Writer at TechnologyAdvice |
Luis Millares is a seasoned tech writer with broad experience reviewing consumer gadgets and enterprise software, offering clear, reliable insights across the latest in technology. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|