Heads up — threats are escalating fast. |
Today’s roundup covers a Crunchyroll breach tied to third-party risk, a US router crackdown, a Mazda supply chain incident, and IRS-themed phishing campaigns. Read past newsletters here. |
|
| Here’s what you need to know: |
|
|
Crunchyroll Probes Alleged Breach Linked to Third-Party Vendor |
A hacker claims to have stolen up to 100GB of Crunchyroll data, though the company says the breach may be overstated.
Early reports link the incident to a compromised third-party vendor, potentially exposing millions of support tickets with email addresses, IP data, and user-submitted content, which could be used for targeted phishing. |
Even without confirmed ongoing access, the incident underscores how supply chain weaknesses can create outsized risk.
If you use Crunchyroll, reset your password, enable two-factor authentication if available, and be cautious of emails referencing support tickets or account issues. |
Mazda Breach Exposes Employee, Partner Data |
Mazda disclosed unauthorized access to a warehouse management system tied to parts procurement in Thailand. Though limited to 692 records and no customer data, exposed employee and partner details such as emails and IDs could enable targeted phishing and supply chain attacks.
Mazda employees and partners: Treat emails about internal systems or suppliers as suspicious, avoid unexpected links, and report them immediately. |
FCC Bans New Foreign-Made Routers Over Security Risks |
US regulators have banned the import of new foreign-made consumer routers, citing their potential use in cyberattacks and espionage.
Officials warn that vulnerabilities in these devices have already been exploited to disrupt networks, target households, and enable intellectual property theft, with concerns heightened by their widespread presence in critical infrastructure. While existing routers are unaffected, the move signals growing scrutiny of supply chain security and the risks posed by embedded hardware in everyday connectivity. |
|
|
Would you use network devices made outside your home country? |
|
|
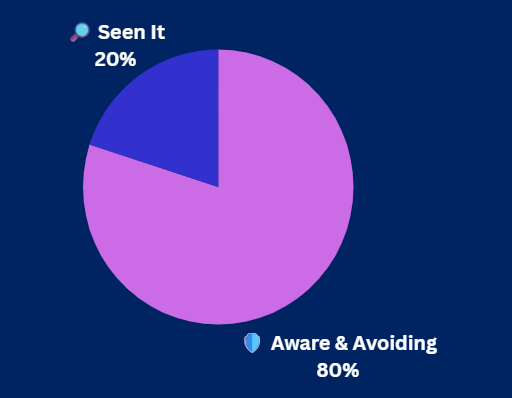
Yesterday's Pulse Check Results |
Toxic Platform Radar: Have you encountered harmful online spaces? |
|
|
Security Tools You Can Use |
|
|
IRS-Themed Phishing Campaign Hits 29,000 Users |
Microsoft warns of tax-season phishing campaigns impersonating the IRS that have impacted over 29,000 users across 10,000 organizations. Attackers use fake tax notices to steal credentials or deploy legitimate remote monitoring tools like ScreenConnect, enabling persistent access and data theft. |
The activity heavily targets finance teams, showing how trusted tools and seasonal urgency can bypass defenses.
Restrict remote monitoring tools to approved use cases and flag any unexpected installations, especially during tax season. |
Claude Desktop Flaw Enables Zero-Click RCE via Calendar |
A critical zero-click vulnerability in Claude Desktop Extensions allows attackers to execute code through a malicious Google Calendar event.
Affecting over 10,000 users, the flaw stems from how AI agents chain low-trust inputs like calendar data into high-privilege system actions without user approval, enabling full system compromise. Disable or limit high-privilege AI extensions and avoid connecting AI tools to untrusted sources like email or calendars without strict access controls. |
|
|
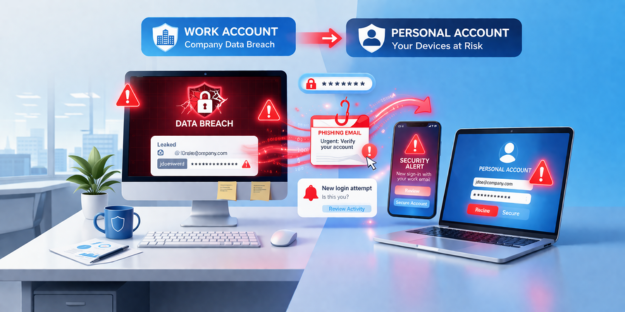
When Work Breaches Spill Into Personal Risk |
A company account breach can quickly extend beyond the workplace, exposing personal accounts through credential reuse and targeted phishing. Attackers often leverage stolen corporate data to craft convincing messages or attempt access to linked services, making individuals a key entry point for further compromise. |
How to protect yourself after a company breach: |
- Reset your work password immediately, then update any personal accounts using the same or similar credentials.
- Enable multi-factor authentication on both work and personal accounts to add a critical layer of defense.
-
Use a password manager to create and store unique passwords, preventing credential reuse across accounts.
|
A company breach doesn’t have to become a personal one, so acting quickly can significantly reduce your risk and limit how far attackers can go. |
|
|
| Senior Staff Writer at TechnologyAdvice |
Luis Millares is a seasoned tech writer with broad experience reviewing consumer gadgets and enterprise software, offering clear, reliable insights across the latest in technology. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|