The threat surface keeps expanding… from the inside out. |
Today, silent access turns into mass disruption, trusted systems become attack vectors, and automation blurs the line between innovation and abuse.
Read past newsletters here. |
|
| Here’s what you need to know: |
|
|
2.7 Million Impacted in Navia Data Breach |
A benefits provider revealed attackers accessed its systems for weeks, exposing sensitive data of millions of users. Exposed data includes SSNs, birth dates, and benefits details — valuable for identity theft and targeted attacks. |
The company has begun notifying those impacted and no threat actor group has claimed responsibility at the time of publication.
Prioritize detection engineering, specifically alerting on abnormal access to benefits and HR systems, enforce stricter data retention policies, and use DLP solutions. |
FBI Seizes Handala Sites After Stryker Attack |
Federal authorities seized infrastructure used by the Handala group after a cyberattack wiped roughly 80,000 devices at Stryker.
The group, tied to Iranian state interests, used privileged access to trigger mass device wipes via Microsoft Intune — highlighting how identity compromise can drive large-scale disruption.
While the seizure shows growing law enforcement focus, the group plans to rebuild, and organizations using centralized device management remain at risk without strong admin controls.
Enforce strict conditional access and privileged identity management (PIM) for domain and Intune admins, use privileged access management tools, and audit for unauthorized Global Admin accounts regularly. |
Global Takedown Disrupts Massive IoT Botnets |
Authorities in the U.S., Germany, and Canada dismantled infrastructure behind multiple botnets used in large-scale cyberattacks. The takedown targeted Aisuru, Kimwolf, JackSkid, and Mossad — botnets that hijacked millions of IoT devices to launch large-scale DDoS attacks. Operating as cybercrime-as-a-service, they exploited poorly secured devices to scale attacks, and are likely to rebuild quickly despite the disruption.
Continuously inventory IoT assets and enforce egress filtering to block unauthorized outbound traffic, which reduces the risk of devices being conscripted into botnets. |
|
|
Botnet Exposure Check: Could your devices be weaponized? |
|
|
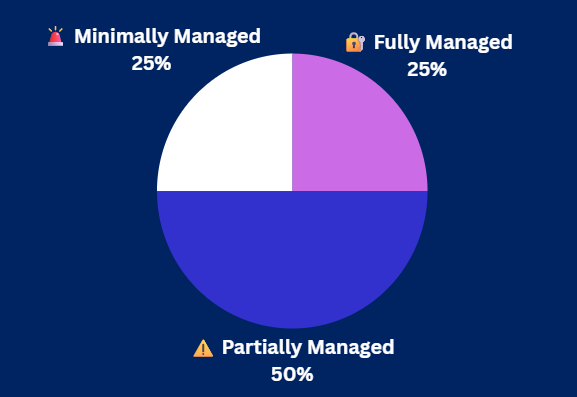
Yesterday's Pulse Check Results |
Third-Party Risk Check: How exposed is your vendor ecosystem? |
|
|
Security Tools You Can Use |
|
|
Bots and AI Power $10M Streaming Scam |
A musician pleaded guilty to running a years-long scheme using AI-generated songs and bots to steal over $10 million in streaming royalties. The scheme shows how automation, cloud infrastructure, and VPNs can bypass fraud detection at scale — exploiting platforms that rely on engagement metrics. |
With thousands of bots and billions of fake streams, it highlights growing AI-driven fraud amid rising regulatory and law enforcement scrutiny.
Implement behavioral analytics that detect anomalies in content consumption patterns — such as uniform streaming behavior or distributed bot activity across cloud environments — to identify fraud beyond traditional account-based signals. |
Insider Theft Drives $2.5M Extortion Scheme |
A former contractor was convicted for stealing sensitive company and employee data to carry out a multimillion-dollar extortion scheme. This incident highlights ongoing insider risk, especially when employees retain broad access near termination.
The case is pending sentencing at the time of publication. Implement automated offboarding that revokes access immediately, and use DLP to block or flag suspicious data transfers and audit recent activity. |
|
|
Gartner® Research: How to Secure Enterprise Agentic AI Ambition Gartner® analysts warn that rapid agentic AI adoption is outpacing enterprise security readiness. Download the report to learn key risks, required controls, and how to secure agentic AI at scale. Access the report now for deeper insight today into emerging threats. |
|
|
How Exposed Are You to Insider Risk? |
Insider threats are increasing as employees, contractors, and partners retain broad access to sensitive systems — whether through negligence or malicious intent. With ongoing layoffs, role changes, and distributed workforces, the risk of data exfiltration is growing, making strong visibility, monitoring, and access controls more important than ever.
|
How to reduce insider threat risk: |
- Use DLP and user activity monitoring to detect and block unauthorized data movement and suspicious behavior in real time.
- Enforce least privilege with regular access reviews and privileged access management to limit unnecessary or high-risk access.
- Automate offboarding and apply behavioral analytics to quickly revoke access and identify anomalies that signal insider threats.
|
Insider threats can be challenging to spot, but combining monitoring, access controls, and automation helps reduce risk. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|