Trust isn’t what it used to be. |
Today’s threats slip through familiar channels — emails you recognize, tools you rely on, devices in your pocket. From vishing-driven breaches to silent mobile exploits, attackers are scaling smarter and faster. Read past newsletters here. |
|
|
Here’s what you need to know: |
| |
Aura Breach Exposes 900K Records via Vishing |
A vishing attack against an Aura employee led to unauthorized access to a marketing database, exposing nearly 900,000 records. Although only about 35,000 records involved customers and no highly sensitive data was exposed, the incident shows how easily social engineering can bypass defenses. |
The investigation remains ongoing at the time of publication.
Implement phishing-resistant MFA, enforce least-privilege access, and regularly audit legacy systems while training employees to verify all sensitive requests. |
672K Records Exposed After Firewall Compromise |
A compromised firewall at Marquis allowed attackers to access systems, steal data from over 672,000 individuals, and disrupt dozens of financial institutions.
Because Marquis supports over 700 financial institutions, the breach had broad downstream impact, showing how a single vendor compromise can affect an entire ecosystem. The investigation into the incident is ongoing.
Enforce MFA, rotate credentials, restrict firewall access, and segment critical systems while maintaining monitored logs and tested backups for rapid ransomware response. |
ScreenConnect Flaw Enables Remote Access Hijacking |
A ScreenConnect vulnerability could let attackers hijack sessions and access systems by bypassing authentication. Because ScreenConnect is widely used with elevated privileges, the flaw could let attackers forge sessions without credentials and impact multiple downstream networks. A patch has been released and there are no reports of exploitation in the wild.
Patch to the latest version, rotate machine keys, enforce MFA, restrict access, and continuously monitor authentication activity to prevent unauthorized sessions. |
|
|
Third-Party Risk Check: How exposed is your vendor ecosystem? |
|
|
Yesterday's Pulse Check Results |
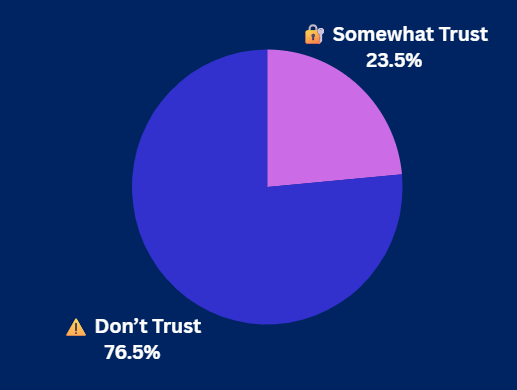
Do you trust fitness apps with your data? |
|
|
Security Tools You Can Use |
|
|
Nordstrom Account Breach Triggers Crypto Scam |
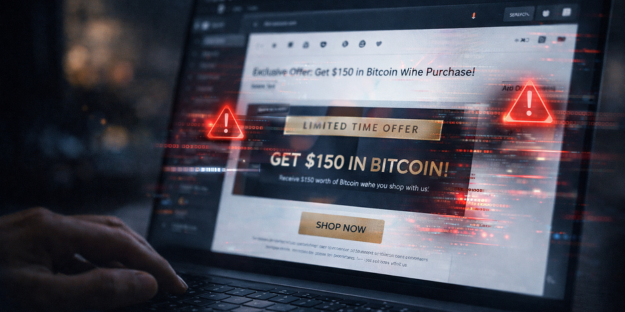
Attackers leveraged Nordstrom’s official email system to send cryptocurrency scam messages, tricking customers into transferring funds under the guise of a limited-time promotion. Because the emails came from a trusted domain, they bypassed defenses and appeared credible, increasing engagement. |
The incident highlights a growing trend of attackers compromising SaaS platforms to launch large-scale, trusted attacks. Enforce MFA, monitor for anomalous logins and email activity, and restrict access to SaaS and marketing systems with least-privilege controls. |
Millions of iPhones Exposed to DarkSword Exploit
|
A newly discovered exploit kit, DarkSword, allows attackers to silently compromise up to 270 million iPhones via infected websites targeting outdated iOS versions. Unlike targeted attacks, this watering hole technique infects users through compromised sites, making it highly scalable and hard to avoid. The fileless exploit steals sensitive data, including messages, passwords, and crypto assets, then erases traces, while its spread across multiple threat groups signals growing accessibility and risk for everyday users.
Patch to the latest iOS version and enable Lockdown Mode for high-risk users to reduce exposure to web-based exploits. |
|
|
Heading to RSAC? Find your Calm-pliance with Vanta.
Stop by Vanta’s booth (S-1827) for a moment of calm in the chaos of RSAC—and find out how to bring the calm to your own program. Vanta, the leading Agentic Trust Platform, combines compliance, risk, and proof in one place, with 400+ integrations and 1,400+ automated tests that keep you audit-ready.
Join Vanta’s uniquely chill kickoff to RSAC, with free food and drinks, music, and a curated space for the GRC community. Hear firsthand how companies like Ramp, Writer, and Atlassian use Vanta to save hundreds of hours and prove trust continuously, without the chaos. Save your spot! |
|
|
Could Your Mobile Device Be at Risk? |
Mobile devices are increasingly targeted by threats like spyware, malicious apps, and zero-click exploits, especially as more enterprise data is accessed on smartphones. As mobile becomes a more common target, strong security is essential to reduce risk and protect sensitive information. |
How to secure your mobile devices: |
-
Enable automatic updates and use mobile threat defense tools to protect against device compromise.
- Turn on phishing-resistant MFA and limit app permissions to strengthen account security and reduce unnecessary data access.
-
Avoid unsecured Wi-Fi, use a VPN on public networks, and enable encryption with screen locks to protect data from interception, loss, or unauthorized access.
|
Mobile security is an essential part of your overall defense strategy, helping reduce risk and protect sensitive data across devices and environments. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|