Attackers are getting creative — and faster. |
A destructive wiper claim hits a global medtech giant, and a WordPress flaw exposes hundreds of thousands of sites.
Meanwhile, an Active Directory bug opens the door to SYSTEM control, Microsoft races to patch dozens of flaws, and researchers reveal how easily AI agents can spill sensitive data. Read past newsletters here. |
|
| Here’s what you need to know: |
|
|
Hacktivists Claim Destructive Wiper Attack on Stryker |
A cyberattack hit medical technology giant Stryker on March 11, disrupting operations and cutting employee access to internal systems across multiple countries. The attack reportedly impacted Stryker’s Microsoft environment, locking employees in multiple countries out of devices. |
The investigation into the incident is ongoing.
Maintain offline, immutable backups, closely monitor identity and device management systems for abnormal administrative actions, and test incident response plans. |
SQL Injection Flaw Exposes 400K WordPress Sites |
A vulnerability in Elementor’s Ally accessibility plugin could allow attackers to extract sensitive data from vulnerable WordPress databases.
The flaw stems from improper input sanitization that allows a user-controlled URL parameter to be injected into an SQL query and potentially impacts over 400,000 installations. A patch has been released for the issue.
Patch to the latest version, enforce least-privilege database access, and use a web application firewall to detect and block suspicious SQL injection activity.
|
Active Directory Vulnerability Enables SYSTEM Takeover |
Microsoft patched an Active Directory Domain Services vulnerability that could allow attackers with limited access to escalate privileges to SYSTEM-level control.
The flaw allows attackers to insert crafted Unicode characters into SPN and UPN entries, creating deceptive duplicates that bypass Kerberos safeguards and potentially enable lateral movement, service disruption, or broader domain compromise. Microsoft has released a patch for the vulnerability.
Apply the latest Windows patches — especially on domain controllers — restrict who can modify SPNs, and monitor Active Directory logs for unusual SPN/UPN changes or suspicious Kerberos activity. |
|
|
Wiper Attack Reality Check: If systems were wiped tonight… |
|
|
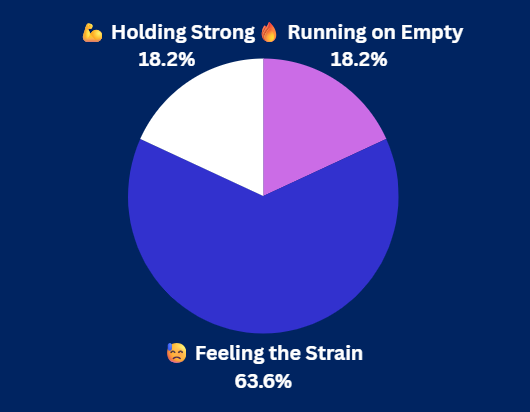
Yesterday's Pulse Check Results |
Cybersecurity Burnout Check: How close are you to the edge? |
|
|
Security Tools You Can Use |
|
|
Microsoft Patches Dozens of Windows and Office Flaws |
Microsoft’s recent Patch Tuesday fixed 78 vulnerabilities, including critical Office flaws that could allow attackers to execute code simply by previewing a malicious document.
Researchers warn two Office flaws can be exploited through the Windows Preview Pane — meaning a malicious document could trigger code execution without being opened. |
The update also fixes an Excel Copilot data leak risk and a high-severity bug discovered by an autonomous AI agent, underscoring growing AI involvement in vulnerability discovery.
Apply the latest patches, build layered defense with zero trust solutions, and temporarily disable the Windows Preview Pane if Office patches cannot be applied immediately. |
Study Shows AI Agents Leak Sensitive Data |
Researchers from MIT, Harvard, Stanford, and other institutions found that autonomous AI agents can be easily manipulated into leaking sensitive data and performing harmful actions.
In the Agents of Chaos study, researchers gave AI agents access to enterprise-style systems, including email, messaging, file storage, and shell commands. Within two weeks, attackers tricked the agents into exposing Social Security numbers, bank details, and medical records — highlighting a major governance gap as organizations deploy AI agents without controls to stop misuse.
Implement strict data-layer governance for AI agents, including authenticated access controls, and use data loss prevention solutions. |
|
|
You’re busy running your business — and so are cybercriminals, using many of the same tools, processes, and tech. Step inside the day-to-day operations of modern cybercrime groups, see how they mirror legitimate enterprises, and gain practical insight into how attackers think so you can spot and disrupt them faster. |
|
|
How Secure Is Your AD Environment? |
Active Directory (AD) is the backbone of identity and access management in many organizations, making it a prime target for attackers seeking privilege escalation and lateral movement. |
How to harden your Active Directory environment: |
-
Apply the latest patches, disable legacy authentication protocols like NTLM, and use Active Directory tools.
-
Apply least privilege, privileged access management (PAM), and tiered administrative access to limit who can make changes within Active Directory.
-
Monitor for suspicious changes to SPNs, group memberships, and authentication events while regularly auditing configurations, service accounts, and permissions for potential weaknesses.
|
Active Directory security requires ongoing management, including limiting privileges, monitoring identity changes, and addressing legacy weaknesses to reduce the risk of broader domain compromise. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|