The pressure is building across the security landscape. |
From database privilege flaws and collaboration app bugs to AI reshaping both attacks and workloads, today’s stories reveal where defenders may be most exposed — and what trends are quietly redefining the threat environment. Read past newsletters here. |
|
|
Here’s what you need to know: |
|
|
Microsoft Warns of .NET DoS Vulnerability |
Microsoft released an emergency patch for a newly disclosed .NET vulnerability that could allow attackers to remotely crash applications. The flaw involves an out-of-bounds memory read triggered by a crafted request that could crash vulnerable .NET applications and cause a denial-of-service condition. |
Microsoft has released a patch and there are no reports of exploitation at the time of publishing. Patch .NET environments to the latest versions, verify updated runtimes in build and deployment pipelines, and implement monitoring, rate limiting, and WAF protections. |
SQL Server Flaw Enables Privilege Escalation |
Microsoft disclosed a vulnerability in SQL Server that could allow attackers with limited database access to escalate privileges to full administrative control. The flaw stems from improper access control, affects SQL Server versions 2016–2025, and could allow attackers to gain sysadmin privileges. A patch has been released for the vulnerability.
Apply the latest SQL Server updates, enforce least-privilege access and MFA for administrative accounts, restrict network exposure, and monitor database logs for unusual privilege changes or suspicious activity.
|
Is AI Actually Helping Employee Burnout? |
Artificial intelligence is transforming security operations, but new research shows it isn’t easing the workload for security leaders.
A report from Seemplicity found that many security leaders now average more than 10 hours of overtime each week while also managing new responsibilities tied to AI governance. As AI automates technical tasks, security leaders are increasingly expected to interpret AI outputs and guide risk decisions — often without sufficient training to manage these complex systems.
Pair AI security tool deployments with structured training and clear governance policies so teams can manage automated systems without adding operational strain. |
|
|
Cybersecurity Burnout Check: How close are you to the edge? |
|
|
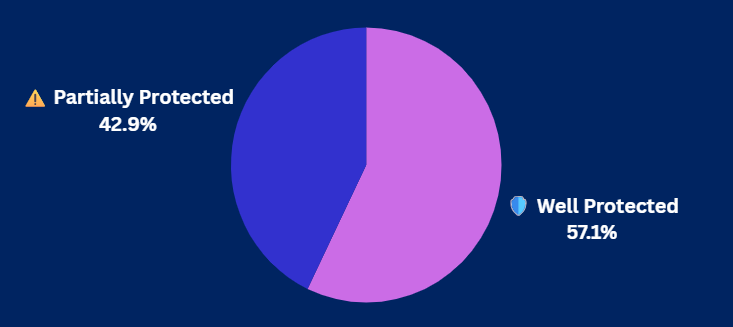
Yesterday's Pulse Check Results |
Are your users protected from malvertising? |
|
|
Security Tools You Can Use |
|
|
Zoom Vulnerabilities Target Windows Users |
Zoom has disclosed multiple vulnerabilities in its Windows collaboration software, including a critical flaw that could allow remote privilege escalation on affected systems. The most severe flaw involves improper file path handling in the Zoom Workplace Mail feature and can be exploited remotely without authentication. |
Zoom has released patches for the vulnerability.
Patch to the latest version, enforce least-privilege access on endpoints, and monitor logs and endpoint activity for unusual Zoom-related behavior that could signal exploitation attempts. |
CyberProof Warns of AI-Powered Attacks |
Threat actors are increasingly relying on stolen identities and AI-powered automation instead of traditional malware to breach enterprise environments.
The CyberProof 2026 Global Threat Intelligence Report found compromised credentials accounted for 22% of breaches in 2025, highlighting the growing role of identity compromise in modern attacks.
Deploy phishing-resistant MFA and continuously monitor authentication activity with identity threat detection tools to quickly spot suspicious logins, privilege changes, or abnormal MFA resets. |
|
|
You’re busy running your business — and so are cybercriminals, using many of the same tools, processes, and tech. Step inside the day-to-day operations of modern cybercrime groups, see how they mirror legitimate enterprises, and gain practical insight into how attackers think so you can spot and disrupt them faster. |
|
|
How Secure Is Your SQL Server Environment? |
SQL Server systems often store sensitive business data and support critical applications, making them attractive targets for threat actors. When permissions are misconfigured, patches are missing, or database services are exposed, the risk of unauthorized access increases. |
How to harden your SQL Server environment: |
-
Regularly apply patches and enforce least-privilege roles so only authorized accounts can perform administrative actions.
- Use Windows authentication with MFA and place SQL Server behind firewalls, allowing connections only from trusted systems.
-
Enable auditing and logging to detect suspicious behavior and use encryption such as TDE to secure data at rest.
|
Hardening SQL Server with proper access controls, monitoring, and regular patching helps reduce the risk of unauthorized access and protects sensitive data. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|