The weak points aren’t always where you expect them. |
Today’s stories span leaked consumer data, trusted tools turned risky, proxy networks hiding in plain sight, and shifting dynamics in cyber collaboration.
Each points to the same question: where does your next blind spot live? Read past newsletters here. |
|
| Here’s what you need to know: |
|
|
ShinyHunters Allege Theft of 14M Panera Bread Records |
The ShinyHunters group claims it has stolen roughly 14 million Panera Bread customer records and listed the company on its data leak site. If confirmed, the exposed data includes basic customer details that can enable phishing, identity fraud, and account takeovers. |
Panera Bread is still investigating the claims.
Require phishing-resistant MFA on all SSO logins and train employees to verify any IT or helpdesk requests before approving authentication prompts. |
Google Targets IPIDEA Proxy Infrastructure |
Google moved to disrupt one of the world’s largest residential proxy networks by targeting IPIDEA’s proxy services and monetization SDKs. The network allegedly routed malicious traffic through millions of consumer devices, helping attackers evade IP-based defenses and power botnets and abuse campaigns. Move beyond IP blocking by enforcing MFA and monitoring identity and behavior signals to detect residential proxy–backed attacks early. |
Cal.com Bugs Expose Millions of Bookings |
Gecko Security researchers disclosed access control flaws in Cal.com that could enable account takeovers and expose millions of private bookings across organizations.
Because Cal.com underpins sales, recruiting, and executive workflows, a single compromised account can expose meeting data, integrations, API keys, and OAuth tokens. The researchers showed POCs, but there are no reports of exploitation in the wild.
Patch Cal.com to version 6.0.8+, enforce MFA, and audit logs and credentials to quickly spot and contain account takeover attempts. |
|
|
What’s your weakest third-party link? |
|
|
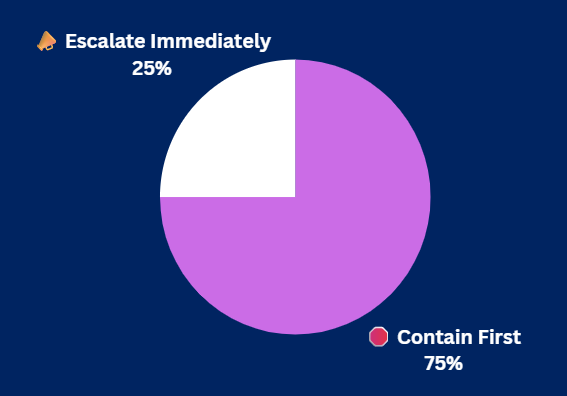
Yesterday's Pulse Check Results |
Data stolen, but no ransomware — what’s your first move? |
|
|
Security Tools You Can Use |
|
|
OpenSSL Vulnerabilities Expose RCE Risk |
OpenSSL issued emergency patches after AISLE researchers uncovered multiple vulnerabilities, including a high-severity remote code execution flaw. Because OpenSSL underpins core security across web, VPN, email, and certificate systems, parsing flaws can have widespread impact. |
The researchers found long-standing flaws in how OpenSSL handles untrusted cryptographic data, including a high-risk issue that could trigger pre-authentication stack overflows in CMS and PKCS#7 processing.
Patch all OpenSSL instances — including embedded libraries — and minimize risk by restricting untrusted crypto parsing and isolating it in least-privileged environments. |
RSAC Loses CISA, FBI, NSA Participation |
Several U.S. federal cyber agencies will not participate in RSAC 2026, removing a long-standing forum for informal government–industry engagement.
The withdrawal matters because RSAC has long supported direct government–industry collaboration, and security leaders warn that canceled sessions and leadership changes could weaken trusted coordination channels as critical infrastructure risks grow. I’ll be attending RSAC this year — reply to this email if you’ll be there and want to connect.
Proactively strengthen ties with ISACs and formal information-sharing programs to offset reduced access to federal partners at major conferences. |
|
|
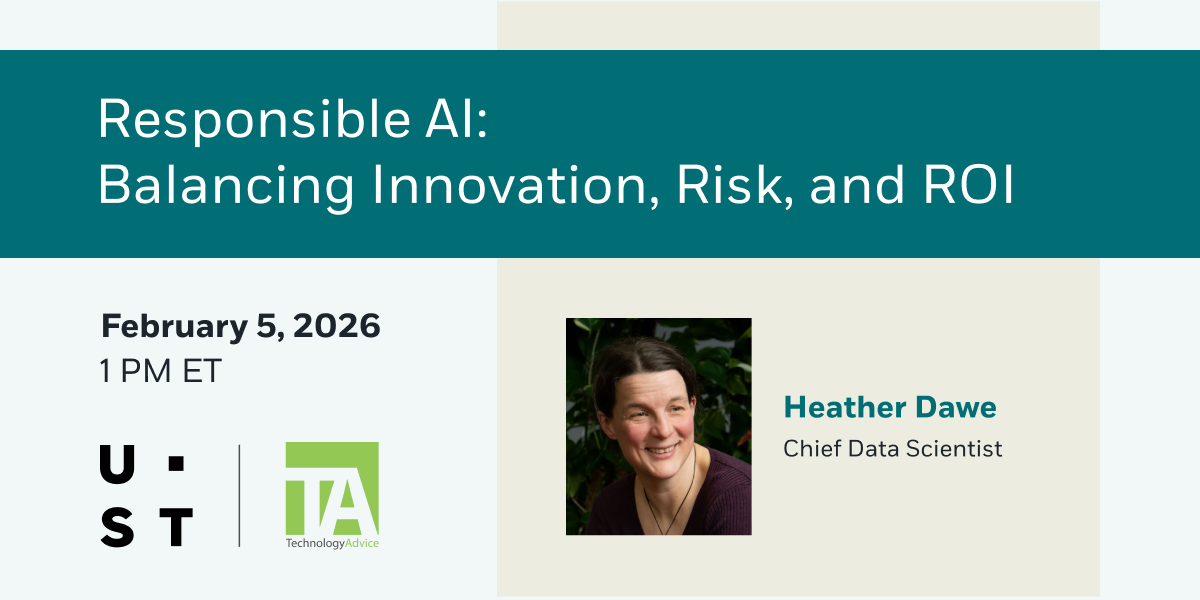
Scaling AI without governance increases risk and uncertainty.
On February 5 at 1:00 PM ET, TechnologyAdvice and UST explore how enterprises embed responsible AI to unlock value safely. Strengthen your AI foundation. |
|
|
Is your threat intel signal or just noise? |
Threat intelligence data continues to grow in volume, yet many security teams struggle to convert raw feeds into actionable insights. Without clear processes, intelligence can become difficult to prioritize, slowing response efforts and allowing avoidable risks to persist. |
How to turn threat intelligence into action: |
-
Focus threat intelligence on what matters most to your industry and environment, and continuously tune feeds and priorities as risks and adversary tactics evolve.
-
Integrate threat intelligence tools and feeds directly into SIEM, SOAR, EDR, and response workflows so indicators drive detections, automation, and action.
- Enrich, validate, and correlate intelligence with internal telemetry to reduce false positives and translate insights into effective controls and playbooks.
|
Effective threat intelligence focuses on relevance and continuous tuning to drive faster decisions, earlier detection, and more efficient response without overwhelming security teams. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|