Trust is being tested across the stack. |
From silent OS bypasses and weaponized collaboration tools to billing scams and sweeping privacy crackdowns, this week’s stories reveal how quickly familiar systems can turn into pressure points… often without warning.
Read past newsletters here. |
|
| Here’s what you need to know: |
|
|
macOS Vulnerability Breaks Core Privacy Protections |
A newly disclosed macOS vulnerability lets attackers silently bypass TCC protections to access sensitive user data.
The flaw allows abuse of trusted services like VoiceOver to execute AppleScript and AppleEvents. This grants access to protected data without administrative privileges, and proof-of-concept code is already available in the wild. |
Source: BoliviaInteligente/Unsplash |
Apple has released a patch for the issue.
Immediately upgrade macOS systems to 26.2+, lock down accessibility and admin privileges, monitor AppleScript and AppleEvent activity, and validate incident response readiness through regular testing. |
Zoom Bug Enables Windows Privilege Escalation |
Windows users face increased risk after a critical Zoom vulnerability was exploited to escalate privileges and steal sensitive data.
The flaw has a CVSS score of 9.6 and affects multiple Zoom products on Windows. It allows attackers to abuse trusted DLL loading for privilege escalation. Zoom has released a patch that fixes the issue by enforcing absolute DLL paths, but systems running versions below 6.3.10 remain vulnerable.
Immediately update all Zoom installations on Windows, disable unnecessary admin privileges, and ensure automatic updates are enabled across the organization. |
NordVPN Disputes Hacking Claims |
Recent claims that NordVPN suffered a data breach sparked concern after a threat actor alleged they had stolen multiple databases from a development server.
NordVPN told BleepingComputer the data came from an isolated third-party test environment containing only dummy information that was never connected to production and has since been decommissioned.
Secure test environments by isolating them from production, using only synthetic data, enforcing least-privilege credentials with MFA, and applying the same monitoring and governance controls as live systems. |
|
|
If an attacker landed in your test environment today… |
|
|
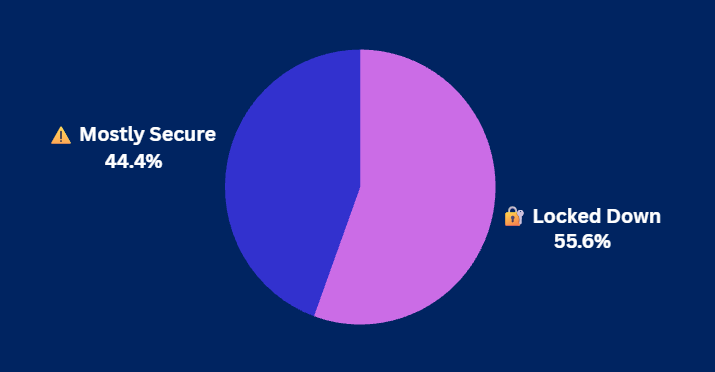
Yesterday's Pulse Check Results |
Mail Server Reality Check: How exposed are you right now? |
|
|
Security Tools You Can Use |
|
|
WordPress Admins Targeted by Renewal Scam |
A new phishing campaign targets WordPress administrators with fake renewal emails that steal credit card data and 2FA codes.
The attack targets billing workflows, creating direct financial risk and enabling broader account compromise. It uses fake WordPress payment portals and 3D Secure prompts to steal card data and OTPs via Telegram. |
This is an active campaign in the wild. Require admins to verify renewals only through official dashboards, enforce phishing-resistant MFA, harden email controls, and monitor billing activity. |
California Targets Data Brokers With DROP Tool |
California has launched a first-of-its-kind platform allowing residents to request deletion of their personal data from 500+ data brokers with one submission.
The Delete Request and Opt-Out Platform (DROP), created under California’s Delete Act, centralizes consumer deletion requests and imposes strict compliance deadlines on data brokers. Brokers face daily fines starting in August 2026 for failing to process deletions on time. The platform marks a shift toward infrastructure-level enforcement with implications beyond California.
Organizations should inventory any relationships with data brokers now and assess whether downstream partners are prepared to meet DROP’s automated deletion and verification requirements. |
|
|
Service management should do more than improve efficiency, it should drive enterprise results. On January 21 at 1:00 PM ET, TechnologyAdvice and Freshworks explore how organizations are breaking down silos and building connected service experiences. Learn what modern service management looks like in practice. Be part of the solution, sign up today. |
|
|
Are Your Endpoints Properly Secured? |
Endpoints are a primary target for attackers, as widespread remote work, bring-your-own-device (BYOD) policies, and cloud-based tools have expanded the attack surface. Ransomware, phishing, and privilege-escalation incidents demonstrate how a single compromised endpoint can enable broader network access. |
How to strengthen endpoint security defenses: |
- Enforce strong identity and access controls by limiting admin privileges and using phishing-resistant MFA to prevent credential abuse and privilege escalation.
-
Reduce endpoint attack surface by keeping systems fully patched and restricting execution from user-writable locations.
-
Improve detection and response by deploying EDR/XDR and centralizing endpoint logging to identify and contain malicious activity.
|
Strong endpoint security can help lower attacker dwell time and reduce the blast radius. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2026 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|