The attack surface keeps expanding. |
This week’s stories span courtroom fallout, physical-world hacks, stealthy browser malware, space agency intrigue, and nation-state tradecraft. Read past newsletters here. |
|
| Here’s what you need to know: |
|
|
Cognizant Hit With Lawsuits After TriZetto Breach |
Cognizant faces multiple class-action lawsuits after a nearly year-long, undetected data breach at its TriZetto healthcare subsidiary exposed sensitive personal information. The breach affected individuals in multiple states and exposed Social Security numbers, financial data, and home addresses. |
The outcome of the litigation is pending.
Continuously monitor for anomalies, lock down access with least privilege and MFA, encrypt sensitive data, and conduct third-party risk assessments. |
Bluetooth Hacks Now Target Electric Wheelchairs |
A critical Bluetooth flaw could allow nearby attackers to remotely control WHILL electric wheelchairs, posing serious safety risks.
The vulnerability affects multiple WHILL wheelchair models and could allow unauthorized movement or configuration changes without user interaction. The company has released updates to fix the issue.
Keep devices updated, require authenticated Bluetooth pairing, restrict unsafe commands, harden wireless access, and train users. |
8.8M Browsers Hit in DarkSpectre Extension Campaign |
Researchers uncovered DarkSpectre, a long-running malware campaign that infected over 8.8 million Chrome, Edge, and Firefox users via malicious browser extensions. The campaign shows how trusted browser marketplaces can be abused at scale through legitimate-looking features and long-term evasion. The threat actor group is still running campaigns in the wild.
Audit extensions, centrally manage browsers, monitor for anomalous behavior, apply zero-trust principles, strengthen identity protections, and conduct threat hunting. |
|
|
How confident are you in your wireless defenses? |
|
|
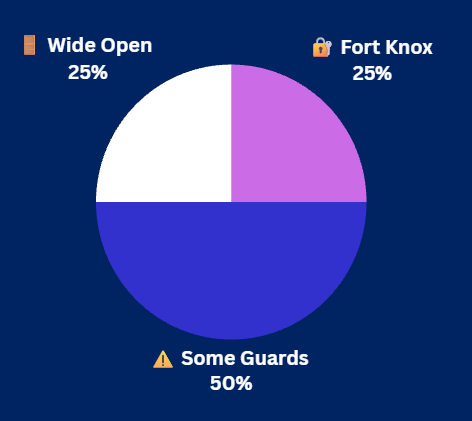
Yesterday's Pulse Check Results |
How locked down are your API connections? |
|
|
Security Tools You Can Use |
-
Help shape the future of AI security in autonomous vehicles — take the survey.
- Equip your team with security tools built to keep pace with modern attack techniques.
-
Build your own AI-driven bot using ChatGPT, Python, and Django — save 42% today.
|
|
|
Hacker Claims 200GB Data Theft From European Space Agency |
The European Space Agency is investigating a cyber incident after a hacker claimed to steal roughly 200 GB of data from external collaboration servers. Impacted systems support scientific and engineering collaboration, potentially exposing researchers and partners. |
The investigation is ongoing.
Treat external collaboration platforms as high-risk assets, monitor, and regularly test segmentation, access controls, and logging. |
APT36 Hits Indian Government With Malicious Windows Shortcuts |
A suspected nation-state actor is targeting Indian government entities using malicious Windows shortcut files disguised as PDFs. The campaign abuses trusted file types and native Windows tools to bypass defenses and deliver fileless malware. This is an active campaign in the wild. Block risky LNK files, harden email filtering, deploy EDR for fileless threats, monitor outbound traffic, and train users. |
|
|
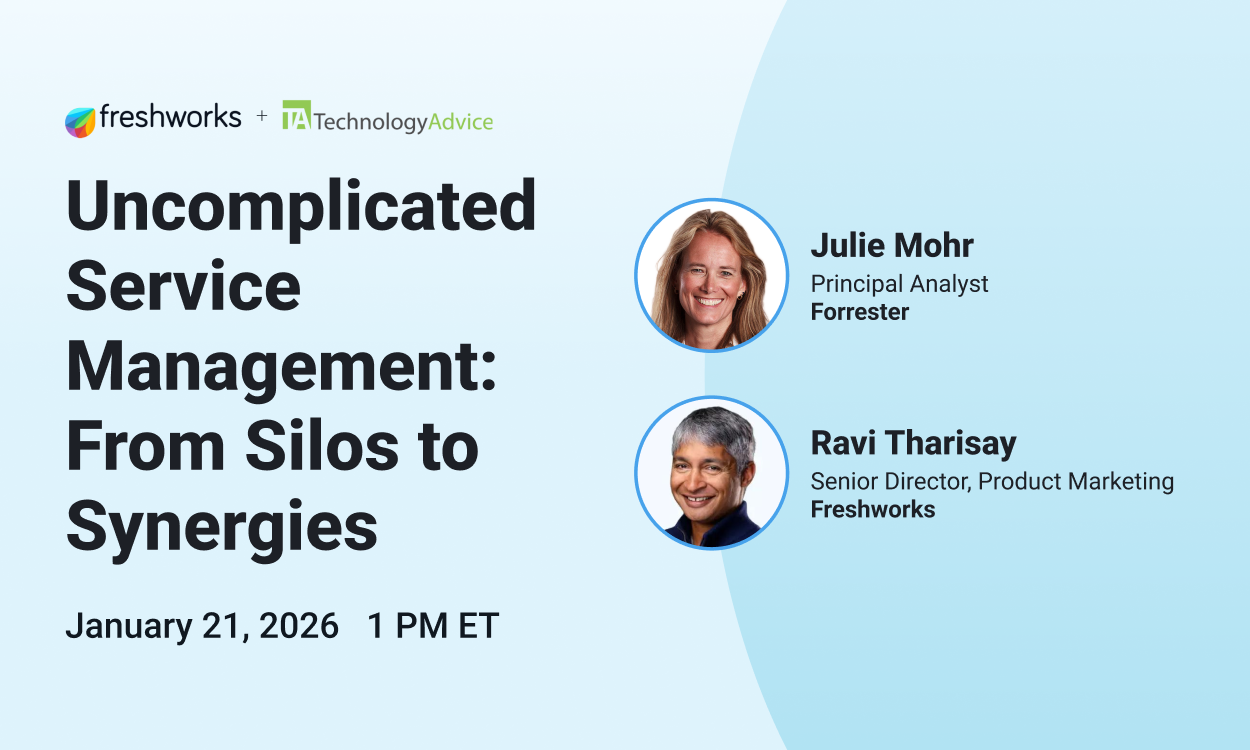
Service management should do more than improve efficiency, it should drive enterprise results. On January 21 at 1:00 PM ET, TechnologyAdvice and Freshworks explore how organizations are breaking down silos and building connected service experiences. Learn what modern service management looks like in practice. Be part of the solution, sign up today. |
|
|
How Exposed Is Your Cloud Data Right Now? |
As organizations accelerate cloud adoption, misconfigurations, excessive access, and poor visibility continue to expose sensitive data to attackers. Cloud platforms shift security responsibility, making it easy for gaps in identity, storage, or monitoring controls to lead to large-scale data exposure if not actively managed. |
How to protect sensitive data in cloud environments: |
- Enforce strong identity and access controls by combining least privilege, multi-factor authentication, and segmentation to limit unauthorized access and blast radius.
-
Protect cloud data with encryption at rest and in transit, while using CSPM tools to continuously monitor for misconfigurations that could expose sensitive resources.
-
Maintain visibility and response readiness through centralized logging, auditing, and monitoring to quickly detect and investigate suspicious activity.
|
Effective cloud data protection requires a layered approach that combines strong identity controls, continuous visibility, and automated enforcement rather than relying on traditional perimeter-based defenses. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|