Hidden risks are surfacing across systems. |
Today’s stories show how small missteps and trusted tech — from enterprise servers to AI agents and wearables — are quietly being exploited. 👉 Help make the newsletter better for you in 60 seconds. |
|
| Here’s what you need to know: |
|
|
Misconfigured CRM Exposes 140K Childcare Records |
A misconfigured database at a popular childcare CRM exposed more than 140,000 sensitive parent and child records online. The data tied families to specific U.S. childcare centers, heightening risks of phishing, impersonation, identity fraud, and long-term privacy harm to minors. |
The database has since been secured, but it’s unclear if threat actors were able to harvest the data. Reduce data exposure risk by locking down databases, enforcing least-privilege access, continuously auditing configurations, and holding third-party platforms to strict security and notification standards. |
Microsoft Patch Breaks MSMQ on Windows Servers |
Microsoft’s December 2025 security update caused widespread enterprise outages by breaking MSMQ across multiple Windows platforms. MSMQ supports many business-critical applications, and systems running Windows Server 2016, Server 2019, and Windows 10 22H2 are seeing queue failures soon after patching.
At the time of writing, Microsoft has not released a fix for the issue. Pause deployment of KB5071546 in production MSMQ environments and test permission changes in staging before applying the December patches broadly. |
Cisco Flags Active Exploitation of Email Zero-Day |
Cisco issued an urgent warning after confirming a Chinese state-linked group is exploiting a zero-day in its email security products to gain full administrative control. The flaw affects Cisco Secure Email Gateway and Secure Email and Web Manager worldwide, exposing sensitive email traffic. With no patch currently available and all AsyncOS versions affected, compromised appliances must be fully rebuilt to remove attacker access.
Immediately check whether Spam Quarantine is internet-exposed and isolate or rebuild affected appliances before attackers can further exfiltrate email data. |
|
|
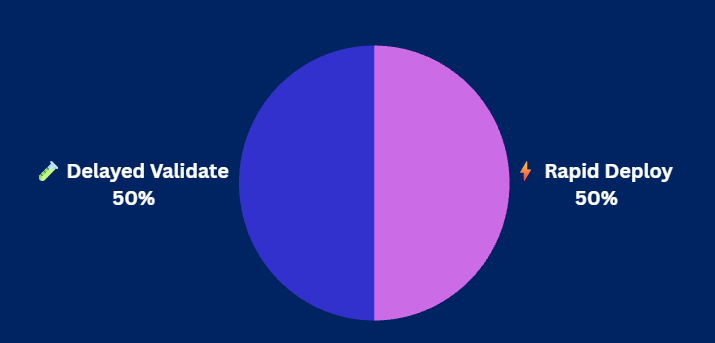
When a vendor update breaks production, what’s your move? |
|
|
Yesterday's Pulse Check Results |
When a critical zero-day drops, what actually happens first in your org? |
|
|
Security Tools You Can Use |
|
|
Attackers Target AI Agents in Enterprises |
Lakera researchers found that attackers exploited early AI agent capabilities in Q4 2025, expanding the enterprise attack surface. Even lightweight agents that browse data or call tools are opening new paths for prompt leakage, safety bypasses, and indirect attacks. |
Source: Growtika/Unsplash |
As AI agents move into production, weak trust boundaries and data ingestion controls risk exposing sensitive systems at scale.
Secure AI agents by enforcing least privilege, validating external inputs, monitoring agent behavior, and applying security controls across every step of the agent workflow. |
Old Blinkenlights Trick Breaks Smartwatch Security |
Researchers showed that a decades-old exfiltration technique can still compromise modern embedded devices, extracting firmware from a low-cost smartwatch via screen output.
Low-cost IoT and wearables often enter enterprise, healthcare, and supply-chain environments without thorough security review, expanding risk beyond traditional IT assets. Quarkslab researchers showed that a single parsing flaw could turn a smartwatch display into a covert memory leak — without Bluetooth exploits or debug access — using inexpensive hardware.
Reduce embedded device risk by enforcing secure-by-design firmware, isolating devices on the network, monitoring for anomalies, and applying strict procurement and lifecycle controls. |
|
|
What Risks Are Hiding in Your Embedded Devices? |
Embedded and IoT devices are increasingly targeted as attackers revive old techniques and exploit simple flaws to extract sensitive data. From low-cost wearables to industrial systems, insecure firmware, weak parsing logic, and poor isolation can turn overlooked devices into serious enterprise risks. |
How to secure embedded and IoT devices: |
- Design embedded systems with secure-by-design controls, including strict input validation, hardened parsers, and hardware-backed trust such as secure boot.
-
Secure firmware throughout its lifecycle by enforcing encrypted, signed updates and conducting continuous firmware testing, fuzzing, and threat modeling.
-
Reduce blast radius by isolating embedded devices on the network and enforcing procurement and lifecycle standards that prevent use of unsupported or insecure hardware.
|
Embedded devices are no longer low risk, and applying secure-by-design principles is essential to reduce exposure and maintain resilience as they proliferate across enterprise environments. |
|
|
| Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field.
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|