The attack surface is getting quieter — and more deceptive. |
Trusted tools are being abused, exploits are outpacing patches, and phishing is evolving… making identity, applications, and user trust the common thread this week.
👉 What should we cover more (or less) in the newsletter? Tell us in a 60-second survey. |
|
| Here’s what you need to know: |
|
|
Azure CLI Trust Abused in Microsoft Account Takeovers |
Security researchers uncovered a phishing technique that hijacks Microsoft accounts without stealing passwords or bypassing MFA. Known as ConsentFix, the attack abuses trusted Azure CLI OAuth flows and subtle user actions. |
This is an active campaign in the wild.
Monitor Azure CLI and directory activity for anomalies, tightly restrict CLI and OAuth permissions, and apply Conditional Access and least-privilege controls. |
Google Warns on Active React2Shell Exploitation |
Google warns attackers are actively exploiting a critical React vulnerability to take over unpatched servers without authentication. Tracked as CVE-2025-55182, React2Shell affects widely used React Server Components and Next.js, putting many internet-facing applications at immediate risk. A patch has already been released for the React2Shell vulnerability. Patch affected React and Next.js deployments, monitor for signs of exploitation, and use layered runtime and network controls to limit impact if compromise occurs. |
Windows Breached via Phantom Stealer ISO Lures |
Researchers found an active phishing campaign using ISO files to deliver Phantom Stealer to Windows while bypassing common defenses.
Dubbed Operation MoneyMount-ISO, the campaign uses financial lures to trick finance staff into opening malicious ISO files that auto-mount in Windows and enable credential theft, fraud, and lateral movement.
Block and inspect ISO attachments, disable auto-mounting, deploy EDR for in-memory threats, and limit privilege and outbound access to reduce Phantom Stealer risk. |
|
|
Where does your environment stand on React2Shell right now? |
|
|
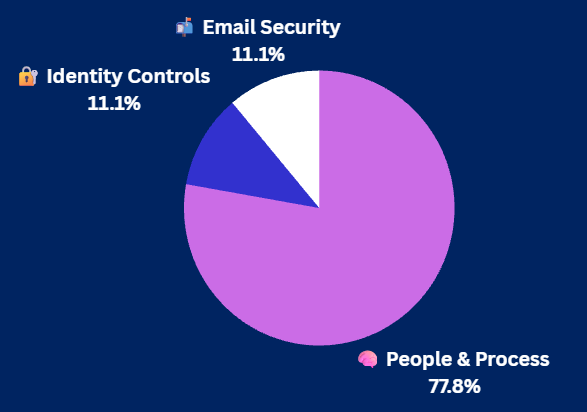
Yesterday's Pulse Check Results |
Spear Phishing Defense Check: What actually protects your org? |
|
|
Security Tools You Can Use |
-
Catch threats early and stop them from escalating into major incidents using the right security tools.
- Surface hidden risks now and address them before they become your next breach.
- Got a minute? Share what’s working (and what isn’t) in our quick DZone community survey.
|
|
|
SantaStealer Lands on Infostealer Naughty List |
Researchers are tracking SantaStealer, a new malware-as-a-service infostealer actively promoted on underground forums and Telegram. The malware steals credentials and sensitive data using mostly in-memory techniques that evade traditional detection, targeting common browsers and applications across enterprises and individual users.
|
Rapid7 researchers continue to monitor the new infostealer, but there is no known use in the wild yet. Keep endpoints and browsers hardened, block unauthorized execution, train users on infostealer lures, and enforce least privilege. |
AiTM Campaign Targets Microsoft 365 and Okta |
An active adversary-in-the-middle (AiTM) phishing campaign is bypassing multi-factor authentication to compromise Microsoft 365 and Okta accounts. Instead of stealing passwords, attackers hijack live authentication sessions to bypass MFA, which indicates a strong understanding of modern SSO flows. Monitor identity logs for suspicious session behavior, deploy phishing-resistant MFA, tighten Conditional Access and email controls, and aggressively limit session scope and privilege. |
|
|
How Secure Is Your Identity Stack? |
Modern attacks increasingly target identity systems rather than endpoints, abusing trusted login flows, OAuth permissions, and session tokens to bypass traditional defenses. As cloud identity platforms centralize access to critical systems, small gaps in identity controls can quickly lead to widespread compromise. |
How to lock down your identity security: |
- Use phishing-resistant MFA with Conditional Access to enforce device trust, location checks, and risk-based sign-in controls.
- Apply least-privilege access and strong OAuth app governance to limit what compromised users or apps can access.
-
Centralize identity logs and monitor sessions and tokens to detect anomalous behavior early.
|
Strong identity security focuses on visibility and control, helping organizations limit attack impact by tightening access, monitoring behavior, and reducing implicit trust.
|
|
|
| Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field.
|
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|