The cyber winds are shifting again, Digital Defenders. |
This week brings silent browser flaws, hijacked OAuth pathways, supply-chain breaches, and a stealthy Android trojan slipping past every scanner. Even holiday shoppers aren’t spared. |
|
|
Here’s what you need to know: |
|
|
Firefox Memory-Flaw Bug Exposed Millions to Silent Risk |
A newly uncovered Firefox vulnerability left more than 180 million users exposed to potential code execution for nearly six months. Researchers at Aisle uncovered a subtle WebAssembly memory flaw in Firefox that could overflow the stack and corrupt nearby data. |
Source: appshunter/Unsplash |
Mozilla has released a patch for the issue.
Update to the latest version of Firefox, monitor for WebAssembly anomalies, and use network and endpoint controls to contain high-risk browsing until all systems are fully patched. |
Salesforce Probes OAuth Breach Tied to Gainsight Apps |
Salesforce is investigating suspicious activity in Gainsight apps that may have exposed customer data through compromised OAuth tokens.
The company revoked all tokens and pulled the affected apps, stressing the issue isn’t a Salesforce platform flaw. ShinyHunters claimed responsibility and threatened further OAuth-based attacks in the Salesforce ecosystem. This is an ongoing investigation. Audit and rotate all connected-app credentials and OAuth tokens as a precautionary hardening step. |
SitusAMC Breach Puts Major Financial Institutions at Risk
|
A breach at SitusAMC exposed sensitive accounting records, legal agreements, and customer data from over 100 major financial institutions, including JPMorgan Chase, Citi, and Morgan Stanley.
SitusAMC says attackers accessed internal systems on Nov. 12 and stole client-related documents that may include architecture diagrams, system details, and contractual data useful for follow-on attacks. This is an ongoing investigation.
Immediately rotate all credentials and API keys shared with SitusAMC, and audit network logs for any authentication or data-access anomalies. |
|
|
How confident are you in your third-party data controls? |
|
|
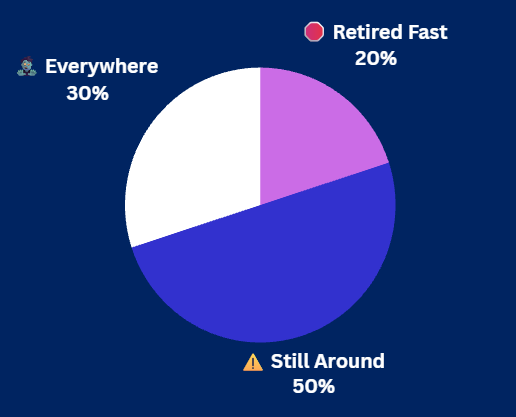
Yesterday's Pulse Check Results |
How are outdated devices handled in your org? |
|
|
Security Tools You Can Use |
|
|
New RadzaRat Android Trojan Evades All Antivirus Detection |
A new Android trojan called RadzaRat is spreading with full surveillance and remote-control capabilities — yet it still shows zero detections across all 66 VirusTotal scanners.
Certo researchers found that RadzaRat poses as a simple file manager while stealing large data sets, keylogging through abused Accessibility permissions, and maintaining persistence via boot receivers and foreground services. |
Source: Denny Müller/Unsplash |
Its public GitHub distribution makes it easy for even low-skill operators to deploy — creating immediate risk for unmanaged or BYOD Android environments.
Lock down high-risk permissions, block sideloading, enforce MDM controls, and use mobile threat defense to spot anomalies while isolating work data and tightening BYOD monitoring. |
Five Practical Ways to Shop Online Safely This Holiday Season |
Online shoppers are facing a surge in scams this holiday season as attackers spin up fake stores, spoof delivery alerts, and push too-good-to-be-true ads. Experts warn that criminals rely on rushed decisions and FOMO, making distracted buyers an easy target.
Matt Chmel, Head of Cyber for North America at Aon, advises consumers to slow down, verify retailers, and stay alert to impersonation attempts — especially bogus delivery texts and phishing messages. Shop through official apps or manually typed URLs — never ad links — to avoid spoofed storefronts and credential-harvesting scams. |
|
|
Live from the floor at AWS re:Invent—AWS experts and AWS Partners tackle real-world cloud security challenges. |
|
|
Protect Your Home Network |
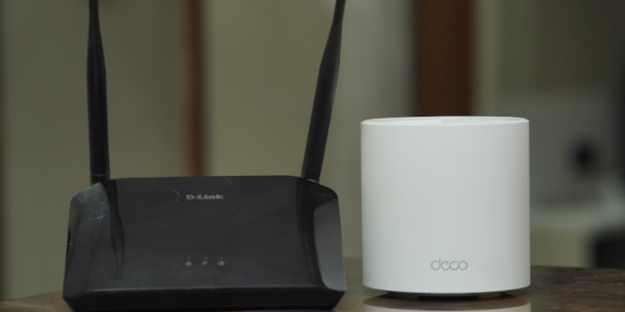
Cybercriminals are increasingly targeting home networks as remote work, smart devices, and always-on connectivity create easy entry points. A compromised home router or insecure device can give attackers direct access to sensitive corporate data. |
Source: TechieTech Tech/Unsplash |
How to harden your home network: |
-
Change default router passwords and enable WPA3 encryption to block unauthorized access to your network.
- Turn on automatic firmware updates and disable unnecessary remote access to reduce your attack surface.
-
Use a guest network and DNS filtering to isolate devices and prevent connections to malicious sites.
|
Strengthening your home network doesn’t always require complex tools — just consistent, proactive habits. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|