The cyber underground didn’t slow down this week, Digital Defenders. |
From ERP backdoors to weaponized lost phone alerts, dormant package swarms, billion-dollar phishing engines, and global scam rings under federal fire… cyber threats are evolving at record speed. |
|
|
Here’s what you need to know: |
|
|
SAP Emergency Patch Fixes Critical System-Takeover Flaw |
SAP’s latest security update includes an emergency fix for a Solution Manager vulnerability that lets unauthenticated attackers inject and execute arbitrary code.
The Solution Manager flaw (CVE-2025-42887) stems from an unsanitized remote-enabled function module, exposing SAP’s central management hub to takeover. |
Source: Kittyfly/Shutterstock |
SAP has released patches for the vulnerabilities.
Apply the latest SAP patches, lock down SolMan access, monitor for anomalies, and regularly audit accounts and configurations. |
Fake Find My Messages Target Lost iPhones in New Scam |
Switzerland’s NCSC warns that scammers are stealing Apple IDs by targeting users immediately after they lose their iPhones. After a device goes missing, attackers send convincing fake Find My messages with real device details to trick victims into entering their Apple IDs on spoofed sites. Compromised Apple IDs let threat actors bypass Activation Lock and access sensitive data. Instruct employees to ignore all “device found” messages and initiate Lost Mode only through official Apple sites — never through links received by email or SMS. |
How 43,000 NPM Spam Packages Evaded Detection for Years |
A newly uncovered campaign injected over 43,000 dormant packages into npm, marking one of the largest supply-chain spam incidents to date.
Researchers found the IndonesianFoods worm used randomized names, legitimate-looking templates, and dormant payloads to blend into npm. This is an ongoing issue. Audit your environment for packages from the affected npm accounts and deploy SCA tools that detect dormant files and suspicious dependency structures. |
|
|
If your phone vanished right now… what’s the real risk? |
|
|
Yesterday's Pulse Check Results |
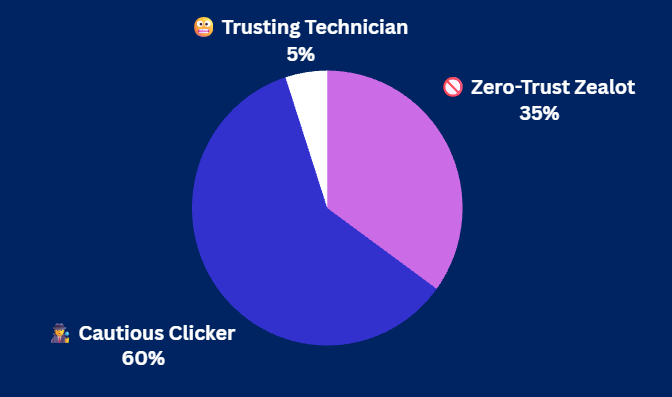
Update Instinct Test: Would you fall for a fake app update? |
|
|
Security Tools You Can Use |
|
|
U.S. Forms Strike Force to Disrupt Global Crypto Scam Networks |
A new federal Strike Force has been launched to dismantle the sprawling “pig-butchering” scam operations driving billions in global cryptocurrency fraud.
The initiative unites the DOJ, Treasury, FBI, Secret Service, and other agencies in a coordinated campaign targeting transnational crime groups running industrial-scale fraud compounds across Southeast Asia. |
Source: Katie Moum/Unsplash |
The Strike Force has ongoing operations against the target groups.
Review your organization’s crypto-related touchpoints and ensure partners undergo enhanced due-diligence screening against OFAC, FinCEN, and DOJ enforcement alerts. |
Google Sues China-Based Phishing Network Behind $1B Global Scam |
Google has filed a major lawsuit against a China-based group behind Lighthouse, a phishing-as-a-service platform tied to over $1 billion in global fraud. The platform gives scammers subscription access to thousands of brand-spoofing templates, enabling large-scale email, SMS, and website phishing attacks. Google’s lawsuit seeks to dismantle the network under US racketeering and computer fraud laws. Enforce rapid enterprise passkey adoption and disable password-only authentication wherever possible to neutralize credential-theft phishing. |
|
|
How Can You Protect Users From Scams? |
Scams are evolving faster than ever, blending social engineering, device impersonation, and AI-assisted tactics to trick even vigilant users. |
Simple steps to shield your users from today’s scams: |
-
Enable strong authentication like MFA or passkeys to block credential-theft attempts.
- Verify URLs and limit lock-screen information to reduce data exposure.
- Use modern message filtering and report suspicious activity quickly.
|
Together, these simple habits create a stronger, more resilient defense that helps users avoid scams and keeps your organization safer. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|