The cyber front lines are heating up, Digital Defenders. |
This week brings trusted tools turned traitors — Meta’s inbox exploited, AppleScript updates gone rogue, and Androids wiped clean by state hackers. |
|
|
Here’s what you need to know: |
|
|
Phishing Campaign Abuses Meta Business Suite to Target SMBs |
Cybercriminals are hijacking Meta’s Business Suite to send convincing phishing emails from the legitimate facebookmail[.]com domain.
Check Point researchers uncovered the global phishing campaign using fake Meta Business pages and Facebook’s own invitation system to send fraudulent “Account Verification” and “Partner Invitation” emails. |
This is an active campaign in the wild. Train users regularly, deploy AI-driven email defenses, enforce MFA, and verify all Meta links through official channels to prevent account compromise.
|
Hackers Use AppleScript to Disguise Fake macOS App Updates |
Researchers found macOS malware campaigns using fake AppleScript updates to trick users into running malicious code that bypasses Gatekeeper protections.
Once run, the scripts quietly install malware behind fake update dialogs — a growing trend of attackers weaponizing trusted macOS features. These campaigns are active in the wild. Restrict AppleScript execution, verify updates only from official sources, and use EDR tools to detect suspicious script activity. |
Ivanti Patches Critical Endpoint Manager Flaws Allowing File Tampering |
Ivanti has released fixes for multiple Endpoint Manager vulnerabilities that could let authenticated users write arbitrary files and gain elevated privileges.
The most critical flaw, CVE-2025-10918, caused by insecure default permissions in older agents, lets local attackers modify system files, plant backdoors, or escalate privileges. Ivanti reported that they are not aware of the vulnerabilities being exploited in the wild.
Enforce least privilege, deploy EDR tools, and maintain strict patching and access controls to prevent local privilege escalation. |
|
|
Update Instinct Test: Would you fall for a fake app update? |
|
|
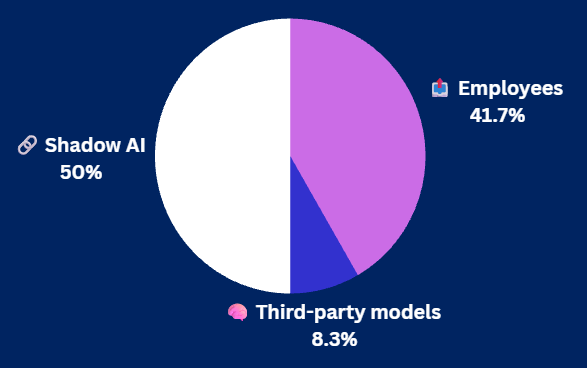
Yesterday's Pulse Check Results |
What’s your biggest AI data leakage worry right now? |
|
|
Security Tools You Can Use |
|
|
North Korean Hackers Exploit Google Find Hub to Wipe Androids |
Researchers uncovered a KONNI-linked campaign where North Korean hackers use Google’s Find Hub to remotely wipe Android devices.
After stealing Google credentials, attackers used legitimate reset features to wipe devices, disrupt communications, and hide surveillance — marking the first known case of a state actor weaponizing Google’s management tools. |
This is an ongoing campaign in the wild. Enable MFA, use EDR and MDM tools, and require verification for remote actions to prevent unauthorized device wipes and account compromise. |
People Remain Cybersecurity’s Strongest — and Weakest — Link |
“Humans are still the last, most important linchpin in security, and we need to keep that pretty clearly in line of sight as we try to make sure that our organizations are safe,” said LevelBlue CIO Maria Cardow.
She warned that focusing on tools over people ignores behaviors and shadow AI use that weaken defenses, stressing that true security starts with understanding human motives, not just enforcing controls. Treat humans as assets and not just liabilities, invest in continuous security awareness, empower teams with sanctioned AI tools, and include behavioral insight in every security strategy. |
|
|
When Layer 8 Fails: Strengthen Human Error Defenses |
Even the strongest security stack can crumble when the human layer — Layer 8 — fails.
From accidental clicks to shadow AI use, people remain both the greatest risk and the greatest defense. As social engineering grows more sophisticated, organizations must prepare for inevitable mistakes with resilient, layered protection. |
How to stay secure when humans make mistakes: |
-
Use intelligent monitoring and adaptive access controls to detect unusual user behavior, limit privilege escalation, and reduce the impact of human error.
-
Strengthen human awareness and readiness through ongoing phishing simulations, realistic training, and clear incident response playbooks.
- Adopt modern authentication and prevention tools like passwordless logins and AI-driven email filters to block threats before they reach users.
|
By combining smart technology with practical, behavior-aware controls, organizations can turn human error from a single point of failure into a recoverable event. Cyber resilience isn’t perfection — it’s readiness when Layer 8 slips. |
|
|
|
Ken Underhill is an award-winning cybersecurity professional, bestselling author, and seasoned IT professional. He holds a graduate degree in cybersecurity and information assurance from Western Governors University, bringing years of hands-on experience to the field. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|