The cloud’s showing cracks, Digital Defenders |
Today’s headlines bring a global AWS blackout, a fintech breach exposing millions, ransomware at record highs, and fresh whispers of state-sponsored spying. |
|
|
Here’s what you need to know: |
|
|
Global AWS Outage Takes Down Major Platforms |
A widespread Amazon Web Services (AWS) outage early Monday knocked major platforms like Snapchat, Canva, Roblox, and Duolingo offline for hours. The disruption, traced to DNS and API failures in the US-EAST-1 region, even affected Amazon’s own retail and Ring systems. |
The incident highlights how deeply the internet depends on a few US-based cloud providers — AWS, Microsoft Azure, and Google Cloud — who control most of the global market. IT leaders should review their disaster recovery playbooks and consider multi-cloud or hybrid architectures to maintain uptime when a dominant provider stumbles. |
Prosper Breach Exposes Data of 17.6 Million Users |
Have I Been Pwned (HIBP) has logged 17.6 million victims linked to a September cyberattack on peer-to-peer lender Prosper, though the company says it cannot yet verify the figure.
Reports suggest that email addresses, government IDs, and financial data, including income and credit status, were exposed. Prosper says that customer funds remain safe and that an investigation is still ongoing. If confirmed, the scale would make this one of 2025’s largest financial sector breaches, spotlighting the persistent risk facing fintech platforms that handle troves of personal and credit data.
Integrate breach-monitoring and dark web feeds directly into incident response workflows to detect possible exposure early. |
Ransomware Attacks Surge 36% as Q3 Sets New Record |
The latest BlackFog Q3 2025 Ransomware Report reveals a 36% year-over-year spike in ransomware incidents, marking the highest volume of attacks on record. Between July and September, 270 public cases were reported across 93 countries, with airlines, automakers, and government agencies among the hardest hit. Healthcare remained the top target, accounting for nearly one-third of all known breaches. Among undisclosed attacks, the manufacturing sector faced the highest concentration of incidents. Prioritize zero-trust controls, data-loss prevention, and egress monitoring to cut attackers off at their most profitable stage. |
|
|
Cloud Dependency Reality Check: How long could your business stay online? |
|
|
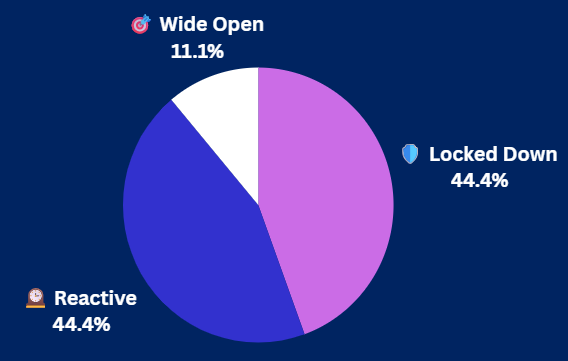
Yesterday's Pulse Check Results |
Third-Party App Security Check: How tight is your Adobe game? |
|
|
Security Tools You Can Use |
|
|
China Claims US Hacked National Time Center |
China’s Ministry of State Security accused the US National Security Agency (NSA) of breaching its National Time Service Center, alleging espionage that could have disrupted China’s communications, finance, and power systems.
The ministry said the NSA exploited a smartphone messaging vulnerability to infiltrate staff devices and target the center’s timing infrastructure between 2022 and 2024. |
Source: ran liwen/Unsplash
|
The US embassy in Beijing dismissed the claims, calling China the most “active and persistent” cyber threat to US networks — adding another flashpoint in US–China cyber tensions. Secure all mobile endpoints. Patch messaging apps promptly and restrict sensitive communications to vetted, encrypted platforms. |
Envoy Air Confirms Breach Linked to Oracle EBS Hack |
Hackers tied to the Cl0p ransomware group have struck Envoy Air, an American Airlines subsidiary, through vulnerabilities in Oracle’s E-Business Suite (EBS).
The attackers reportedly exfiltrated over 26 GB of data and listed American Airlines on their leak site, though the breach was traced back to Envoy’s Oracle systems. Envoy said only limited business info was affected, but other victims — including Harvard University and industrial giant Emerson — suggest the campaign is widespread and still unfolding.
Orgs using Oracle EBS should verify patch status for CVE-2025-61882 and CVE-2025-61884 and review vendor access controls before attackers do. |
|
|
Elevate Your AWS Identity Security Posture with Cisco Duo
Join Cisco Duo and AWS experts for a comprehensive webinar designed for security professionals and organizations from SMB to Enterprise. Learn how to build a robust, Zero Trust identity security framework for your AWS environment and beyond. |
|
|
Monitor the Dark Web for Early Breach Clues |
Data breaches don’t end when hackers steal your information — they often begin again on the dark web. Stolen credentials, customer data, and corporate secrets can circulate for months before detection.
Monitoring underground markets, like the dark web, gives security teams a critical early warning system, helping them detect leaks and act before attackers strike again. |
Source: Jefferson Santos/Unsplash
|
How to stay vigilant on the dark web: |
- Track exposed credentials: Use tools like Have I Been Pwned to check if employee or customer emails appear in known data breaches.
-
Set up continuous monitoring: Employ automated alerts to detect leaked credentials, sensitive files, or mentions of your organization in dark web spaces.
- Correlate with existing intelligence: Integrate dark web insights into your existing SIEM or threat intelligence workflows for faster validation and response.
-
Investigate suspicious activity: Assign analysts to review credible leaks or chatter that may indicate targeting of your brand, partners, or customers.
|
Dark web monitoring transforms reactive defense into proactive protection. By pairing automation with a clear response plan, organizations can spot stolen data before it’s weaponized and turn potential crises into manageable incidents. |
|
|
| Senior Staff Writer at TechnologyAdvice |
Luis Millares is a seasoned tech writer with broad experience reviewing consumer gadgets and enterprise software, offering clear, reliable insights across the latest in technology. |
|
|
Cybersecurity Insider is a TechnologyAdvice business |
© 2025 TechnologyAdvice, LLC. All rights reserved. |
TechnologyAdvice, 3343 Perimeter Hill Dr., Suite 215, Nashville, TN 37211, USA. |
|
|
|